A transit router connects network instances and forwards traffic between them within a region or across regions. You can configure routes on a transit router to control how traffic is forwarded between the connected network instances.
Cloud Enterprise Network (CEN) provides two editions of transit routers: Enterprise Edition and Basic Edition. Enterprise Edition is the recommended edition and provides the routing capabilities described in this topic. Basic Edition is a legacy edition that is supported only in Cloud Connect Network (CCN) regions. Read the section that matches the edition that you use.
How Enterprise Edition transit routers work
Connect network instances
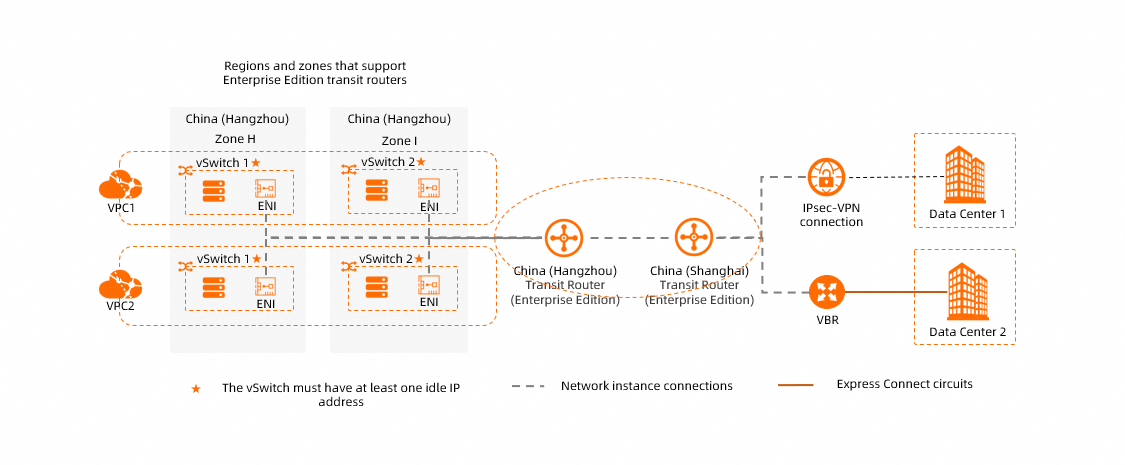
Enterprise Edition transit routers support the following network instances:
In regions where an Enterprise Edition transit router supports only one zone, before you connect a VPC to the transit router, make sure that the VPC has at least one vSwitch in that zone and that the vSwitch has an available IP address. When you connect the VPC, the Enterprise Edition transit router creates an elastic network interface (ENI) in the vSwitch of the VPC. The ENI occupies one IP address in the vSwitch and serves as the interface for traffic between the VPC and the Enterprise Edition transit router.
In regions where an Enterprise Edition transit router supports multiple zones, such as China (Hangzhou), before you connect a VPC to the transit router, make sure that the VPC has at least two vSwitches in zones supported by the Enterprise Edition transit router. The two vSwitches must be in different zones, and each vSwitch must have an available IP address. When you connect the VPC, the Enterprise Edition transit router creates an ENI in each of the two vSwitches. Each ENI occupies one IP address in its vSwitch and serves as the interface for traffic between the VPC and the Enterprise Edition transit router. The two vSwitches provide zone-level disaster recovery for the traffic.
For information about the regions and zones supported by Enterprise Edition transit routers, see Regions and zones supported by Enterprise Edition transit routers.
(Recommended) In regions where an Enterprise Edition transit router supports multiple zones, create a vSwitch in each supported zone for VPC connections. Each vSwitch must have an available IP address. This reduces traffic detours and provides lower transmission latency and higher performance for traffic between the VPC and the Enterprise Edition transit router. For more information, see Traffic transmission between a VPC and an Enterprise Edition transit router.
Routing
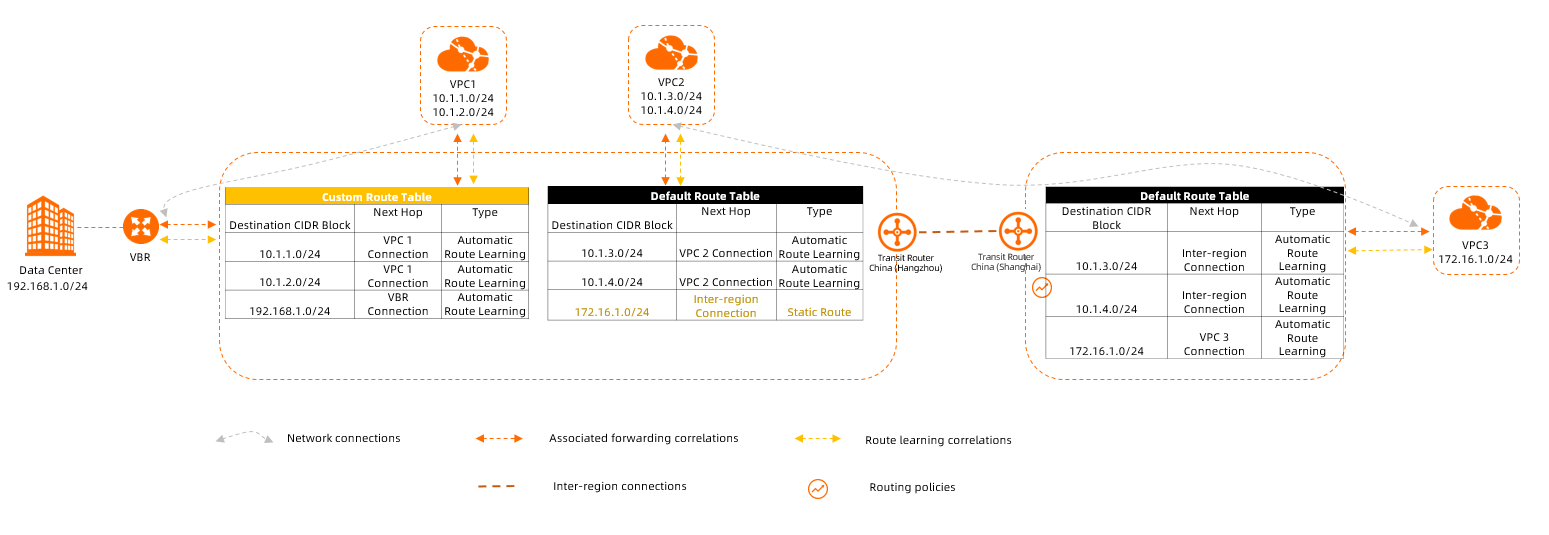
After an Enterprise Edition transit router connects to network instances, it stores the routes of the network instances in route tables. The Enterprise Edition transit router forwards network instance traffic by querying route entries in the route tables.
Each Enterprise Edition transit router has a system route table when it is created. You can create custom route tables for an Enterprise Edition transit router. System route tables and custom route tables are isolated from each other, which helps you implement access isolation.
Associated forwarding controls traffic forwarding for network instances. An Enterprise Edition transit router forwards network instance traffic by querying route entries in a route table only after the network instance connection has an associated forwarding relationship with that route table.
A network instance connection can have an associated forwarding relationship with only one Enterprise Edition transit router route table.
Route learning controls route propagation for network instances. Routes of a network instance can be propagated to an Enterprise Edition transit router route table only after the network instance connection has a route learning relationship with that route table.
You can establish a route learning relationship between a network instance connection and one or more Enterprise Edition transit router route tables. Each route table that has a route learning relationship with the network instance connection can learn the routes of that network instance.
Enterprise Edition transit router route tables support custom route entries. You can add custom route entries to an Enterprise Edition transit router route table to help control network instance traffic forwarding.
Default routing behavior
After an Enterprise Edition transit router connects to a network instance, it does not propagate any route entries to the network instance by default. You can use the Route propagation feature to control route propagation from the Enterprise Edition transit router to network instances.
Route priority
After traffic enters an Enterprise Edition transit router, the transit router matches route entries for the traffic according to the longest prefix match principle.
If multiple route entries with the same destination CIDR block exist in an Enterprise Edition transit router route table, the system first determines whether a route conflict exists:
If the route table already contains a static or dynamic route entry whose next hop is a VPC connection, a route entry for the same destination CIDR block learned from another network instance is considered conflicting.
If the route table already contains a dynamic route entry whose source is a VPC, a route entry for the same destination CIDR block learned from another network instance is considered conflicting.
If the route table already contains a static or dynamic route entry that is not sourced from a VPC, a route entry for the same destination CIDR block learned from a VPC is considered conflicting.
Workloads that communicate between two cloud VPCs differ from workloads that communicate between a cloud VPC and an on-premises network. For the same CIDR block, a cloud VPC and a cloud-to-on-premises network cannot form an active-standby or ECMP relationship.
When an Enterprise Edition transit router receives a route entry for the same destination CIDR block from another network, the route conflict rules limit the impact: communication fails only between the newly added network and the existing network. Traffic forwarding for existing workloads is not affected, so online workloads continue to run normally.
Adding network instances, such as the VPC in which an Elastic Compute Service (ECS) instance resides, to a CEN for connectivity does not adversely affect the ECS instance or the VPC network itself. Whether creating a CEN affects the VPC network depends primarily on whether route conflicts exist in the CEN route table:
If no conflicting routes exist in the CEN, existing VPC communication, including connections established through peering connections, operates normally. Traffic is forwarded along its original path and is not affected.
If route conflicts exist, the conflicting route entries are marked invalid. This may change route selection for VPC traffic and affect the corresponding network communication.
(Recommended) Before you add network instances to a CEN, check whether the CEN route table contains route entries with the same destination CIDR blocks as existing VPC routes. This prevents impacts on existing network communication for ECS instances and other instances.
For route entries whose destinations are on-premises and that do not cause route conflicts, priority is determined in the following order:
Static routes configured in an Enterprise Edition transit router route table — Static routes that you manually configure in the route table have the highest priority. They include custom route entries and prefix list route entries. If you configure both custom route entries and prefix list route entries, these route entries automatically form ECMP routes.
Dynamic routes — If route entries are not manually configured but are learned automatically by the transit router, they are matched in the following order:
Source instance type — Compare the source instance types of the route entries. Priority from high to low is as follows: VBR or ECR instances > CCN instances > IPsec connections (VCO).
Route type in the source instance route table — Compare the route type of the route entry in the source instance route table. Priority from high to low is as follows: BGP route entries > custom route entries.
AS_PATH — Compare the length of the AS_PATH attribute, which lists the autonomous systems that a route has traversed. A shorter AS_PATH has higher priority.
Whether the next hop is inter-region — A next hop that is an intra-region connection has higher priority than a next hop that is an inter-region connection.
Routing policy — Select a route based on the priority specified by Routing policies. A smaller priority value has higher priority.
MED (multi-exit discriminator) — Compare the MED value in the route entry attributes. A smaller MED value has higher priority.
If none of the preceding comparisons selects a route with higher priority, the following rules apply:
All next hops are intra-region connections — The routes form ECMP routes.
All next hops are inter-region connections — If the Enterprise Edition transit router route table has the Multi-region VBR ECMP routing feature enabled and the source instance type is VBR or ECR, the routes form ECMP routes. If the feature is not enabled, compare the region IDs of the regions to which the next-hop transit routers belong. An earlier region ID in character order has higher priority.
IPv6 notes
Enterprise Edition transit routers support learning and propagating IPv6 routes and forwarding IPv6 traffic. After you connect VPC, ECR, and VBR instances to an Enterprise Edition transit router, the VPCs, the on-premises networks associated with ECR instances, and the on-premises networks associated with VBR instances can communicate over IPv6 within a region or across regions.

IPv6 support status for network instances
Network instance type | Description |
Enterprise Edition transit router instance | An Enterprise Edition transit router instance supports IPv6 network communication by default after it is created. |
VPC | A VPC supports IPv6 network communication. For a VPC to communicate over IPv6 through an Enterprise Edition transit router, IPv6 must be enabled for the VPC, and IPv6 must be enabled for the VPC connection when you connect the VPC to the Enterprise Edition transit router. For more information, see Enable IPv6 for a VPC and Create a VPC connection. |
ECR instance | An ECR instance supports IPv6 network communication by default after it is created. |
VBR instance | A VBR instance supports IPv6 network communication. For a VBR instance to communicate over IPv6 through an Enterprise Edition transit router, IPv6 must be enabled for the VBR instance. For more information, see Enable IPv6 for a VBR instance. |
IPsec connection instance | IPv6 network communication is not supported for IPsec connection instances. |
CCN instance | IPv6 network communication is not supported for CCN instances. |
Limitations
The multicast feature does not support IPv6 network communication.
IPv6 route entries consume the route entry quota of a transit router route table.
For example, if a transit router route table supports a maximum of 10,000 route entries, the total number of IPv4 and IPv6 route entries in the route table cannot exceed 10,000.
Except in the following scenario, IPv4 and IPv6 traffic behavior and routing behavior are the same for all features of a transit router.
When you create a VPC connection and select the Auto-add transit router routes to all VPC route tables advanced setting, the system automatically configures three custom route entries,
10.0.0.0/8,172.16.0.0/12, and192.168.0.0/16, in all route tables of the VPC. Their next hops are the VPC connection, which directs IPv4 traffic from the VPC to the transit router. The system does not automatically add IPv6 routes to VPC route tables.If a VPC must communicate over IPv6 through a transit router, after the VPC connection is created, you must enable the Route propagation feature for the VPC connection, or manually add IPv6 route entries that point to the VPC connection in the VPC route tables. IPv6 traffic from the VPC can enter the transit router only after you complete one of these actions. For a tutorial, see IPv6 communication over a transit router.
How Basic Edition transit routers work
Since March 31, 2022, Basic Edition transit routers are supported only in CCN regions. Basic Edition transit routers are no longer available for purchase in other regions, and those regions support only new Enterprise Edition transit routers by default. (Recommended) Upgrade the Basic Edition transit routers in those regions to Enterprise Edition transit routers to access more features and larger-scale enterprise networking capabilities. For more information, see Upgrade a Basic Edition transit router to an Enterprise Edition transit router.
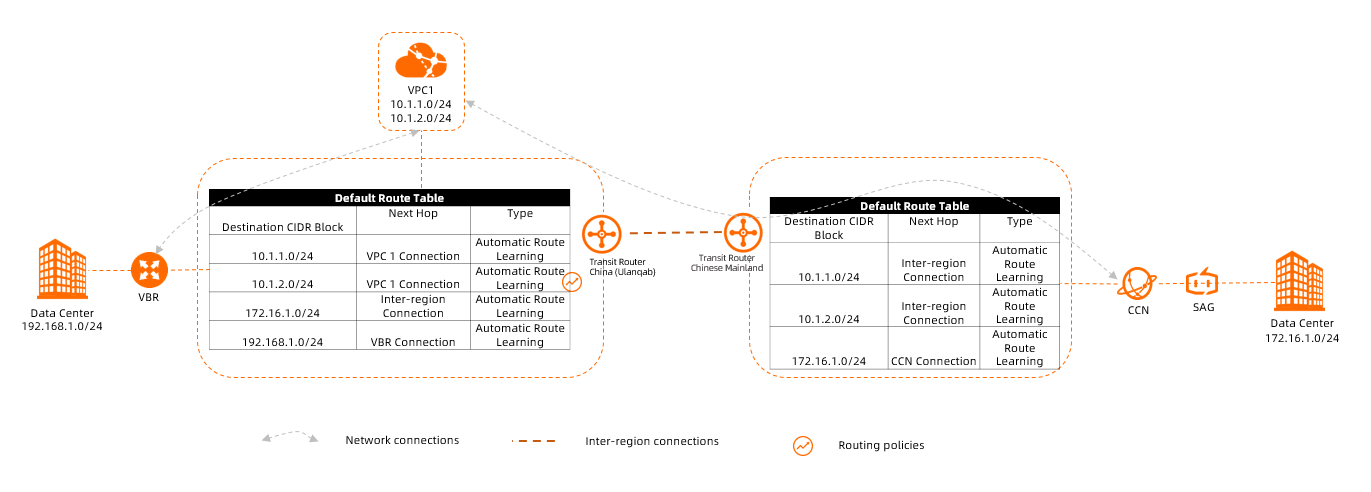
Connect network instances
Basic Edition transit routers support the following network instances:
Routing
After a Basic Edition transit router connects to network instances, it stores the routes of the network instances in a route table and forwards network instance traffic by querying the route table.
Basic Edition transit routers support the longest prefix match principle. After traffic enters a Basic Edition transit router, the transit router matches route entries for the traffic according to the longest prefix match principle.
Each Basic Edition transit router has exactly one system route table when it is created. Custom route tables are not supported.
After a Basic Edition transit router connects to network instances, the routes of all network instances are propagated to the system route table of the Basic Edition transit router. The Basic Edition transit router propagates learned routes to all connected network instances to enable network connectivity.
Routing policies control route propagation for Basic Edition transit router route tables. You can use routing policies to determine whether to propagate routes in a Basic Edition transit router route table to network instances. You can also use routing policies to modify route attributes in a Basic Edition transit router route table.
If both VBR instances and CCN instances are attached to a Basic Edition transit router, the system adds a routing policy with a policy priority of 5000 and a policy action of Reject in the Egress Regional Gateway direction by default. This routing policy limits connectivity between VBR instances, CCN instances, and other VBR instances and CCN instances attached to the transit router. For more information, see Routing policies.