Security Center gives you a unified view of your assets' security posture, risk assessment results, and real-time alerts.
Data overview
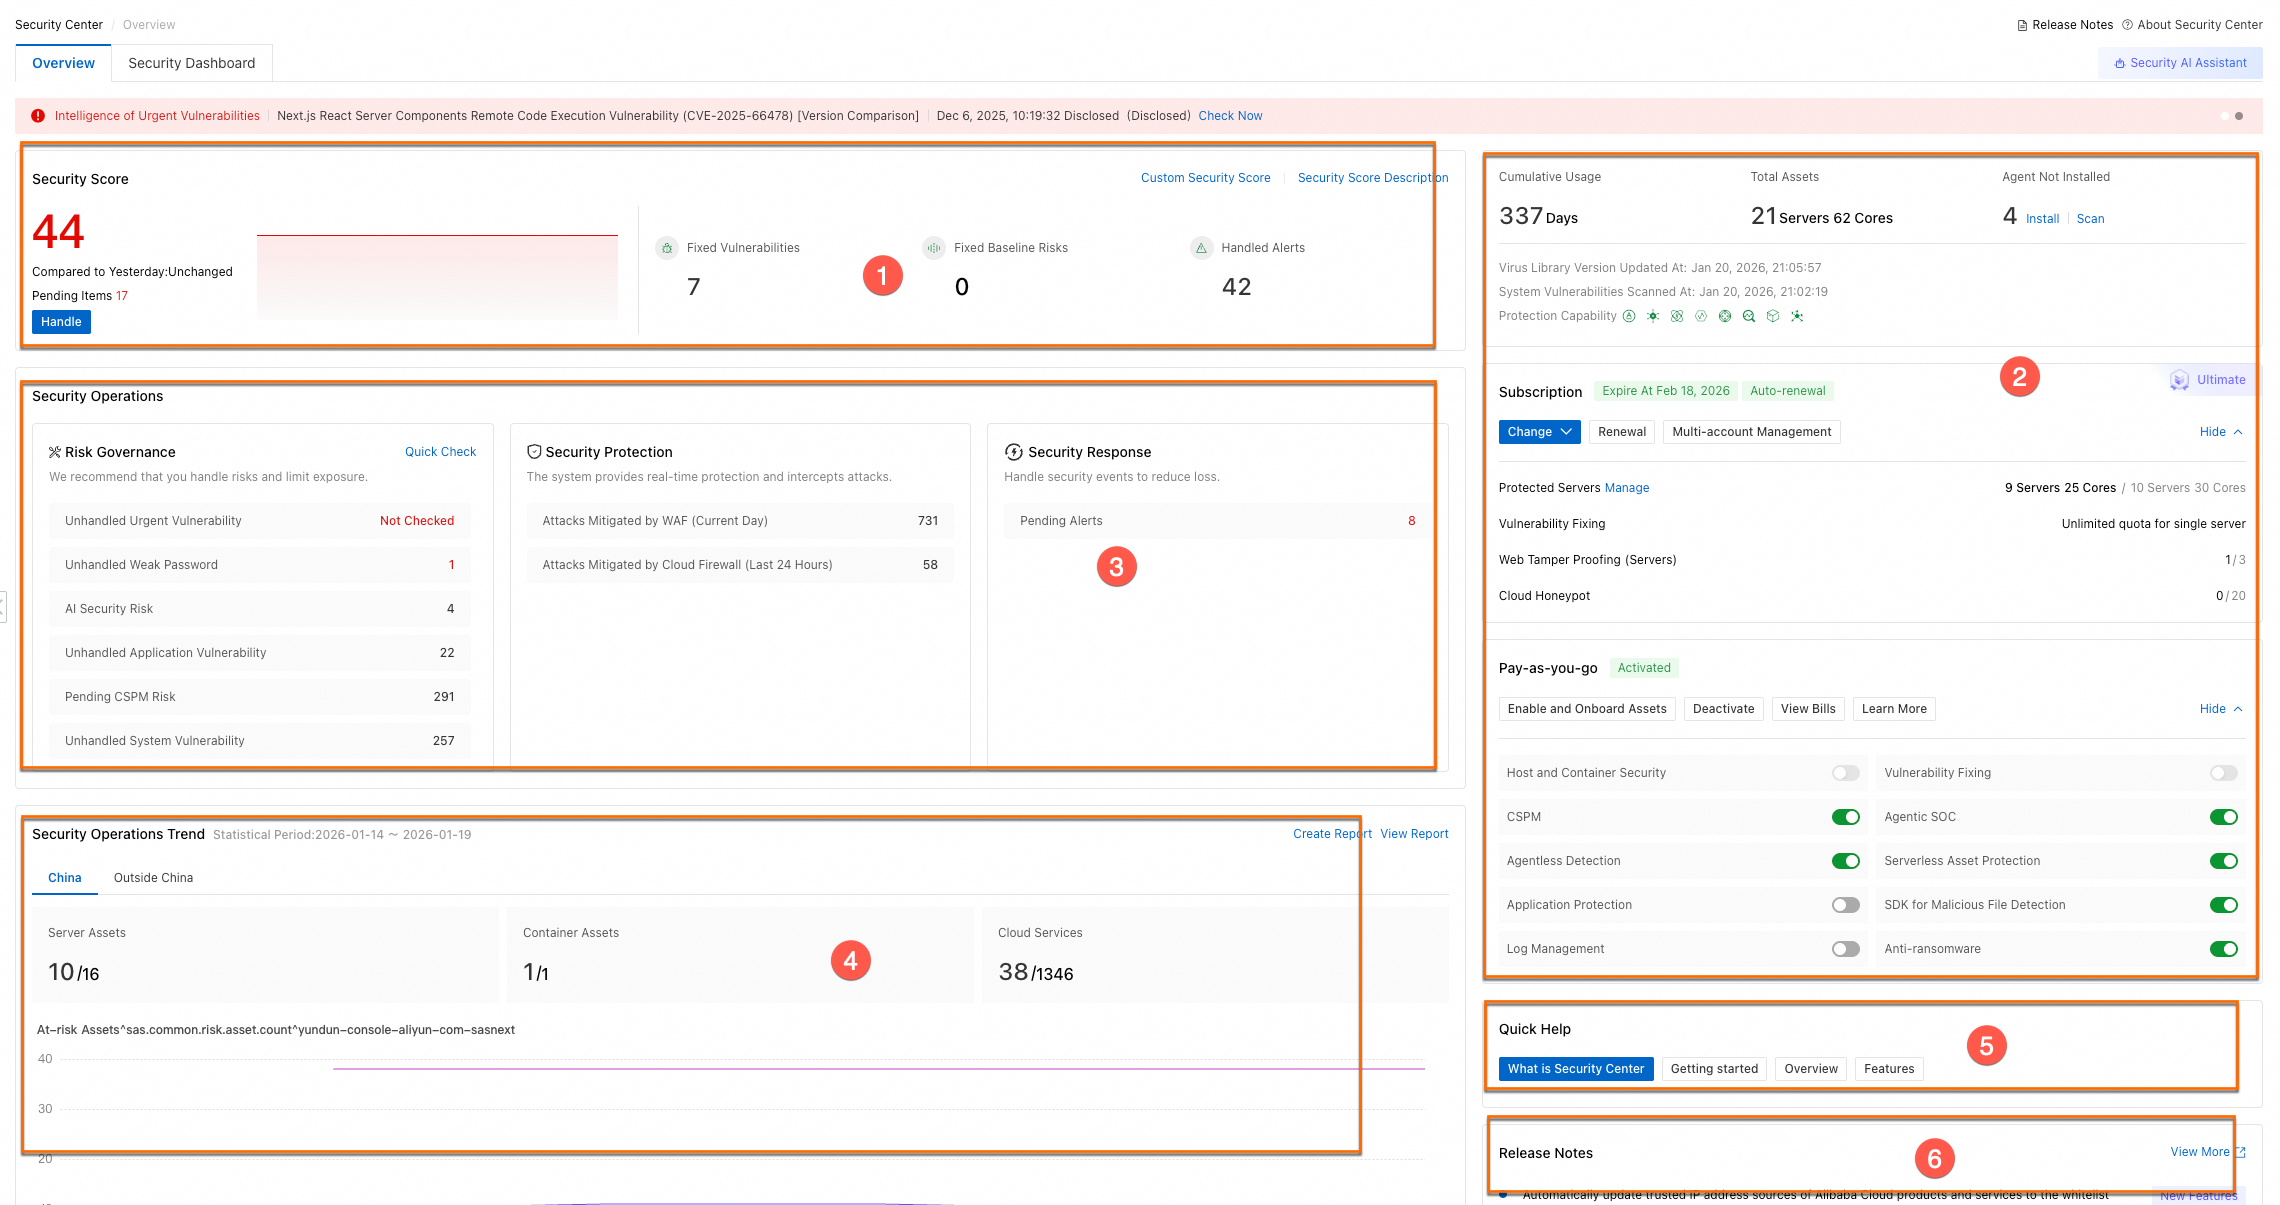
The Overview page displays security data for your cloud assets across global data centers, covering security scores, risks, operation trends, and instance information. It also provides quick access to upgrade, renew, or expand your service.
In the Security Center console, navigate to the Overview page to view the following information:
|
Module |
Description |
Actions |
|
|
Security Score (① in the figure) |
Displays your security score and management statistics, including fixed vulnerabilities, resolved baseline risks, and handled alerts. |
|
|
|
Instance information overview (② in the figure) |
Displays the edition, configuration, expiration date, and protected asset statistics for your subscription-based service, plus pay-as-you-go service status. Note
The information displayed may vary depending on your Security Center edition. The actual UI takes precedence. |
|
|
|
Security Operations (③ in the figure) |
Risk Governance |
Displays security risk data including urgent, application, and system vulnerabilities; weak passwords; cloud service and host baseline risks; API and data security risks. Also provides reminders for improperly connected security products, key feature configurations, and expiring services. Note
The detection features may vary depending on your Security Center edition. The actual UI takes precedence. |
Note
Handle security alerts promptly based on the Security Center documentation. |
|
Security Protection |
Shows real-time blocked attack counts from DDoS scrubbing, Web Application Firewall (WAF), Cloud Firewall, Security Center host protection, and ID Verification. |
Click the number in each section, select a specific risk item, and click Handle Now. |
|
|
Security Response |
Displays unhandled urgent, reminder, and suspicious alert events. Handle these alerts promptly to minimize potential losses. |
Click the number in the Pending Alerts section, select a specific risk item, and click Handle Now. Evaluate and handle security alerts. |
|
|
Security Operations Trend (④ in the figure) |
Displays trend data for host assets, container assets, cloud services, and at-risk assets over time. |
In the upper-right corner of the Security operation trend section, click Create Report or View Report to access the security report page. Security reports. |
|
|
Quick Help (⑤ in the figure) |
Provides quick links to key Security Center information and resources. |
The links include the following: |
|
|
Release Notes (⑥ in the figure) |
Shows recent feature optimizations, releases, and capability updates. |
Click View More to go to the Product News page. |
|
 icon and click Scale Out to purchase more storage for anti-ransomware or log analysis.
 icon to enable or disable a service. Related topics:
Security score
The security score is a health index from 0 to 100, dynamically calculated from your assets' real-time security status, including alert events and configuration flaws. A higher score indicates better security posture.
Improve your security score
Risk levels: High (below 69), Medium (70-84), At-risk (85-94), Secure (95-100). Handle risk alerts promptly to raise your score.
-
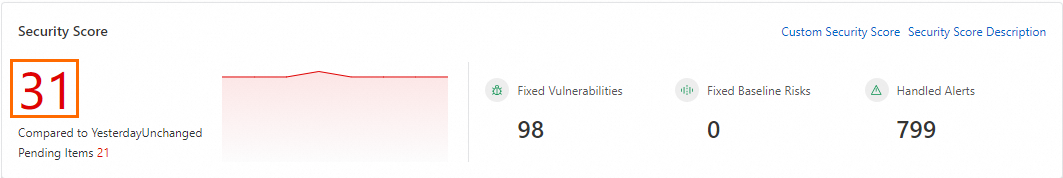
In the Security Score module, click the score value.
-
In the Security Score Details panel, review the specific deduction items. Click Handle Now next to an item to view details and resolve the risk.
Note-
The detection features may vary depending on your Security Center edition. The actual UI takes precedence.
-
The Risk Governance, Security Response, and Security Protection panels consolidate all items that need to be handled. You can also follow the event handling priorities in the security score to address risk alerts promptly. Pending security alerts are counted as score deductions. After you handle or ignore an alert, it is no longer counted, and your security score recovers after the score is recalculated. Score calculation is delayed rather than real-time, so refresh the page later to view the updated score. Each risk item in the security weekly report corresponds to an alert event, and may correspond to only one alert, such as an
unusual logon. If you confirm that the logon was performed by yourself, you can ignore the alert. The weekly report may also list historical alerts that were already handled during the statistical period, and such handled alerts do not affect your current security score.
-
Customize your security score
Security Center assigns a default deduction value to each scoring item. Customize these values based on your business priorities.
-
In the upper-right corner of the Security Score module, click Custom Security Score.
-
In the Custom Security Score panel, set the deduction value for each item, and then click OK.
-
Scoring modules include Core Feature Configurations, Pending Alerts, and Unfixed Vulnerabilities. The deduction threshold for each module can be set from 0 to 100, and the sum of all module thresholds cannot exceed 100.
-
Each module contains individual deduction items. The deduction value for each item can range from 0 to the module's deduction threshold. The sum of the deduction values for all items within a module cannot exceed that module's threshold.
NoteIf you have previously modified and saved your security score settings, the Custom Security Score panel will display a Reset to Default option. Click it to restore the deduction values to the system defaults.
-
FAQ
Why are risks still reported when my security score is 100?
The security score is calculated dynamically from risk items that are currently pending, including vulnerabilities to fix, cloud platform configuration risks, baseline check issues, and unhandled security alerts. After an alert is handled or ignored, it is no longer counted as a score deduction. Therefore, the score can reach 100 when all pending risk items are handled.
The security weekly report may list historical alerts that were already handled during the statistical period, and such handled alerts do not affect your current security score. In addition, score recalculation is delayed rather than real-time, so the score does not change immediately after you handle an alert. Refresh the Overview page later to view the updated score.
Event handling priority
The following table lists event handling priorities that affect your security score (1 = highest priority).
|
Priority |
Event |
|
1 |
Key features are configured or enabled, including:
|
|
2 |
Handle AccessKey pair leak events. |
|
3 |
Address cloud platform configuration risks. |
|
4 |
Remediate baseline check issues. |
|
5 |
Handle security alerts. |
|
6 |
Fix vulnerabilities. |
Vulnerability attention level and security score
To focus on high- and medium-risk vulnerabilities and exclude low-risk ones from the security score calculation, follow these steps.
Go to the Risk Governance > Vulnerabilities page and click Vulnerability Settings in the upper-right corner. In the Vulnerability Settings panel, set the Vulnerability Scan Level. Scan for vulnerabilities.
Does an unfixed medium-risk vulnerability affect my security score?
Yes. Unfixed medium-risk vulnerabilities do affect your security score. The deduction module for unresolved vulnerabilities (maximum deduction: 20 points) deducts points by vulnerability category — CMS vulnerabilities, Windows vulnerabilities, Linux/CVE vulnerabilities, and emergency vulnerabilities — regardless of risk level. Once a vulnerability scan detects a medium-risk vulnerability, it is counted toward the deduction, and leaving it unfixed lowers your security score.
The exact amount deducted depends on the deduction threshold that you configure in Custom Security Score. You can also adjust the vulnerability scan level on the vulnerability settings page described in the preceding FAQ entry (Vulnerability attention level and security score) and clear the medium-risk option to exclude medium-risk vulnerabilities from scanning and score calculation.
Baseline attention level and security score
To focus on high- and medium-risk baselines and exclude low-risk ones from the security score calculation, follow these steps.
Go to the page and click Policy Management in the upper-right corner. On the tab, select the Baseline Check Level. Baseline checks.