DataWorks provides a comprehensive permission system for product management, feature use. For feature-use permissions, DataWorks uses global roles and workspace-level roles to control access to global features and workspace-level features, respectively. This topic describes how DataWorks uses role-based access control (RBAC) to manage feature-use permissions.
In DataWorks, product management permissions cover operations performed in the DataWorks console. Examples include creating, disabling, and deleting workspaces on the Workspace list page; creating exclusive resource groups and configuring their networks on the Resource Groups page; and configuring contacts on the Alarm configuration page. DataWorks uses RAM policies to manage product management permissions. For more information, see RAM policies for service and console permissions.
Global and workspace-level features
Log on to the DataWorks console and enter a DataWorks workspace. Click the  icon on the left side of the top menu bar to display all DataWorks feature modules, as shown in the following figure.
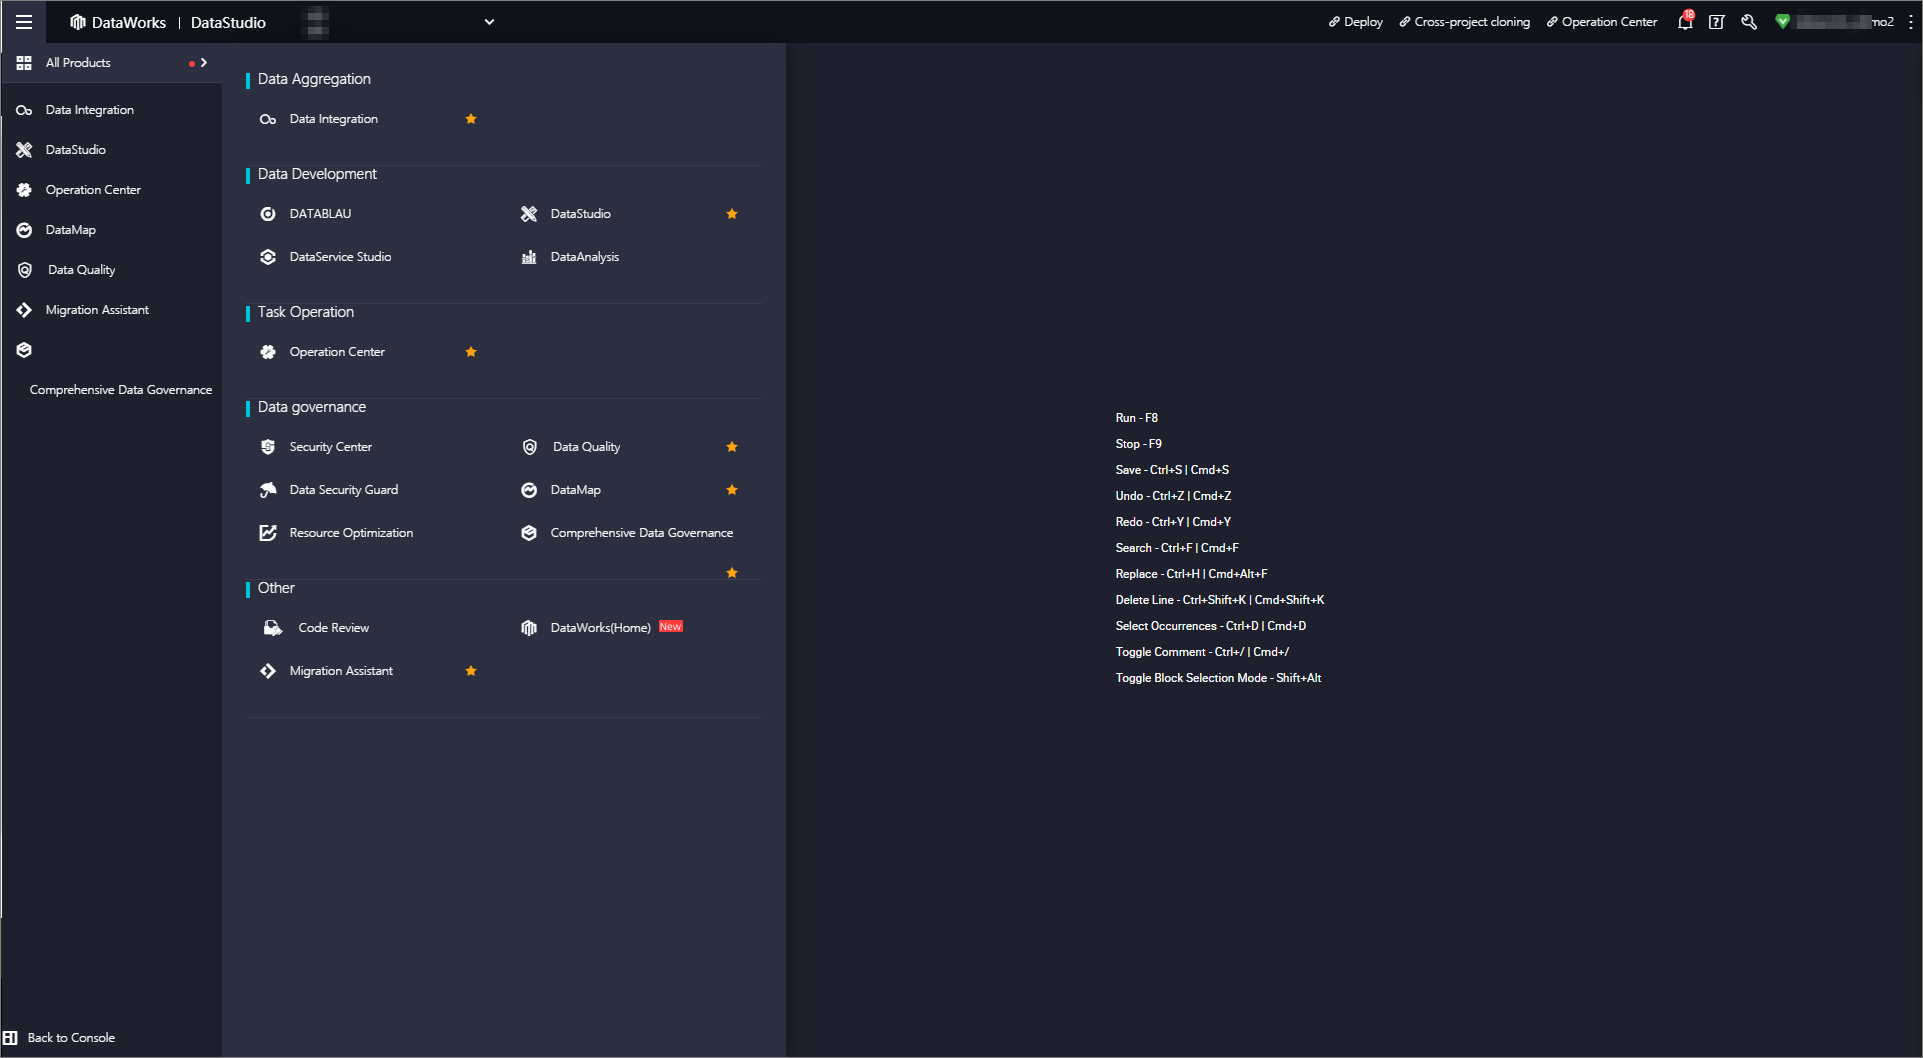 Click a feature module to open its page and use it. After you open the page:
If the top menu bar displays the DataWorks workspace name, the module is a workspace-level module. For example, DataStudio.
If the top menu bar does not display the DataWorks workspace name, the module is a global-level module. For example, DataMap.
For more information about how to distinguish global-level features from workspace-level features, see Appendix: Distinguish workspace-level and global-level modules.
Global roles and workspace-level roles
DataWorks uses an RBAC (role-based access control) model for feature-use permissions. You can define global roles for global features and workspace-level roles for workspace-level features. After you assign a user (a RAM user or RAM role) to a role, the user can use the DataWorks feature modules included in that role's permissions.
Key concepts:
User: A RAM user or RAM role.
Role: A DataWorks workspace-level role or global role.
Permission: Access to a DataWorks workspace-level or global-level feature module.
DataWorks provides built-in global and workspace-level roles that you can assign to users. You can also create custom global or workspace-level roles as needed. The following figure shows the relationship among users, roles, and permissions.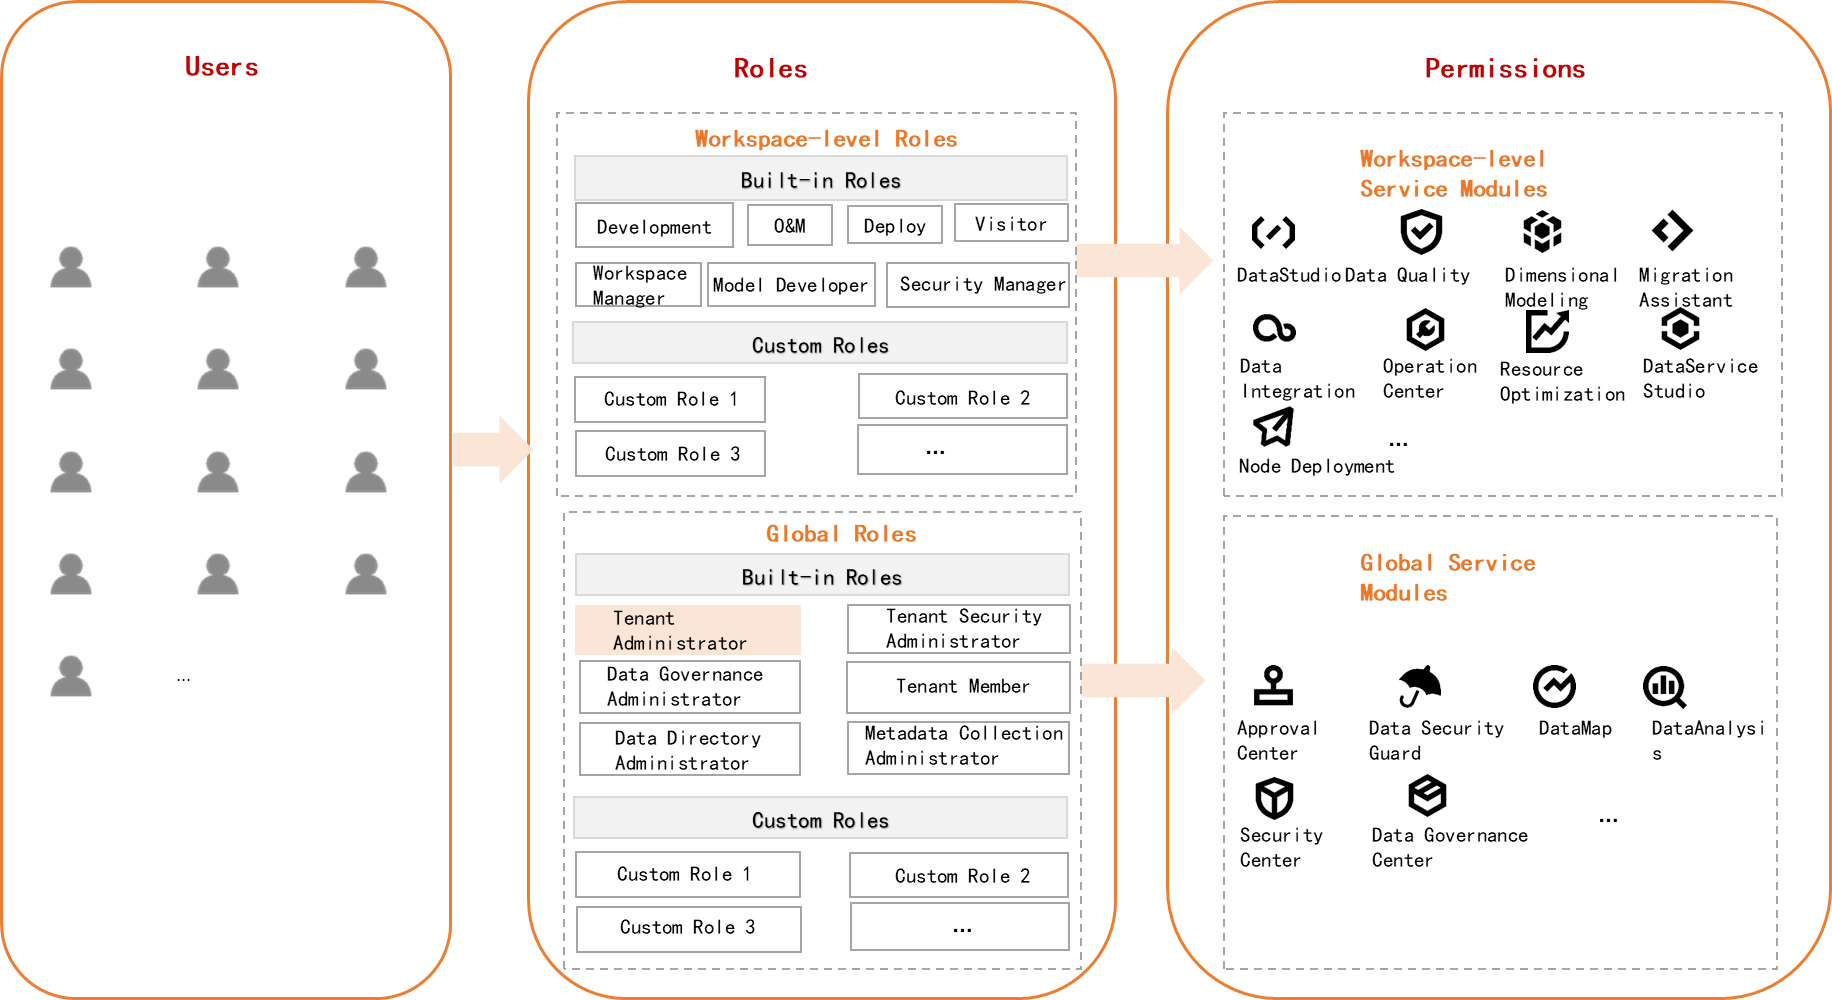
Among all roles, only the Tenant Administrator global role grants access to all feature modules.
All RAM users under an Alibaba Cloud account are assigned the Tenant Member role by default.
If a Tenant Administrator creates a custom global role that denies access to some global-level modules, the custom role's permissions take precedence over those of the Tenant Member role.
For example, RAM user A under an Alibaba Cloud account has the Tenant Member role by default and can access the DataMap feature page. If a tenant administrator creates a custom role that denies access to DataMap and assigns RAM user A to that role, RAM user A cannot access the Data Map page.
Permissions of global roles
DataWorks global roles include tenant administrator, tenant member, tenant security administrator, data directory administrator, metadata collection administrator, and data governance administrator. The following table describes the permissions of each role.
Role | Permission | Grantor | Description |
Tenant Administrator | Permissions for all DataWorks product features, excluding operations in the Alibaba Cloud DataWorks console. | The tenant owner (Alibaba Cloud account), a RAM user with the AliyunDataWorksFullAccess policy, a user with AdministratorAccess permissions, or a RAM user with the Tenant Administrator role can grant the Tenant Administrator role to RAM users under their account. | The highest-level DataWorks administrator. This role can use all features in DataWorks. |
Tenant Member | Has the same feature-use permissions as the current developer role.
| No grant is required. By default, all RAM users under the current Alibaba Cloud account have the Tenant Member role. | All RAM users and RAM roles under the current Alibaba Cloud account have the Tenant Member role by default. |
Tenant security administrator | Has all permissions for Security Center, Approval Center, and Data Security Guard. | Tenant AdministratorCan grant the Security Administrator. | Manages security-related workspace settings. |
Data Governance Administrator | Has standard use permissions for Data Governance Center, excluding service activation and creating, enabling, or stopping check items; also has management permissions for Data Governance Center. | Tenant AdministratorCan grant the Data Governance Administrator. | Manages Data Governance Center. |
Data Directory Administrator | Has standard use permissions for DataMap and permission to manage DataMap's Data Catalog feature. | Tenant AdministratorCan grant the Data Directory Administrator. | Manages the data directory feature in Data Map. |
Metadata Collection Administrator | Has standard use permissions for DataMap and Metadata Collection permission. | Tenant AdministratorCan grant the Metadata Collection Administrator. | Can use the metadata collection feature in Data Map. |
Permissions of workspace-level roles
DataWorks provides several built-in workspace-level roles. You can also create custom workspace-level roles to meet your permission management needs.
Built-in workspace-level roles
DataWorks provides the following built-in roles: Project Owner, Data Analyst, Workspace Administrator, Development, O&M Personnel, Deployment Personnel, Visitor, Security Administrator, Model Designer.
NoteThe workspace owner is the Alibaba Cloud account. A RAM user creates a workspace only on behalf of that account. You cannot grant the Project Owner role to other users. For details about each built-in role's permissions for DataWorks feature modules, see Appendix: permissions of built-in workspace roles.
Custom workspace-level roles
A custom DataWorks workspace-level role lets you control whether the role can use a specific workspace-level feature module. For instructions on creating a custom role, see Manage permissions on workspace-level services.
When you use workspace-level roles to control access to workspace-level features, permissions apply to two types of operations: DataWorks feature operations and compute engine operations. Compute engine permissions include the ability to create, read, update, and delete tables and resources in an engine database. The following table describes how built-in and custom roles control these two types of operations.
Permission target | Built-in role | Custom role |
DataWorks feature operations | DataWorks has predefined each role's permissions for workspace-level features. For details, see Appendix: permissions of built-in workspace roles. | When you create a custom role, you specify whether it can perform operations on each workspace-level feature. |
Compute engine permissions: MaxCompute |
| When you create a custom role and map it to a MaxCompute role, the custom role has the permissions of the mapped MaxCompute role. |
Compute engine permissions: EMR | When you register an EMR cluster, configure a mapping between workspace members and accounts to grant compute engine permissions. For more information, see Data Studio (legacy): Register an EMR cluster. | |
Compute engine permissions: CDH | Map workspace members to Linux or Kerberos accounts to grant compute engine permissions. For more information, see Configure a workspace. | |
Compute engine permissions: other engines | Before you use an engine with DataWorks, create a data source for it in DataWorks. For other engines, configure the scheduling identity used in the development and production environments when you create the data source. For example, for an AnalyticDB for PostgreSQL data source, specify the username and password used to access the database. When users with built-in or custom workspace-level roles run tasks on other engines, they use the scheduling identity configured for the data source. Workspace-level roles therefore do not directly control permissions for non-MaxCompute engines. Those permissions are determined by the scheduling identity specified when the data source is created. | |
As described above:
When DataWorks provides built-in workspace-level roles, it also maps them to roles of data sources created in the workspace. This gives the built-in roles some of the compute engine operation permissions held by the mapped roles.
DataWorks supports custom workspace-level roles. When you create a custom role, you can map it to a compute engine role so that the custom role has compute engine operation permissions.
After you grant a workspace-level role to a user, the user can perform DataWorks feature operations and compute engine operations. The following MaxCompute examples explain the actual permissions granted by built-in and custom workspace-level roles.
Scenario 1: Grant a built-in workspace-level role
Example: A user with workspace administrator permissions adds a RAM user as a workspace member and grants the built-in Development role.
NoteFor instructions on adding members and granting permissions, see Manage permissions on workspace-level services.
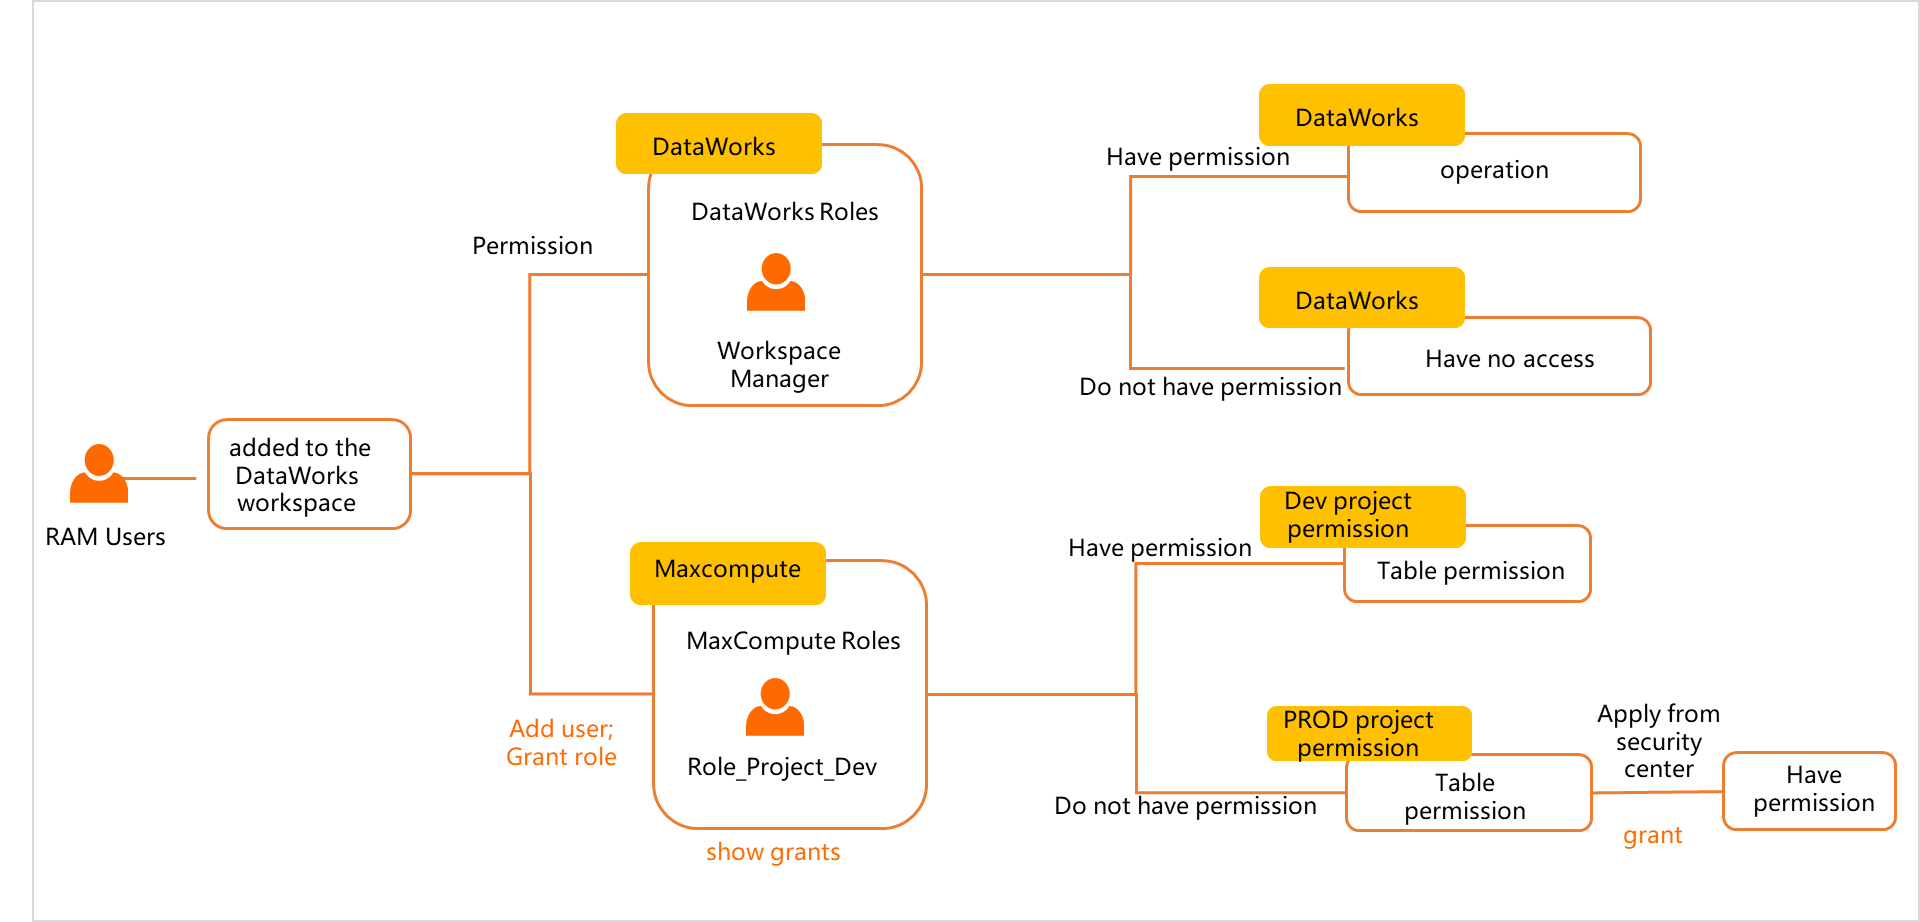 After being added, the RAM user has some permissions in both DataWorks and MaxCompute. The following describes the operations that the user can perform at each level.
DataWorks: After the RAM user is granted the Development role, the user can develop and submit code in DataWorks but cannot publish it directly to the production environment. Publishing to production requires O&M permissions, which the Project Owner, Administrator and O&M Personnel roles have.
MaxCompute: After the RAM user is granted the Development role, the user is also granted the Role_Project_Dev role in MaxCompute. This role grants some table and project permissions in the MaxCompute development project.
NoteA RAM user who is granted a built-in administrator role has more DataWorks feature permissions but still cannot directly access production tables.
Here, RAM user refers specifically to a RAM user who is not assigned as a non-scheduling engine access identity, that is, is not assigned as a MaxCompute access identity for the production project.
Scenario 2: Grant a custom workspace-level role
Example: A user with workspace administrator permissions adds a RAM user as a workspace member and grants a custom DataWorks workspace role.
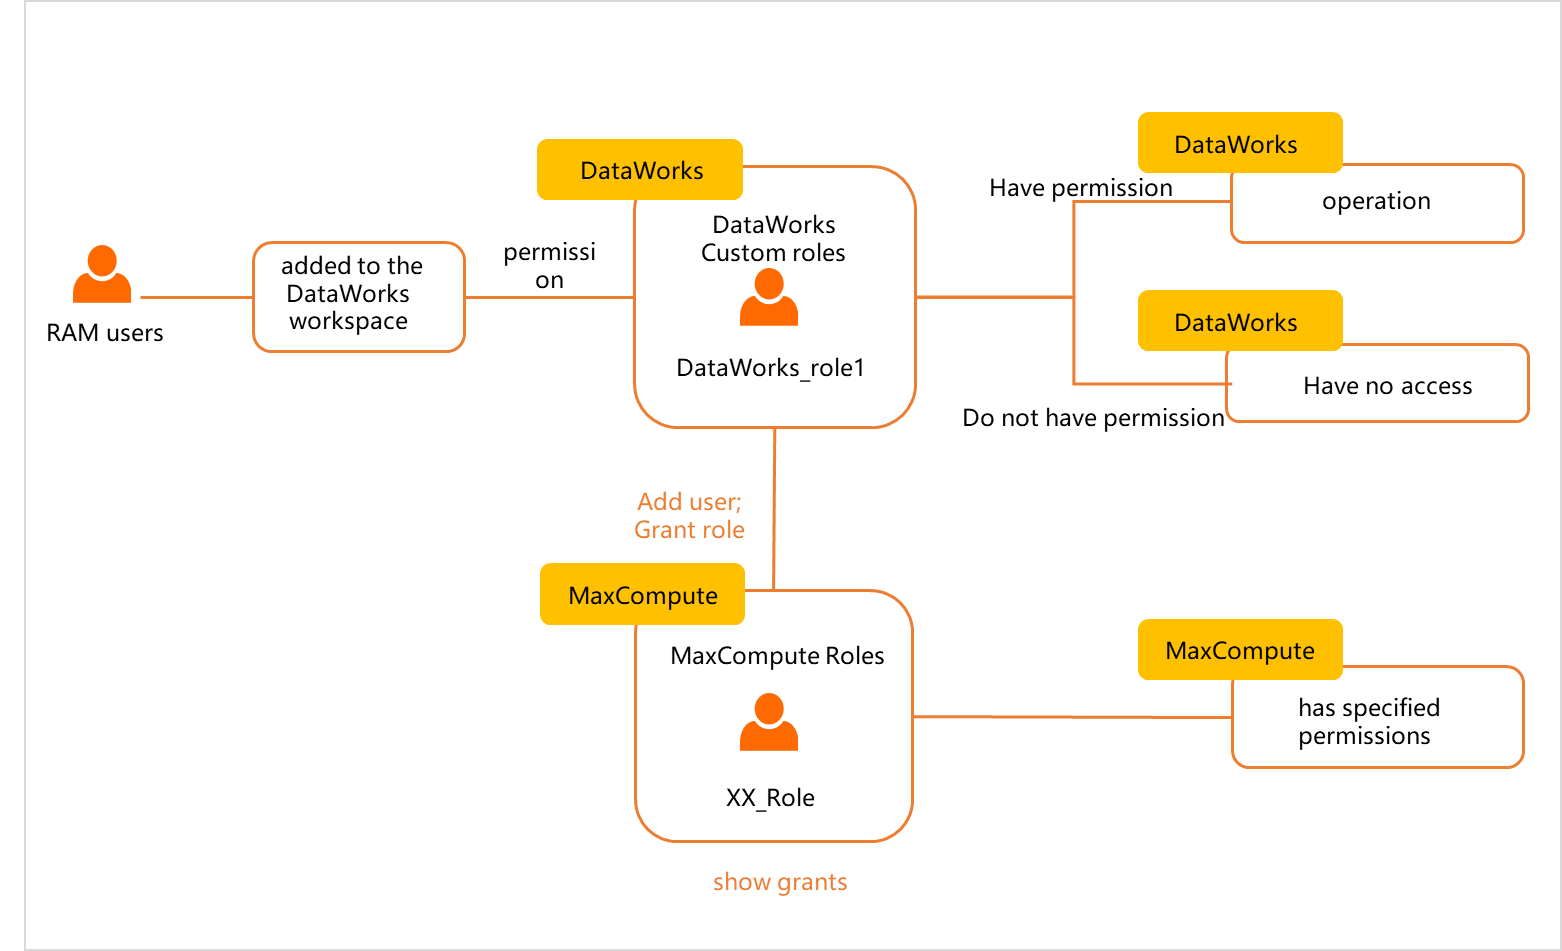 When you create a custom role, you can choose whether to map it to a MaxCompute role. After creating the role, assign it when adding the workspace member. The RAM user then has some permissions in both DataWorks and MaxCompute. The following describes the operations that the user can perform at each level.Note
For instructions on creating a custom role, see Manage permissions on workspace-level services. For instructions on adding members and granting permissions, see Manage permissions on workspace-level services.
DataWorks: A RAM user granted a custom DataWorks role can access only the modules allowed by that role.
MaxCompute:
If the custom DataWorks role has no engine permission mapping, the RAM user has no MaxCompute operation permissions and cannot run queries or other operations by using commands.
If the custom DataWorks role has an engine permission mapping, the RAM user has the same operation permissions as the mapped MaxCompute role.
NoteUnless a RAM user is assigned as the scheduling engine access identity (the MaxCompute access identity for the production project), the user has no production-environment operation permissions by default after joining a workspace. To operate on or access production tables, the user must request permissions in Security Center. For more information, see Request permissions on tables in Security Center (latest version). For details about MaxCompute access identities, see Configure a workspace.
Appendix: Mapping built-in workspace-level roles to MaxCompute permissions
The following table shows how built-in DataWorks workspace-level roles map to permissions in a MaxCompute development project, along with the permissions granted by each mapping.
DataWorks member role | MaxCompute role | Data permissions in the DataWorks development environment / MaxCompute DEV project | Data permissions in the DataWorks production environment / MaxCompute PROD project | DataWorks platform permissions |
Workspace administrator | Role_Project_Admin |
| No permissions by default. Request them through an approval process in Security Center. | Manages the workspace's basic properties, data sources, compute engine configuration, and members. Can grant workspace administrator, developer, O&M, deployment, and visitor roles to workspace members. |
Developer | Role_Project_Dev |
| Users with the developer role can create workflows, script files, resources, and UDFs, and create and delete tables. They can create deployment packages but cannot perform deployment. | |
O&M | Role_Project_Pe | All permissions on project/fuction/resource/instance/job in the current project, Read permission on package, and Read/Describe permissions on table. Note This role has MaxCompute permissions, but users with the O&M role cannot run nodes directly in the DataWorks interface to execute tasks. | A workspace administrator grants the O&M role. Users with this role can publish tasks and perform online O&M operations, but cannot develop data. | |
Deployment | Role_Project_Deploy | No permissions by default. | The deployment role is similar to the O&M role but does not grant online O&M permissions. | |
Data analyst | Role_Project_Data_Analyst | No permissions by default. | By default, the data analyst role grants only permission to use the DataAnalysis module. | |
Visitor | Role_Project_Guest | No permissions by default. | Users with the visitor role can view content but cannot edit workflows or code. | |
Security administrator | Role_Project_Security | No permissions by default. | The security administrator role is used only in Data Security Guard for tasks such as configuring sensitive-data rules and auditing data risks. | |
Model designer | Role_Project_Erd | No permissions by default. | Can view models and edit data warehouse plans, data standards, dimensional models, and data metrics, but cannot publish models. | |
None | Project Owner | The owner of the MaxCompute project, with all permissions in that project. | Has permissions. | None |
None | Super_Administrator | The super administrator of the MaxCompute project, with project management permissions and all permissions for every type of resource in the project. | Has permissions. | None |
None | Admin | Each project automatically creates an Admin role and grants it specific permissions. The role can access all objects in the project, manage users and roles, and grant permissions. Unlike the Project Owner, the Admin role cannot assign Admin permissions to users, configure project security settings, or modify the project's authorization model. The permissions of the Admin role cannot be changed. The Project Owner can grant the Admin role to a user to delegate security administration. | Has permissions. | None |
Appendix: Distinguish workspace-level and global-level modules
A module is workspace-level if the top menu bar displays the DataWorks workspace name. For example, DataStudio.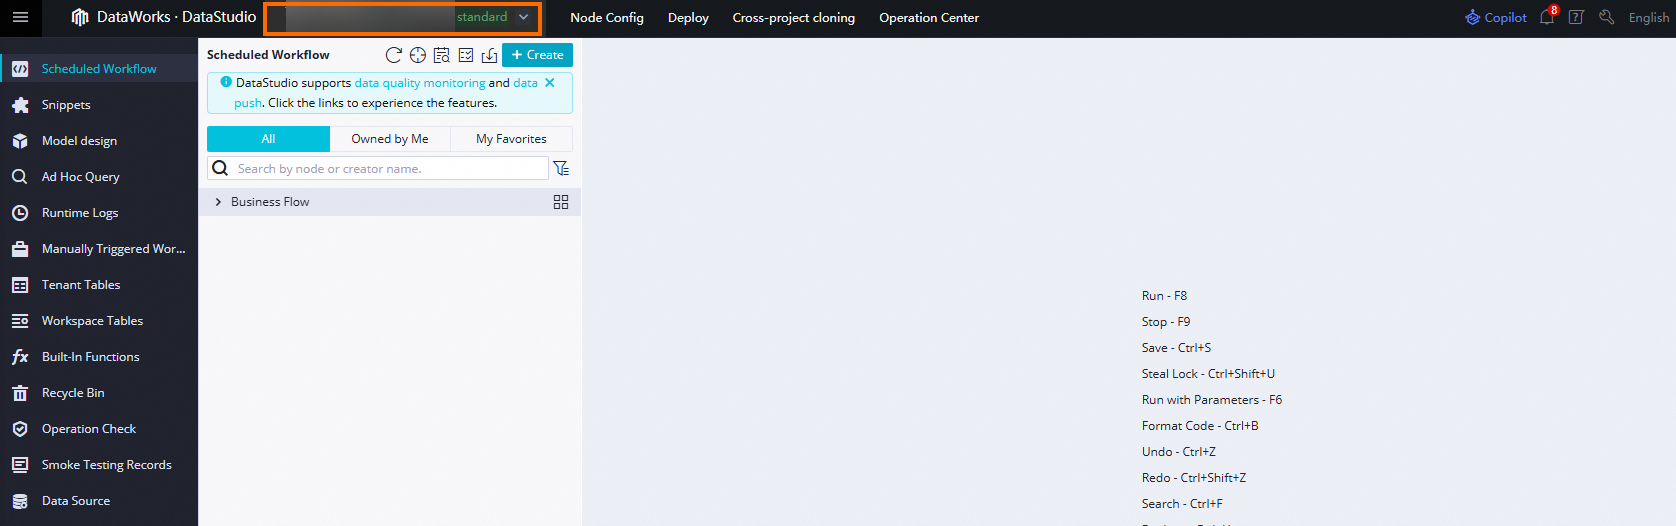
A module is global-level if the top menu bar does not display the DataWorks workspace name. For example, DataMap.