After you enable mitigation logs, you can use them to query and analyze traffic scrubbing, blackhole filtering, and traffic rerouting events on your Anti-DDoS Native instance.
Prerequisites
Mitigation logs are enabled. For more information, see Enable mitigation logs.
Query and analyze logs
Log on to the Traffic Security console. In the left-side navigation pane, choose DDoS.
In the left-side navigation pane, choose .
In the top navigation bar, select the resource group to which the instances belong and the region in which the instances reside.
Anti-DDoS Native 1.0 (Subscription) instances: Select the region in which the instance resides.
Anti-DDoS Native 2.0 (Subscription) and Anti-DDoS Native 2.0 (Pay-as-you-go) instances: Select All Regions.
In the upper part of the Mitigation Logs page, select an Anti-DDoS Native instance.
Enter a query and analysis statement.
A query and analysis statement consists of a search statement and an analytic statement in the format
Search statement|Analytic statement. For more information about the syntax, see Search syntax and functions and Aggregate functions.You can also use Data Explorer to build query and analysis statements. For instructions, see High-performance fully accurate query and analysis (Dedicated SQL).
In the upper-right corner of the page, set the time range for the query.
NoteThe query results may deviate from the specified time range by up to 1 minute.
Click Search & Analyze to view the query and analysis results.
Query & Analysis page
Page overview
The raw log query page of Simple Log Service (SLS) mainly consists of the following areas:
Top search bar: enter a query statement (SQL, SPL, or Copilot); on the right, select a time range (such as Last 1 Minute).
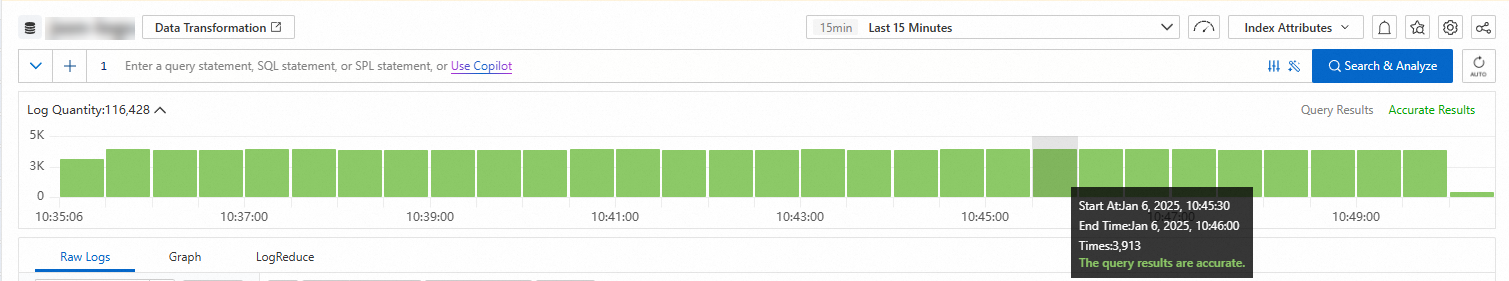
Search result overview: shows the number of matched log entries (7,246 in the example) and a time-distribution histogram.
Tab area: contains the Raw Logs, Statistical Charts, and LogReduce tabs, and supports switching between table and raw views, a line-wrap toggle, and pagination settings.
Displayed Fields panel on the left: lists indexed fields such as
@timestamp,host,remote_addr,request_method,status, anduri.Main area: shows the structured key-value details of each log entry, including Nginx access log fields such as the timestamp, source IP, host name, request method, request URI, and response status code.
Histogram
-
Hover over a green block to view its time range and hit count.
-
Double-click a green block to drill into a finer time granularity. Results for that time range appear on the Raw Logs tab.
Raw logs
-
Log details
-
Click Table or Raw Data to switch the log display format.
-
 > Download Log: Download logs to your computer. Download logs.
-
 > JSON Settings: Set the display type and level for JSON logs.
-
> Event Settings: Configure events for raw logs.
-
 : Copy the log content.
-
 : Summarize information and identify errors in log content using SLS Copilot.
-
 : View a log entry in context within its original file. Available only for Logtail-collected logs. Contextual query.
-
 : Monitor logs in real time and extract key information. Available only for Logtail-collected logs. LiveTail.
-
-
Displayed fields
-
In the Displayed Fields section, click the
 icon next to a field to remove it from Displayed Fields. The field no longer appears in logs on the right.
-
 : Save the current field selection as a favorite. After configuring the fields to display in Area 5, select a saved view from the drop-down list above Area 4.
-
 > Tag Settings: Set a field as a system tag.
-
> Alias: When enabled, field names are replaced by their aliases. Fields without aliases keep their original names. Set field aliases in Create indexes.
-
-
Index fields
-
In the Indexed Fields section, click the
 icon next to a field to add it to Displayed Fields. The field then appears in logs on the right.
-
 : View the Basic Distribution and Statistical Metrics of the field. Field settings.
-
Graph
A graph renders the visual output of a query and analytic statement. Simple Log Service supports tables, line charts, column charts, and more. Statistical charts. View results on the Graph tab.
Other features on this tab:
-
Add to New Dashboard: Save query and analysis results as a chart to a dashboard for real-time monitoring. Click Add to New Dashboard to add a chart. Visualization overview.
-
Save as Scheduled SQL Job: Periodically analyze data, store aggregated results, and filter or project fields. Scheduled SQL.
-
Interaction Occurrences: Drill down into data by adjusting dimension hierarchy and analysis granularity. Add an interaction to a dashboard for drill-down analysis.
LogReduce
On the LogReduce tab, click Enable LogReduce to aggregate highly similar logs during collection. LogReduce.
SQL enhancement
Click the  icon in the upper-right corner to enable Dedicated SQL for the current session. Dedicated SQL allocates additional computing resources to analyze larger data volumes per query. To enable Dedicated SQL by default: High-performance, fully accurate query and analysis (Dedicated SQL).
Alerting
Click the  icon in the upper-right corner and select Save as Alert to create an alert rule based on the query and analysis results. Get started with alerting.
Saved search
Click the  icon in the upper-right corner to Save as Saved Search the current query and analysis statement. Use saved searches to quickly re-run frequent queries. Saved Search.
Share
Click the  icon in the upper-right corner to copy and share the current page URL. Embed and share console pages.