After you add a website to Web Application Firewall (WAF), you can configure a Data Security whitelist to allow requests that meet specified conditions to bypass detection by specific modules (Data Leakage Prevention, Website Tamper-proofing, and Account Security). The Data Security whitelist can prevent legitimate business requests from being mistakenly blocked by data security rules.
Prerequisites
-
You have activated a Web Application Firewall instance.
-
Your website has been added to WAF. For more information, see Tutorials.
Background information
Data Security protects against page content leaks and tampering to ensure the integrity and confidentiality of your website data. This feature includes the following detection modules:
If these modules cause false positives by blocking legitimate website requests, you can configure a Data Security whitelist to allow requests that meet specific conditions to bypass detection by the specified modules.
Configure highly specific rules to ensure that only legitimate requests bypass protection.
Procedure
-
Log on to the Web Application Firewall console.
-
In the top menu bar, select the resource group and region for your Web Application Firewall instance (Chinese Mainland or Outside Chinese Mainland).
-
In the left navigation pane, choose .
-
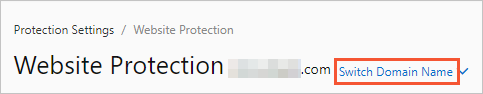
On the Website Protection page, switch to the domain name to configure.
-
Click the Web Security tab, locate the Data Security section, and then click Configure Now.
-
Create a Data Security whitelist rule.
-
On the Data Security - Whitelist page, click Create.
-
In the Create Rule dialog box, configure the following parameters.
Parameter
Description
Rule Name
Enter a name for the rule.
Match Condition
Define the conditions for requests that you want to add to the whitelist. Click Add Condition to specify up to five conditions. If you specify multiple conditions, a request must meet all of them to be whitelisted.
For more information about match condition fields, see Fields in match conditions.
Bypassed Modules
Select the detection modules to bypass if a request meets the conditions. You can select one or more of the following:
-
Data Leakage Prevention
-
Website Tamper-proofing
-
Account Security
-
-
Click Save.
Newly created Data Security whitelist rules are enabled by default. You can view the new rule in the rule list and disable, edit, or delete it as needed.
-