Configure an Internet Firewall access control policy with region-based filtering to block inbound traffic from international regions. This example applies to businesses that serve users only in Chinese mainland.
Scenario
In the scenario shown in the following figure, you have an ECS instance with the EIP 47.100.XX.XX. Because your business serves users only in Chinese mainland, you need to configure a policy to block all traffic from international regions.

Prerequisites
You have purchased Cloud Firewall and enabled Internet firewall protection. For more information, see Purchase Cloud Firewall and Internet firewall.
Procedure
Log on to the Cloud Firewall console.
In the left-side navigation pane, select .
On the Inbound tab, click Create Policy. In the Create Inbound Policy panel, click the Create Policy tab and configure the policy with the following parameters.
Parameter
Description
Example value
Source Type
The source of the network traffic. Select a source type and enter its address.
Location
Source
All Locations Outside China
Destination Type
The destination of the network traffic. Select a destination type and enter its address.
IP
Destination
Enter the public IP address of the ECS instance,
47.100.XX.XX/32.Protocol Type
The transport layer protocol. Valid values are TCP, UDP, ICMP, and ANY. If you are unsure which protocol to use, select ANY.
ANY
Port Type
The type and number of the destination port.
Port
Port
Enter
0/0to apply the policy to all ports.Application
The application type associated with the traffic.
ANY
Action
The action to apply to matching traffic.
Allow: Allow the traffic.
Drop: Block the traffic without any notification.
Monitor: In this mode, traffic is allowed by default. You can filter and observe this traffic by using relevant fields in Traffic Logs, After a period of observation, adjust to Allow or Deny.
Drop
Priority
Highest: The access control policy takes effect with the highest priority.
Lowest: The access control policy takes effect with the lowest priority.
Custom: Customize the priority. Minimum: 1, Maximum: 50. The smaller the number, the higher the priority.
Highest
Policy Validity Period
Always
Single Time Range: Select a one-time time period.
Recurrence Cycle: Select a recurring time period and effective dates.
NoteThe start time of the effective date must be earlier than the end time. The policy takes 3 to 5 minutes to take effect.
If you select Indefinite Recurrence, the effective end time is automatically set to December 31, 2099.
Related FAQ: Does a policy take effect if the recurrence cycle spans multiple days?
Always
Status
Specifies whether the policy is enabled upon creation. You can enable disabled policies later from the policy list.
Enable
Next steps
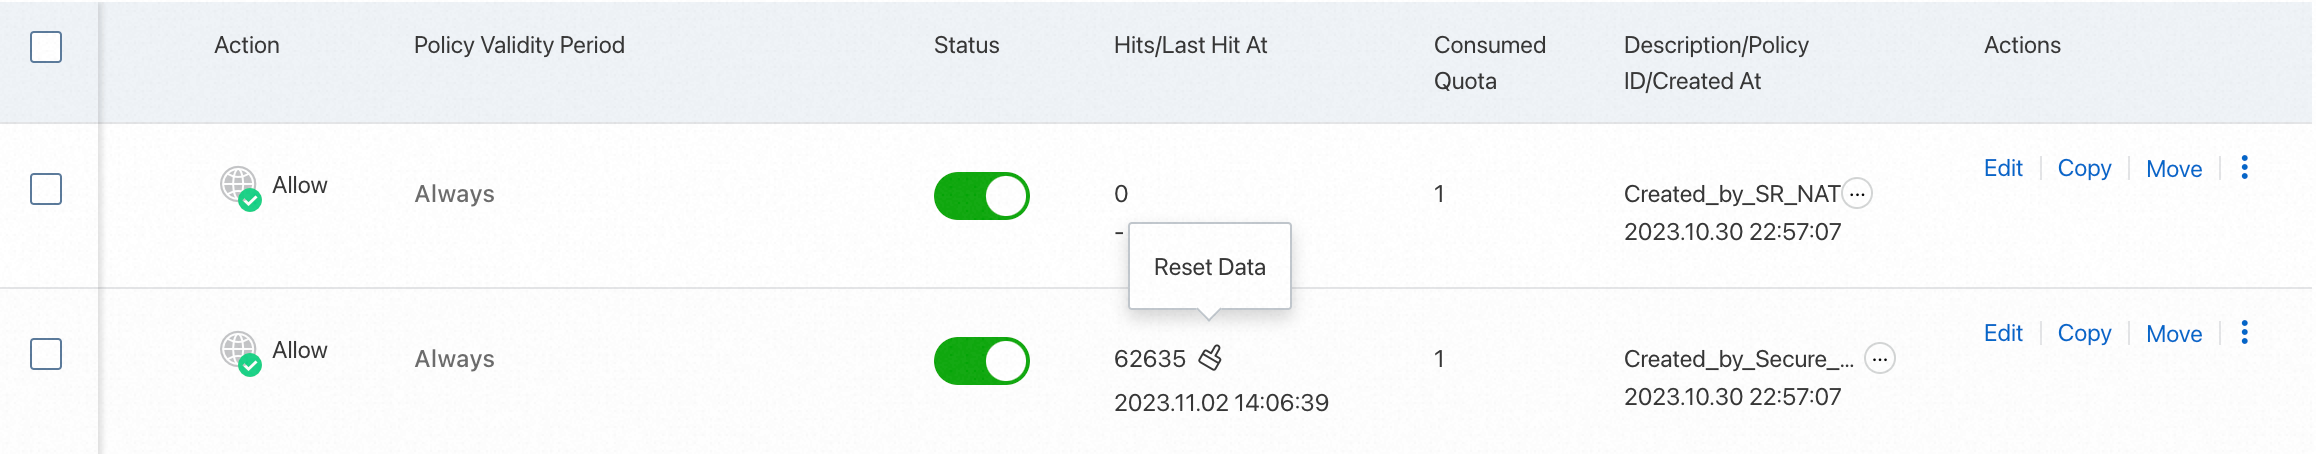
After your business has been running for a period, you can view the hit count of access control policies in the Hits/Last Hit At column in the access control policy list.
Click the hit count to go to the Traffic Logs page to view traffic logs. For information about how to view traffic logs, see Traffic Logs.
Related documentation
For detailed instructions on how to configure access control policies for the Internet firewall, see Configure Internet firewall access control policies.
For more information about access control policy configuration principles, see Access control policy configuration examples.
For answers to common questions about access control policies, see FAQ about access control policies.