Security Center Basic provides free security protection to all Alibaba Cloud users, including unusual logon detection, DDoS trojan detection, and vulnerability detection. Install the Security Center agent on your servers to use these services for free.
Intended users
Security Center Basic is intended for individual users and enterprise users who need centralized security management for their server assets. It supports both Alibaba Cloud servers and non-Alibaba Cloud servers, including on-premises servers.
Features
Security Center Basic provides the following security capabilities to help you detect security risks on your servers at the earliest opportunity:
Security Center Basic only detects security risks such as vulnerabilities and alerts. It does not automatically handle these risks. To handle risks automatically, upgrade to a paid edition.
Feature | Description | References |
Vulnerability detection | Detects Linux software vulnerabilities, Windows system vulnerabilities, and Web-CMS vulnerabilities on your servers. Security Center automatically scans your servers on a regular basis. You can view the scan results and vulnerability details on the Vulnerabilities page. | |
Urgent vulnerability (critical security event alert) scan | Detects whether your servers are affected by high-risk vulnerabilities that were recently disclosed on the Internet. This helps you identify critical security risks in your system at the earliest opportunity and reduces the chance that your system is compromised. Note To scan for urgent vulnerabilities, you must manually start a one-click scan on the Vulnerabilities page. | |
Unusual logon detection | Detects unusual logons to your servers, including logons from unapproved locations and brute-force attacks. This helps you identify the risk of account theft at the earliest opportunity and reduces the chance of cyberattacks on your system. | Overview of Cloud Workload Protection Platform (CWPP) security alerts |
Cloud service threat detection | Detects unusual operations on cloud services based on user behavior analysis. For example, it detects a case in which an attacker uses a leaked AccessKey pair to purchase a large number of ECS instances for cryptomining. | |
AccessKey pair leak detection | Monitors public code platforms such as GitHub and detects whether your AccessKey pair appears in public source code. If a leak risk is detected, Security Center immediately generates an alert so that you can handle the risk at the earliest opportunity. | |
Compliance check | Provides MLPS compliance check and ISO 27001 Compliance Check capabilities to help you evaluate the security compliance status of your system, meet MLPS compliance assessment requirements, and obtain ISO 27001 Certification. |
Get Security Center Basic
Security Center Basic is enabled for all Alibaba Cloud users by default. Verify your edition on the Overview page of the Security Center console.
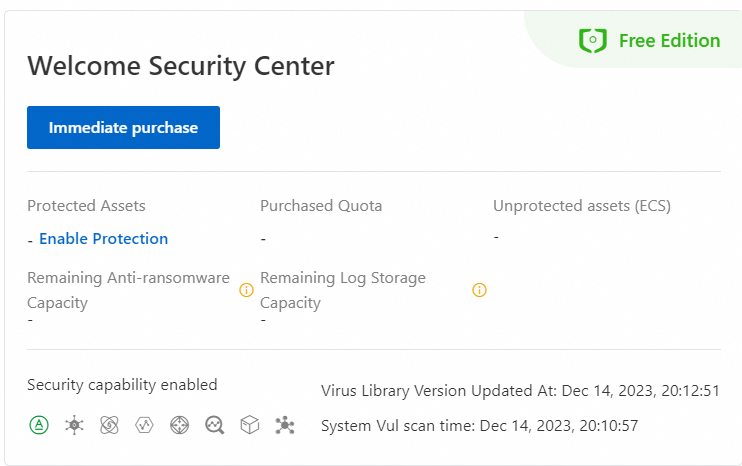
Enable server protection
After you install the Security Center agent on a server, Security Center begins protecting it.
Install the agent in one of the following ways:
Alibaba Cloud ECS instance
When you purchase an ECS instance, select Alibaba Cloud Security Large Model. This automatically installs the agent on the ECS instance.

Manually install the agent in the Security Center console. Install the agent.
Servers hosted outside of Alibaba Cloud
Manually install the agent from the Security Center console. Install the agent.
Apply for a 7-day free trial
If you have purchased an Alibaba Cloud ECS instance but Security Center Basic cannot meet your security protection requirements, you can apply for a 7-day free trial of Security Center Enterprise or Ultimate to experience more advanced protection capabilities.