Equal-Cost Multipath (ECMP) in Express Connect scales bandwidth by distributing traffic across multiple physical connections, preventing link congestion and improving resource utilization.
Use case
An enterprise connects its on-premises data center (IDC) in Shanghai to Alibaba Cloud through ECMP link aggregation with two Express Connect circuits from different carriers.
The IDC uses the CIDR block 172.16.0.0/12, and the VPC in the China (Shanghai) region uses 192.168.0.0/16. Two Express Connect circuits are provisioned to address bandwidth bottlenecks.
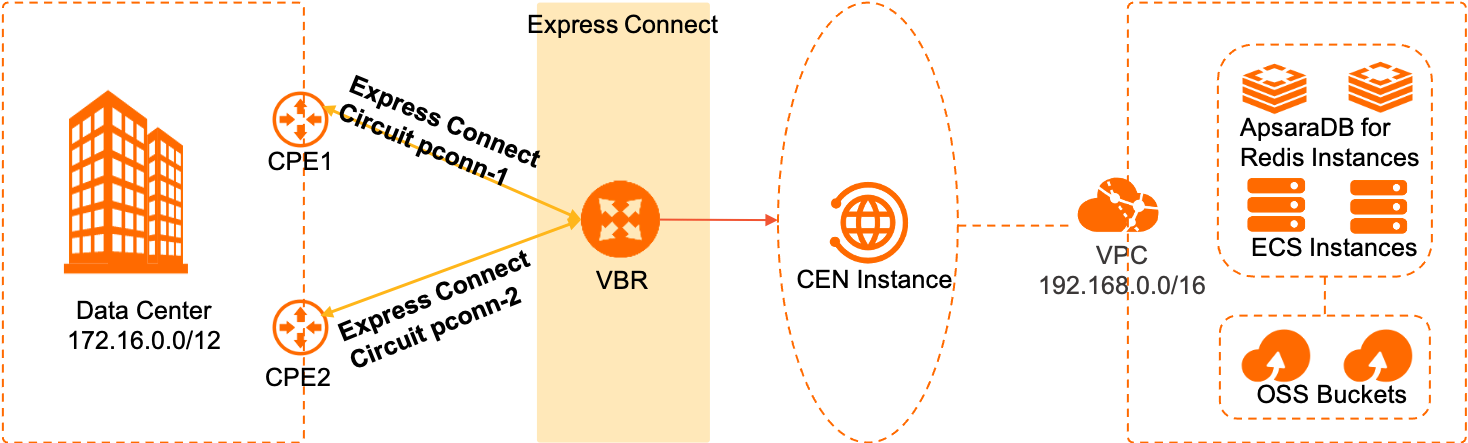
The following table lists the VBR configuration for the two Express Connect circuits.
VBR parameter | Express Connect circuit pconn-1 | Express Connect circuit pconn-2 |
VLAN ID | 1 | 1 |
Alibaba Cloud-side IPv4 interconnect IP | 10.4.4.1 | 10.4.5.1 |
Customer-side IPv4 interconnect IP | 10.4.4.2 | 10.4.5.2 |
IPv4 subnet mask | 255.255.255.252 | 255.255.255.252 |
Background information
An Enterprise Edition transit router in Cloud Enterprise Network (CEN) automatically learns and distributes routes. After route configuration, the transit router synchronizes routes across connected network instances. Each node learns routes as follows:
You can use static routes or BGP dynamic routing. The configuration differs for each method:
Alibaba Cloud side: set the static route destination to the on-premises IDC CIDR block, or for BGP, set the peer IP to the customer-side gateway IPv4 address.
On-premises IDC side: set the static route destination to the VPC CIDR block, or for BGP, set the peer IP to the Alibaba Cloud-side gateway IPv4 address.
This topic uses dynamic BGP routing.
BGP routing information on the VBR
Destination CIDR block
Next hop
VBR Route 1
172.16.0.0/12
10.4.4.2
VBR Route 2
172.16.0.0/12
10.4.5.2
VBR Route 1 and VBR Route 2 show routes learned from BGP peers. After you create a VBR connection on the transit router, the VBR forwards these routes to the transit router.
Complete route configuration
Destination CIDR block
Next hop
VBR Route 1
172.16.0.0/12
10.4.4.2
VBR Route 2
172.16.0.0/12
10.4.5.2
Route Table
172.16.0.0/12
VBR
192.168.0.0/16
VPC
After you create VBR and VPC connections on the transit router, the VBR forwards routes learned from the on-premises IDC to the transit router, which then advertises them to connected network instances such as the VPC.
The transit router also redistributes its system routes into BGP. The on-premises IDC BGP route table then shows routes from the transit router, with next hops pointing to the two VBR peer IP addresses.
Prerequisites
ECMP is not enabled by default. Contact your account manager to enable it.
You have provisioned Express Connect circuits that meet the following requirements. Apply for Classic Mode.
The Express Connect circuits are deployed on the same core switch.
The status of the Express Connect circuit is Enabled.
The Express Connect circuits have the same bandwidth.
You have created a VPC in the China (Shanghai) region of Alibaba Cloud, and deployed related services in the VPC by using cloud resources such as Elastic Compute Service (ECS).For more information, see Create a VPC with an IPv4 CIDR block.
NoteBefore you create a VPC connection on an Enterprise Edition transit router, ensure the VPC has at least one vSwitch in a transit router-supported zone with at least one available IP address. In this example, the transit router is in the China (Shanghai) region (Zone F and Zone G).
You understand the security group rules of the ECS instances in the VPC. Make sure that the rules allow the ECS instances to communicate with the data center. For more information, see View security group rules and Add a security group rule.
A CEN instance is created. Create a CEN instance.
An Enterprise Edition transit router is created in the region where the VPC resides. For more information, see Create a transit router.
Step 1: Create a VBR for an Express Connect circuit
Log on to the Express Connect console.
In the top navigation bar, select a region.
On the Physical Connection page, click the instance ID of the physical connection interface (pconn-1) for which you want to create a VBR and whose status is Enabled.
On the details page of the Express Connect circuit, click Create VBR.
In the Create VBR panel, configure the parameters and click OK.
Parameter
Description
Account
Account that owns the VBR.
This example uses Current Account.
Name
Enter a name for the VBR.
Physical Connection Interfaces
Select the pconn-1 interface. Ensure the circuit is provisioned and running.
VLAN ID
Enter the VLAN ID for the VBR.
This example uses 1.
VBR Bandwidth
Set the bandwidth for the VBR.
This example uses 200 Mbps.
Alibaba Cloud-side IPv4 Interconnect IP
Gateway IP for routing traffic from the VPC to the on-premises IDC.
This example uses 10.4.4.1.
Customer-side IPv4 Interconnect IP
Gateway IP for routing traffic from the on-premises IDC to the VPC.
This example uses 10.4.4.2.
IPv4 Subnet Mask
Subnet mask for the Alibaba Cloud-side and customer-side IPv4 addresses.
This example uses 255.255.255.252.
Step 2: Add a second Express Connect circuit to the VBR
Log on to the Express Connect console.
In the top navigation bar, select a region.
On the Physical Connection page, click the instance ID of the physical connection interface (pconn-1) for which a VBR has been created.
On the details page of the Express Connect circuit, click the ID of the VBR that you created.
On the Physical Connection Interfaces tab, click Add Physical Connection Interface.
In the Add Physical Connection Interface panel, configure the parameters for the second Express Connect circuit and click OK.
Parameter
Description
Physical Connection Interfaces
Select the Express Connect circuit interface to associate with the VBR. Ensure the circuit is provisioned and running.
This example uses pconn-2.
VLAN ID
Enter the VLAN ID for the VBR.
This example uses 1.
Alibaba Cloud-side IPv4 Interconnect IP
Gateway IP for routing traffic from the VPC to the on-premises IDC.
This example uses 10.4.5.1.
Customer-side IPv4 Interconnect IP
Gateway IP for routing traffic from the on-premises IDC to the VPC.
This example uses 10.4.5.2.
IPv4 Subnet Mask
Subnet mask for the Alibaba Cloud-side and customer-side IPv4 addresses.
This example uses 255.255.255.252.
Step 3: Configure BGP routing on the VBR
To establish dynamic BGP routing between the on-premises IDC and the VBR, create a BGP group and configure BGP peers for each Express Connect circuit.
Log on to the Express Connect console.
In the top menu bar, select the target region, and then in the left-side navigation pane, click Virtual Border Routers (VBRs).
On the Virtual Border Routers (VBRs) page, click the target VBR instance ID.
Configure a BGP group.
Click the BGP Groups tab and then click Create BGP Group.
Configure the BGP group and click OK.
Parameter
Description
Name
Enter a name for the BGP group.
Peer ASN
AS number of your on-premises network.
BGP Key
Enter the key for the BGP group.
Description
Enter a description for the BGP group.
Configure BGP peers.
Click the BGP Peers tab and then click Create BGP Peer.
Configure the BGP peer and click OK.
Parameter
Description
BGP Groups
Select the BGP group that you created.
BGP Peer IP Address
BGP peer IP address. In this example, enter 10.4.4.2 (customer-side interconnect IP).
Enable BFD
BFD is disabled in this example.
Repeat Step5 to configure the BGP neighbor of physical connection pconn-2 in the created BGP group.
In this example, the BGP peer IP of pconn-2 is set to 10.4.5.2, and BFD is disabled.
Step 4: Connect the VPC and VBR to the transit router
Create a VBR connection and a VPC connection on the transit router in the China (Shanghai) region. The VBR connection links the transit router to your Express Connect circuits, and the VPC connection links it to your VPC, enabling private communication between the on-premises IDC and the cloud.
Log on to the CEN console.
On the CEN Instance page, click the ID of the CEN instance that you want to manage.
On the tab, find the transit router instance in the target region and click Create Connection in the Actions column.
On the Connection with Peer Network Instance page, configure the following parameters to create a VPC connection, and then click OK.
NoteWhen you perform this operation for the first time, the system automatically creates a service-linked role named AliyunServiceRoleForCEN. This role allows the transit router to create an ENI in a vSwitch of the VPC. For more information, see AliyunServiceRoleForCEN.
Parameter
Description
Instance Type
The type of network instance.
In this example, VPC is selected.
Region
The region in which the VPC is deployed.
In this example, China (Shanghai) is selected.
TR
The system automatically displays the transit router in the selected region.
Account
The Alibaba Cloud account to which the VPC belongs.
In this example, Your Account is selected.
Billing Method
The billing method of the transit router is Pay-As-You-Go by default.
For more information, see Billing overview.
Network Instance
The ID of the VPC.
In this example, the VPC that you created is selected.
vSwitch
Select at least two vSwitches in a zone supported by the transit router.
Advanced Settings
The system selects three advanced features for you by default, namely Associate with Default Route Table of Transit Router, Propagate System Routes to Default Route Table of Transit Router, and Auto-add transit router routes to all VPC route tables.
In this example, the default settings are used.
On the Connection with Peer Network Instance page, click {value, select, continue {Create More Connections} setTRRouter {Configure Route Table} gotoList {Return to the List} createCross {Create More Cross-region Connections} Other {{value}} }.
On the Connection with Peer Network Instance page, configure the following parameters to create the VBR1 connection, and then click OK.
Parameter
Description
Instance Type
In this example, VBR is selected.
Region
The region in which the VBR is deployed.
In this example, the China (Shanghai) region is selected.
TR
The system automatically displays the transit router in the selected region.
Account
The Alibaba Cloud account to which the VBR belongs.
In this example, the default value Your Account is used.
Network Instance
The ID of the VBR.
In this example, VBR1 is selected.
Advanced Settings
The system selects three advanced features for you by default, namely Associate with Default Route Table of Transit Router, Propagate System Routes to Default Route Table of Transit Router, and Propagate Routes to VBR.
In this example, the default settings are used.
After the network connection is created, you can view the information about the VPC connection and the VBR connection on the Intra-Region Connections tab. For more information, see View network instance connections.
Step 5: Configure routing on the on-premises side
Configure BGP on your on-premises customer-premises equipment (CPE) to advertise routes to Alibaba Cloud. The on-premises IDC network is 172.16.0.0/12. The following table lists sample BGP configurations for the two CPE devices. For specific commands, consult your equipment vendor.
Parameter | CPE1 | CPE2 |
VLAN ID | 1 | 1 |
Network | 172.16.0.0/12 | 172.16.0.0/12 |
BGP ASN | 65000 | 65000 |
PEER BGP ASN | 45104 | 45104 |
Interface IP | 10.4.4.2/30 | 10.4.5.2/30 |
Step 6: Test connectivity
After configuration, verify connectivity over the redundant Express Connect circuits.
On a PC in your on-premises IDC, open a command-line window.
Run the ping command to check the network connectivity between the on-premises IDC and an ECS instance in the 192.168.0.0/16 CIDR block of the VPC.
A successful ping response confirms the connection.
Run the tracert command to verify that load balancing is active across the redundant circuits.
The specific command varies by device. Consult your equipment vendor.