Agentic NDR is the last line of defense for securing business asset traffic in cloud environments. This topic describes the use cases of Agentic NDR.
Major event protection and threat tracing
Challenges
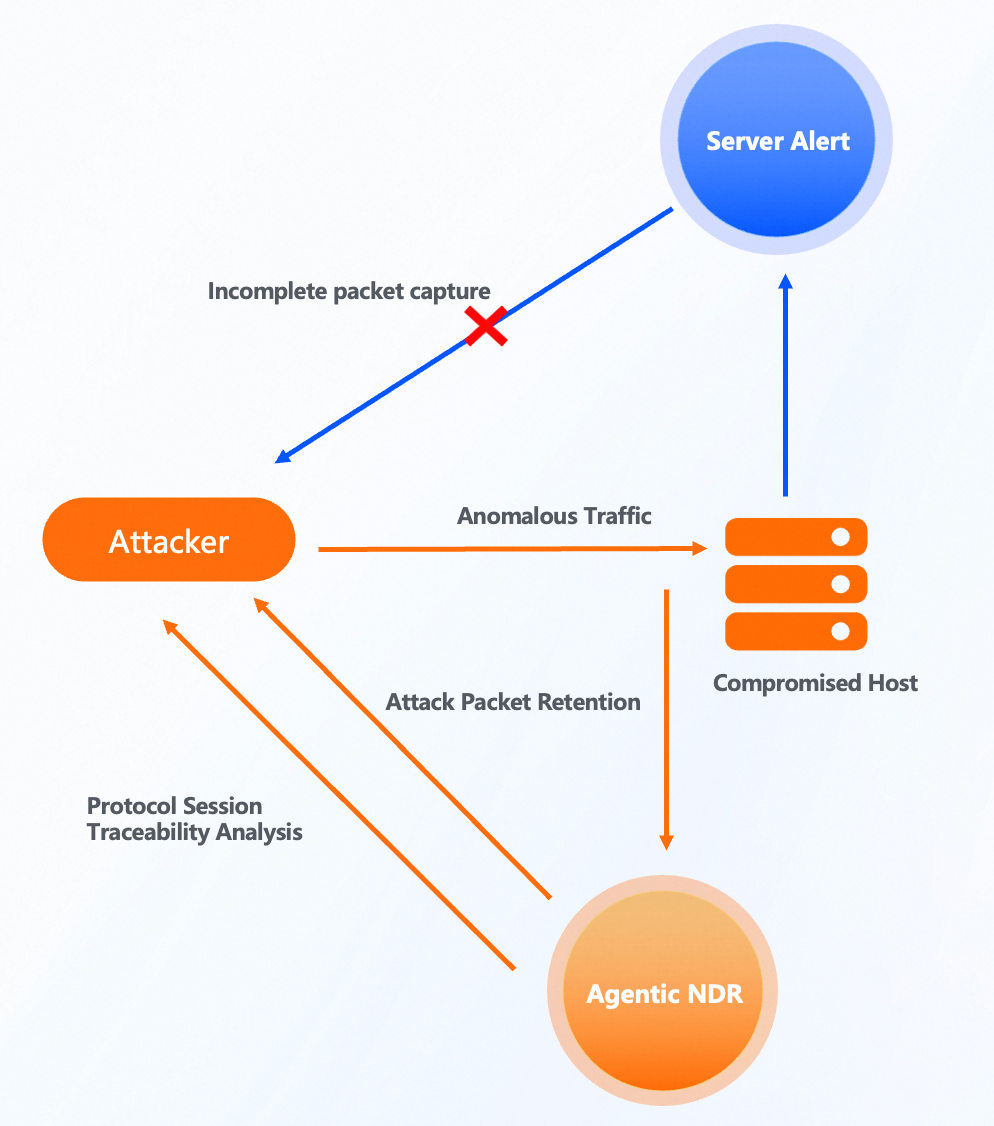
During major event protection periods, network security is especially critical. Attackers may exploit this timing to launch advanced attacks such as APT attacks, zero-day exploits, and stealth attacks, attempting to disrupt normal operations or steal sensitive information. In this highly adversarial environment, security operations teams must not only detect alerts but also trace attacks based on traffic, analyze the attacker's path and techniques, and proactively deploy targeted defenses. However, most perimeter protection devices only generate security event alerts without storing the original attack traffic, leaving security teams unable to perform attack tracing or confirm the specifics of anomalous traffic, which poses significant security risks.
Solution
Agentic NDR uses its threat analysis and multiple detection engines to cover a broader range of threat types. When an alert is generated, Agentic NDR simultaneously retains the attack event packets and the original traffic before and after the attack, enabling security teams to trace the attack, understand the attacker's techniques and tools, identify the intrusion path, confirm the attacker's identity and motives, and pursue legal accountability when necessary — all while keeping storage costs under control by avoiding the retention of irrelevant traffic.
Asset risk assessment and sensitive data leak detection
Challenges
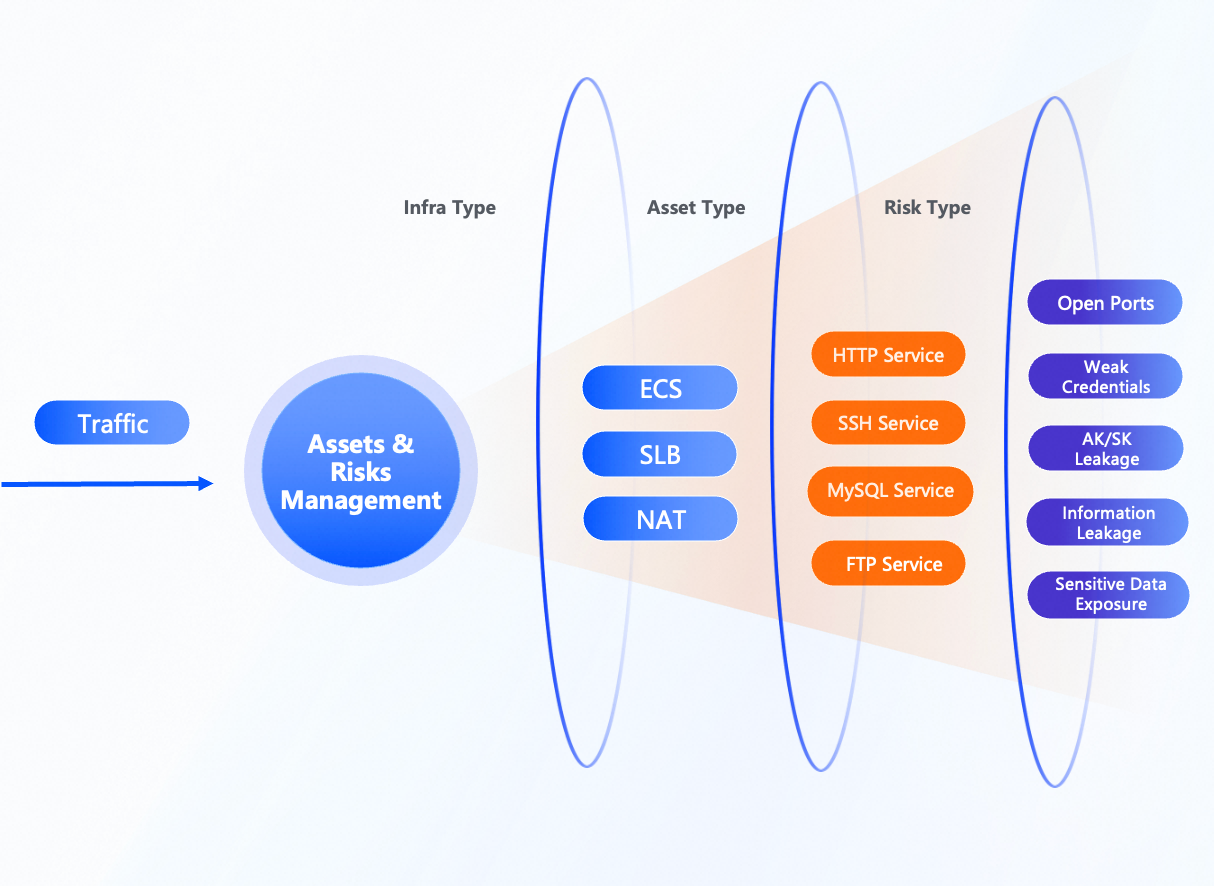
Organizations in industries such as finance and healthcare handle large volumes of sensitive, high-value data. Attackers actively seek to steal this data for illegal profit or competitive advantage. Risks such as unauthorized port exposure, sensitive data leaks, and weak asset passwords are easily exploited. A single data breach can cause significant financial losses and reputational damage.
Solution
Before protecting enterprise assets and data, you must first know which business assets are at risk. Agentic NDR's asset management and risk management capabilities automatically inventory your cloud asset types and services, quickly identifying unauthorized port exposure, weak-password logins, and sensitive data exposure. This helps you identify risk asset areas and flag business interfaces that transmit sensitive data.
Strictly regulated log compliance and traffic audit
Challenges
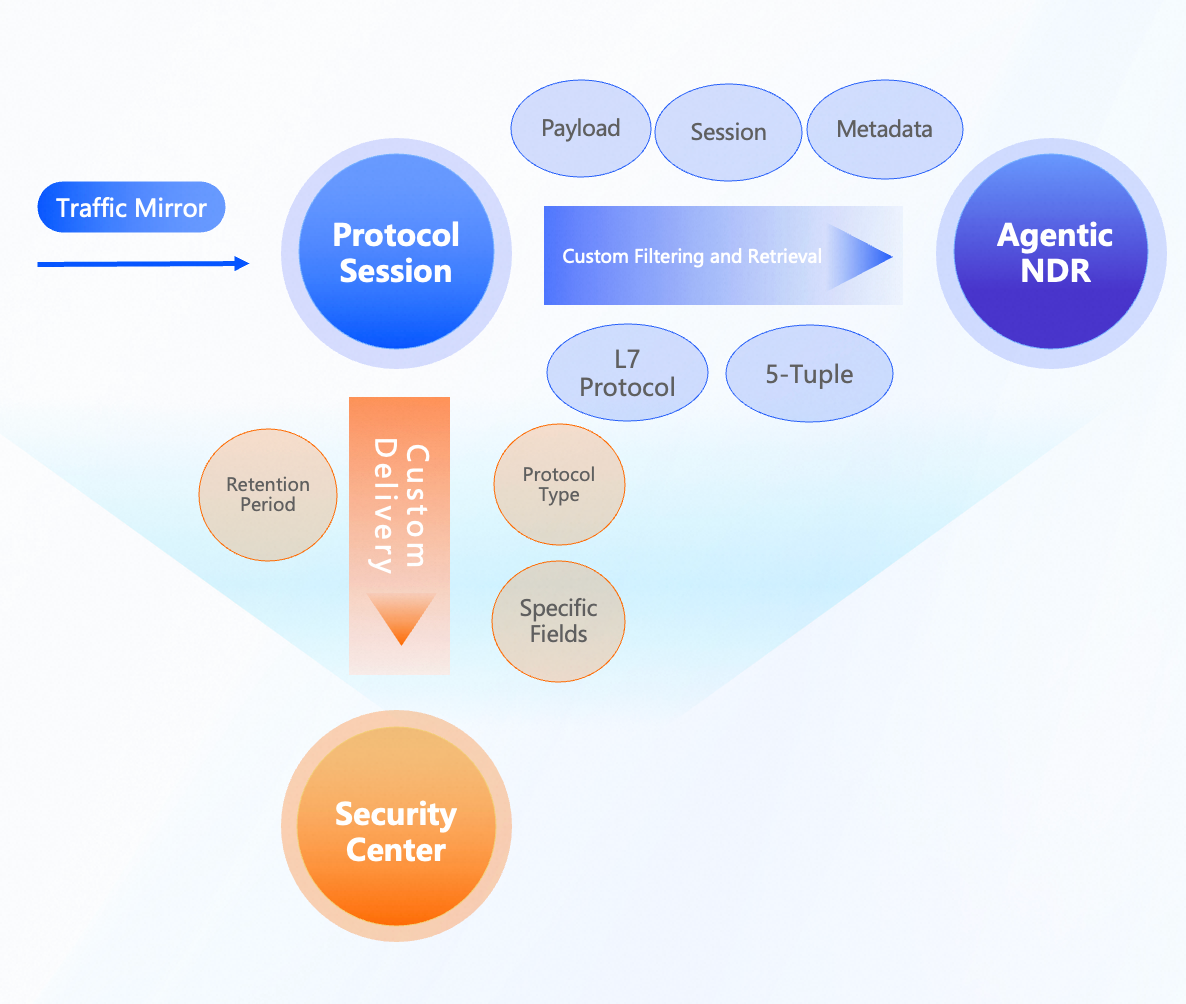
Some organizations have high requirements for log auditing and centralize on-premises business logs into self-built SIEM and SOC platforms. However, the cloud lacks effective full-traffic threat analysis, with issues such as incomplete Layer 7 bidirectional business logs and cumbersome retrieval and delivery operations. These organizations need comprehensive traffic analysis and auditing for cloud asset access behavior.
Solution
Agentic NDR performs effective detection of bidirectional full traffic in the cloud. Using its protocol log retrieval, filtering, and delivery capabilities, it generates comprehensive log information on demand. You can visually analyze and retrieve logs directly on the Agentic NDR console, and customize protocol types and specific fields for delivery to on-premises SIEM platforms for centralized auditing.