You can use a RAM role from Resource Access Management (RAM) to grant cross-account access. This allows an enterprise to access the ApsaraMQ for Kafka resources of another enterprise.
Background
Company A has enabled ApsaraMQ for Kafka and needs Company B to manage its ApsaraMQ for Kafka resources, such as instances, topics, and Groups, on its behalf. Company A has the following requirements:
Company A wants to focus on its business systems and act only as the owner of the ApsaraMQ for Kafka service. It wants to authorize Company B to handle operational tasks, such as O&M, monitoring, and management of ApsaraMQ for Kafka.
Company A wants to avoid making permission changes when employees join or leave Company B. Company B should be able to delegate access to Company A's resources to its own RAM users (employees or applications) and manage their access permissions at a fine-grained level.
Company A wants to be able to revoke Company B's access at any time, for example, if their contract is terminated.
Step 1: Create a RAM role as Company A
Log on to the RAM console with Company A's Alibaba Cloud account to create a RAM role for Company B's Alibaba Cloud account.
-
Log on to the RAM console as a RAM administrator.
-
In the left-side navigation pane, choose .
-
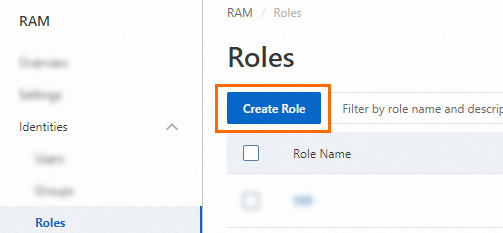
On the Roles page, click Create Role.
-
On the Create Role page, set Principal Type to Cloud Account, specify the trusted Alibaba Cloud account, and then click OK.

-
Current Account: When you want to allow all RAM users and RAM roles under the current Alibaba Cloud account to assume the RAM role that you are creating, you can select Current Account.
-
Other Account: To allow all RAM users and RAM roles that belong to another Alibaba Cloud account to assume the RAM role that you are creating, select Other Account and enter the ID of the other Alibaba Cloud account (main account). This option is mainly used for scenarios where you authorize access to resources across Alibaba Cloud accounts. For more information, see Access resources across Alibaba Cloud accounts.You can find your Alibaba Cloud account ID (main account) on the Security Settings page.
-
In the Role Name text box, enter a name for the RAM role. In the Select Trusted Alibaba Cloud Account section, select Other Alibaba Cloud Account, enter Company B's Alibaba Cloud account ID, and then click Completed.
NoteA RAM role name can contain letters, digits, and hyphens (-) and be up to 64 characters long.
You can find the account ID on the Security Settings page of the Account Management console.
Step 2: Grant permissions to the RAM role
Grant the RAM role permissions to access ApsaraMQ for Kafka.
Log on to the RAM console as a RAM administrator.
In the left-side navigation pane, choose .
On the Roles page, find the target RAM role and click Grant Permission in the Actions column.
In the Policy section of the Grant Permission panel, enter the name of the policy that you want to add in the search box. Click the policy to add it to the Selected Policies list on the right. Then, click Confirm Grant Permission.
NoteFor information about the policies for authorizing access to ApsaraMQ for Kafka, see RAM policies.
Step 3: Create a RAM user as Company B
Log on to the RAM console with the Alibaba Cloud account of Company B and create a RAM user.
Procedure
Console
Sign in to the RAM console using your Alibaba Cloud account or as a RAM user with administrative permissions (a user to which the
AliyunRAMFullAccesspolicy is attached).In the left-side navigation pane, choose .
On the Users page, click Create User.
On the Create User page, in the User Account Information section, configure the user's basic information.
Logon Name (required): The name can contain letters, digits, periods (.), hyphens (-), and underscores (_), and be up to 64 characters long.
Display Name (optional): The name can be up to 128 characters long.
Tag (optional): Click
 , and then enter a tag key and tag value. Tags help you categorize and manage users.
NoteClick Add User to create multiple RAM users in bulk.
In the Access Mode section, select an access mode based on the user type.
ImportantAs a security best practice, select only one access mode per user. This creates a clear separation between human users who require console access and applications that require programmatic access.
If an AccessKey pair is leaked, your account's security is compromised. Prioritize using Security Token Service (STS) tokens, which are temporary credentials, to reduce the risk of leaks. For more information, see Best practices for using access credentials to call Alibaba Cloud APIs.
Console accessConsole Access
Select Console Access.
Set Logon Password: You can choose to automatically generate a password or set a custom one. A custom password must meet the configured password complexity requirements. For more information, see Set a password policy for RAM users.
Password Reset: Select whether the RAM user must reset their password at the next sign-in.
Enable MFA: By default, multi-factor authentication (MFA) is required for all users to sign in. To change this setting, see Manage security settings for RAM users. RAM users must bind an MFA device when they first sign in. For more information, see Bind an MFA device.
Programmatic access
Select Using permanent AccessKey to access.
After enabling this option, the system automatically creates an AccessKey ID and an AccessKey secret for the RAM user.
ImportantA RAM user's AccessKey secret is displayed only during creation and cannot be retrieved later. You must immediately download or copy and save the AccessKey secret. A leaked AccessKey pair severely compromises the security of all resources under your account. For more information, see Create an AccessKey pair.
OpenAPI
Create a RAM user for console access
Call GetDefaultDomain to obtain the default logon suffix of an account. The format is
<AccountAlias>.onaliyun.com.Call the CreateUser operation to create a RAM user. The following parameters are required:
UserPrincipalName: The logon name for a RAM user. The format is<username>@<AccountAlias>.onaliyun.com, where<username>is the RAM username and<AccountAlias>.onaliyun.comis the default logon suffix.DisplayName: The display name for the RAM user. It can be different from the<username>above.
Call the CreateLoginProfile operation to create a login profile, and configure the access mode and MFA requirements. The recommended settings for some parameters are as follows:
UserPrincipalName: The information of the user created in the previous step.Password: Set the password according to the password strength requirements for the account. You can call the GetPasswordPolicy operation to query the password strength policy for RAM users in the current account.MFABindRequired: We recommend that you require RAM users to enable MFA. The recommended parameter value istrue.Status: Specifies whether to enable console password logon. The default value isActive.
Create a RAM user for programmatic access
Call GetDefaultDomain to obtain the default logon suffix for an account. The suffix is in the format
<AccountAlias>.onaliyun.com.Call the CreateUser operation to create a RAM user. The following parameters are required:
UserPrincipalName: The logon name of a RAM user in the format<username>@<AccountAlias>.onaliyun.com, where<username>is the RAM username and<AccountAlias>.onaliyun.comis the default logon suffix.DisplayName: The display name for the RAM user, which can be different from the<username>above.
To create an AccessKey pair (AccessKey), call the CreateAccessKey operation and pass only the
UserPrincipalNamefor the user that you created in the previous step.ImportantThe response to the
CreateAccessKeyAPI call contains the AccessKeyId and AccessKeySecret. The AccessKeySecret is provided only in this response and cannot be retrieved later. You must save it immediately. Leaking an AccessKey severely threatens the security of all resources in your account. For more information, see Create an AccessKey.
Step 4: Grant permissions to the RAM user
Attach the AliyunSTSAssumeRoleAccess policy to the RAM user.
Log on to the RAM console.
In the left-side navigation pane, choose .
On the Users page, find the RAM user that you created and click Attach Policy in the Actions column.
In the Policy area of the Grant Permission panel, enter the policy that you want to add in the search box, click the policy to add it to the Selected Policies list on the right, and then click Grant Permission.
Next steps
A RAM user from Company B can access Company A's ApsaraMQ for Kafka in the following ways.
Console
In a browser, open the RAM User Logon page.
On the RAM User Logon page, enter the RAM user name, click Next, enter the password, and then click Log On.
NoteThe RAM user logon name is in the format <$username>@<$AccountAlias> or <$username>@<$AccountAlias>.onaliyun.com. <$AccountAlias> is the enterprise alias. If no account alias is set, the ID of the Alibaba Cloud account is used as the alias.
On the RAM user's homepage, move the pointer over the profile picture in the upper-right corner and click Switch Identity.
On the Switch Role page, enter the enterprise alias or default domain name of Company A and the RAM role name, and then click Submit.
NoteEnterprise alias: Log on to the Alibaba Cloud console with Company A's Alibaba Cloud account. Move the pointer over the profile picture in the upper-right corner to view the alias.
Default domain name: Log on to the RAM console with Company A's Alibaba Cloud account. On the Setting page, click the Advanced Settings tab to view the default domain name.
API
Call the AssumeRole operation to obtain an access key ID, an access key secret, and an STS token. For more information, see AssumeRole.
Use the obtained credentials (access key ID, access key secret, and STS token) to call APIs and access ApsaraMQ for Kafka.