The protection rules engine uses a built-in set of protection rules to automatically defend your website against common web attacks, such as SQL injection, cross-site scripting (XSS), webshell uploads, command injection, backdoor isolation, illegal file requests, path traversal, and attacks that exploit common application vulnerabilities.
Prerequisites
-
You have activated a Web Application Firewall instance.
-
Your website has been added to WAF. For more information, see Tutorials.
Background
The protection rules engine in WAF is enabled by default. It automatically inspects and protects all websites added to WAF.
The protection rules engine uses an extensive set of basic protection rules from the Alibaba Cloud security team to defend against various common web application attacks. You can configure which protection rules the engine uses by selecting a protection rule group based on your business needs. WAF provides three built-in rule groups with different strictness levels:
Medium Rule Group: This rule group is selected by default.
Loose Rule Group: This rule group is designed to reduce false positives.
Strict Rule Group: This rule group is designed to improve the attack detection rate.
You can also create a custom protection rule group. For more information, see custom protection rule groups.
The Protection Rules Engine mitigates common web attack threats, but does not guarantee a 100% block rate. If an attack is not blocked, you can first analyze the request features and rule hit records. Then, you can use custom mitigation policies to configure specific protection rules. For more information, see Configure a custom protection policy.
Intelligent Rule Hosting
Intelligent Rule Hosting is enabled by default in the protection rules engine to prevent false positives that might affect legitimate traffic.
Intelligent Rule Hosting learns your website's historical traffic patterns. Using Alibaba Cloud threat intelligence, it identifies rules that could cause false positives for your business scenarios or API endpoints. The feature then automatically adds fine-grained Web Intrusion Prevention whitelist rules. These rules typically target a specific API endpoint URL and ignore a specific Rule ID, to minimize false positives without expanding the attack surface. Once the false positive risk is eliminated, the engine automatically deletes these rules.
Procedure
-
Log on to the Web Application Firewall console.
-
In the top menu bar, select the resource group and region for your Web Application Firewall instance (Chinese Mainland or Outside Chinese Mainland).
-
In the left navigation pane, choose .
-
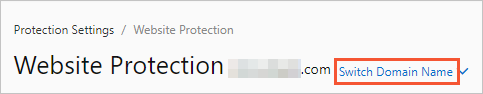
On the Website Protection page, switch to the domain name to configure.
Click the Web Security tab, go to the Protection Rules Engine section, and configure the following parameters.
Parameter
Description
Status
Enables or disables the protection rules engine. By default, the protection rules engine is enabled to defend all websites added to WAF against common web application attacks.
On the Security Report page, you can view the attack logs from the protection rules engine in the report. If you find that a rule incorrectly blocks legitimate service traffic, you can use the Ignore False Positives feature to suppress the specified rule. For more information, see Web Security reports.
Mode
The action to perform on requests identified as attacks. Valid values:
Block: Blocks attack requests.
Alert: Generates alerts for attack requests but does not block them.
Intelligent Rule Hosting
Enables or disables Intelligent Rule Hosting. By default, this feature is enabled to dynamically manage the Web Intrusion Prevention whitelist and reduce false positives.
In the Protection Rules Engine section, a message appears stating, "XX rules have been intelligently optimized." Click Click to go to the Web Intrusion Prevention - Whitelist page, which lists the whitelist rules automatically added by the engine. For these rules, Rule Source is set to Intelligent Rule Hosting. You can edit or delete these automatically added whitelist rules.
The engine automatically deletes these rules once the risk of false positives is eliminated.
ImportantEven if you manually edit a rule that was automatically added, the engine will still delete it after the risk of false positives is eliminated.
The engine does not automatically delete whitelist rules that you create manually.
Protection Rule Group
Select the protection rule group that you want to apply. You can apply a built-in rule group or a custom protection rule group. The built-in rule groups include:
Medium Rule Group: Detects common web application attacks based on a standard protection level. This rule group is applied by default.
Strict Rule Group: Detects web application attacks such as path traversal, SQL injection, and command injection based on a strict protection level.
Loose Rule Group: Detects common web application attacks based on a loose protection level. We recommend that you select this rule group if you experience a high number of false positives with the Medium rule group, or if your business involves large volumes of uncontrollable user input, such as in rich-text editors or technical forums.
Click Configure Now to go to the Protection Rule Group configuration page. On this page, you can create a custom protection rule group and select the protection rules to apply based on your business needs. For more information, see custom protection rule groups.
Decoding Settings
Specify the content formats that you want the protection rules engine to decode for analysis.
By default, the protection rules engine decodes and analyzes content in all formats to ensure effective protection. If the engine frequently blocks legitimate requests that contain a specific format, you can deselect that format to reduce false positives.
You can expand the Decoding Settings menu and select or deselect the formats that you want to decode.
ImportantYou cannot deselect the following decoding formats: URL Decoding, JavaScript Unicode Decoding, Hex Decoding, Comment Processing, and Space Compression.
The optional decoding formats that you can deselect include: Multipart Parsing, JSON Parsing, XML Parsing, PHP Deserialization, HTML Entity Decoding, UTF-7 Decoding, Base64 Decoding, and Form Parsing. By default, all 13 decoding methods are selected.
Query protection rules
Use the following methods to query the WAF protection rules engine for the latest and all current protection rules:
Query the latest protection rules
On the Overview page of the WAF console, the Urgent Vulnerability list shows the latest protection rules added to the protection rules engine.
The Urgent Vulnerability section displays WAF's protection rule updates for newly disclosed security vulnerabilities.
Click an urgent vulnerability record to view the Details pane. This pane shows the affected domain names, vulnerability details, and related WAF protection rules.
The Urgent Vulnerability Protection Details dialog box contains the following fields: Protected Assets, Emergency Start Time, Rule Release Time, Vulnerability Name, Vulnerability ID (including a link to the CVE ID), Rule Name, Rule ID, Application Type, Protection Type, and Rule Description.
Query all protection rules
On the page of the WAF console, you can query all protection rules in the WAF protection rules engine.
To query the rules, perform the following steps:
On the Web Intrusion Protection tab, find the Strict Rule Group and click the number link in the Built-in Rules column.
The Strict Rule Group is a default, system-defined group in the protection rules engine. It contains all protection rules of the engine and cannot be modified.
NoteBecause the protection rules in the engine are updated dynamically, the number in the Built-in Rules column may not reflect the exact current count.
In the Number of Built-in Rules panel, find the protection rule that you want to view.
You can filter protection rules by Severity, Protection Type, or Application Type. You can also search for a specific rule by its Rule ID or CVE ID. For example, you can search by a Rule ID found on the Overview or Security Report page.
The rule list provides the following information: Severity/Rule Name, Rule ID, Updated At, Application Type, CVE ID, Protection Type, and Rule Description.
You can click a specific CVE ID to view the details of the corresponding vulnerability.
FAQ
Which common framework vulnerabilities does WAF protect against, and how can I find their rule IDs?
The protection rules of the Protection Rules Engine are continuously and dynamically updated. This topic does not list the specific mappings between vulnerabilities and rule IDs. For the most accurate information, refer to the current WAF rule set. You can verify this information using the method described in the Query protection rules section.
What should I do if the Protection Rules Engine blocks normal service traffic?
If the Protection Rules Engine blocks normal service traffic, troubleshoot and resolve the issue as follows:
Locate the rule causing the false positive: On the Security Report page, navigate to Web Security > Web Intrusion Prevention. Query the attack hit records of the Protection Rules Engine to find the specific rule that is causing the false positive.
Handle the false positive:
For a single false positive: If you confirm that a rule blocks normal service traffic, use the Ignore False Positives feature to shield the rule.
For multiple false positives: If many false positives occur, switch to a built-in rule group with a looser protection level, such as Loose Rule Group, in the Protection Rule Group settings.
Does the intelligent managed rule feature pose a security risk that attackers can exploit?
The intelligent managed rule feature does not pose a security risk that attackers can exploit.
This feature is powered by the Protection Rules Engine. The engine uses intelligent algorithms to learn from your website's historical traffic patterns and combines this information with Alibaba Cloud security threat intelligence. This process automatically detects rules that may cause false positives because they do not apply to your current business scenarios or interfaces. The system then automatically adds a Web Intrusion Protection whitelist rule with the smallest possible granularity. This rule typically targets a specific service interface URL and ignores a specific rule ID.
Therefore, the intelligent managed rule feature does not unconditionally allow all traffic or expand the attack impact scope. After the risk of false positives is resolved, the Protection Rules Engine automatically deletes the previously added whitelist rule.