After you add a website to Web Application Firewall (WAF), you can enable the positive security model for the website. The positive security model uses the machine learning algorithms that are developed by Alibaba Cloud to automatically learn the legitimate traffic of a website. Then, the model generates custom protection rules for the website based on the learning results to prevent unknown attacks.
Prerequisites
-
You have a Web Application Firewall instance of Ultimate Edition edition or higher.
-
Your website has been added to WAF. For more information, see Tutorials.
Background information
Traditional protection methods protect websites from attacks based on detection rules. The positive security model uses unsupervised learning to automatically learn the traffic of a website. Then, the positive security model uses the model that is built by machine learning algorithms to generate a standard security score and grade different requests. The positive security model defines the baseline traffic of the website and generates custom protection rules for the website based on the request scores. The positive security model integrates with other protection modules of WAF to defend against attacks at different network layers.

Procedure
-
In the top menu bar, select the resource group and region for your Web Application Firewall instance (Chinese Mainland or Outside Chinese Mainland).
-
In the left navigation pane, choose .
-
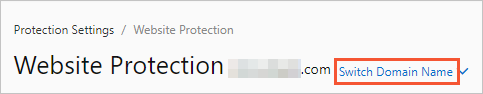
On the Website Protection page, switch to the domain name to configure.
-
Click the Web Security tab and go to the Positive Security Model section. The positive security model uses machine learning algorithms to automatically learn the legitimate traffic of a domain name and generate custom security policies. You can configure the feature by turning on the Status switch, selecting Block or Warn for the Mode, and viewing the Learning Status (such as "Model training") after the feature is enabled.
Parameter
Description
Status
The switch that enables or disables the positive security model.
Mode
The action that you want to perform on attacks that are detected by WAF. Valid values:
-
Alert: Only triggers a warning and does not block the attack request.
-
Block: Directly blocks attack requests.
NoteBy default, the positive security model is set to the Warn mode. In this mode, WAF records the requests that match the protection rules in security reports, but does not block the requests. Before you set the mode to Block, we recommend that you study the data in security reports and make sure that the protection rules do not cause false positives.
The first time that you enable the positive security model for a website, WAF uses the model that is built by machine learning algorithms to automatically learn the historical traffic of the website. Then, WAF generates custom protection rules based on the learning results to protect the website. The time that is required to initially learn the traffic varies based on the total amount of traffic. In most cases, WAF initially learns the traffic of a website and generates protection rules within approximately 1 hour. After WAF completes the learning process, WAF sends you a notification by using internal messages, text messages, or emails.
ImportantIf you disable the positive security model, the traffic learning results that are generated become invalid. If you re-enable the positive security model, the positive security model needs to relearn the traffic of the website. If you upgrade your WAF instance, the learning results of the positive security model are not affected. If the traffic pattern of the website that is added to WAF changes, the learning results are no longer applicable. We recommend that you configure the positive security model to relearn the traffic of the website. Traffic pattern changes include the change of the service type of the website.
-