Alibaba Cloud uses identities, credentials, and authorization to secure user access to cloud resources. An identity uniquely identifies a user, a credential verifies that identity, and authorization determines what resources the user can access.
Identity
An identity uniquely identifies a user. Alibaba Cloud determines user permissions based on identity and supports three types: Alibaba Cloud account, Resource Access Management (RAM) user, and RAM role.
-
Alibaba Cloud account
An Alibaba Cloud account owns all resources under it and has full permissions. The account is billed for all resource usage. Use a RAM user or RAM role to log on to the console and call API operations unless the Alibaba Cloud account is specifically required.
-
RAM user
An identity with a fixed ID and credential that represents a person or application. For more information, see Overview.
-
RAM role
A RAM role is a RAM identity type with attached policies. Unlike a RAM user, a role is not bound to a single person or application—any trusted principal can assume it. Roles have no long-term credentials such as passwords or AccessKey pairs. When a principal assumes a role, the Security Token Service (STS) generates temporary security credentials valid only for that session.
For example, Account A creates RAM role a_rr1, grants
FullAccesson Object Storage Service (OSS) to it, and assigns it to RAM user b_ru1 of Account B. RAM user b_ru1 can then assume a_rr1 to manage Account A's OSS resources.For more information, see Overview.
Credential
A credential verifies user identity. You must provide a valid credential to authenticate when you log on. Alibaba Cloud supports the following credential types:
-
An AccessKey pair of an Alibaba Cloud account or RAM user. An AccessKey pair consists of an AccessKey ID and an AccessKey secret and is permanently valid.
WarningAn AccessKey pair of an Alibaba Cloud account has full access to all account resources. Leaked AccessKey pairs pose critical security threats. Use the AccessKey pair of a RAM user and rotate it regularly. For information about how to create an AccessKey pair for a RAM user, see Create an AccessKey.
-
A Security Token Service (STS) token of a RAM role. STS tokens are temporary credentials with configurable validity periods and permissions. For more information, see STS overview
NoteSTS tokens have a validity period. You must update an STS token after it expires.
-
A bearer token for authentication and authorization. Only Cloud Call Center allows you to use a bearer token to initialize a Credentials client. To use a bearer token, select BearerToken for the Configure Authentication Mode parameter.
Credential leaks pose critical threats to cloud resources and your business. Prioritize credential security during routine O&M. For more information, see Credential security solutions.
Authorization
Authorization grants resource access permissions to users by system administrators or resource owners. After verifying a user's identity, the system determines whether the user can perform specific operations based on assigned permissions.
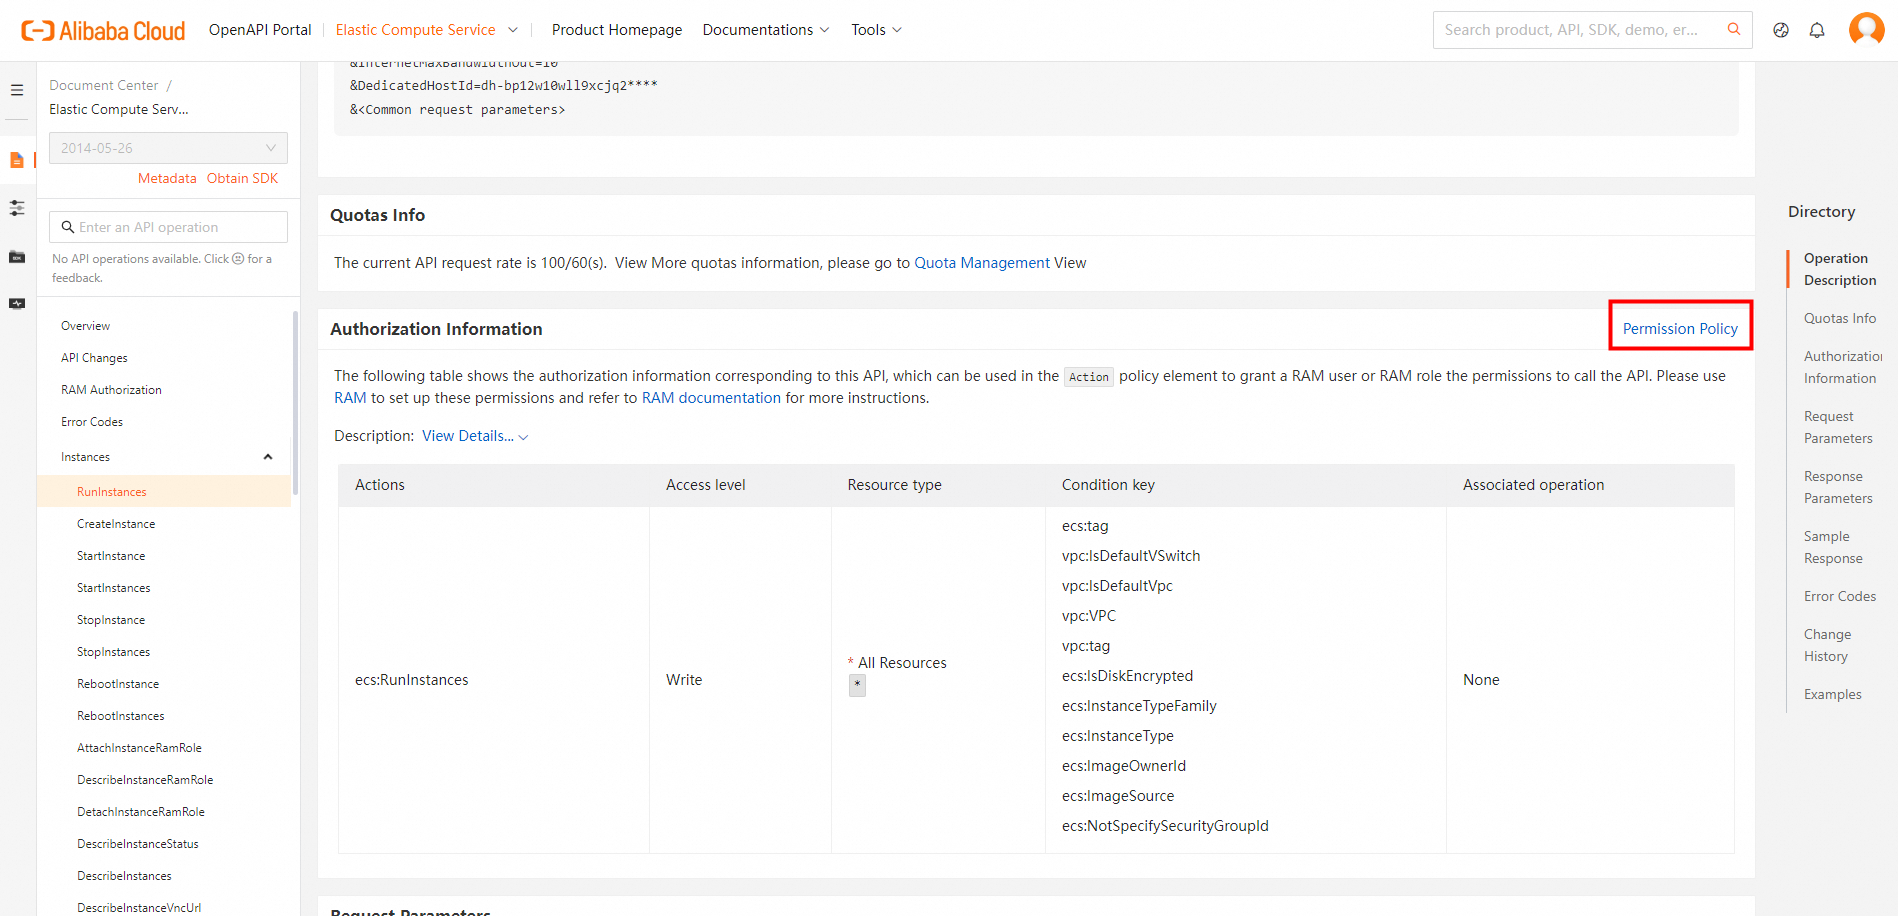
Each Alibaba Cloud API operation requires minimum permissions. View the required permissions on the API Docs page of the API operation in OpenAPI Explorer. The following figure shows the authorization information of the RunInstances operation of Elastic Compute Service (ECS).
-
Alibaba Cloud account
An Alibaba Cloud account has full, unmodifiable permissions on all resources within it. You do not need to grant permissions to an Alibaba Cloud account, and the permissions of an Alibaba Cloud account cannot be modified. However, if the account belongs to a resource directory, access control policies of that directory may apply. For more information, see Overview.
-
RAM user
You can grant the permissions displayed on the API Docs page of an API operation to a RAM user. For more information, see Manage RAM user permissions.
-
RAM role
Compared with authorization for a RAM user, authorization for a RAM role requires an additional step.
-
Specify the trusted entity of the RAM role: an Alibaba Cloud account, a RAM user, or another RAM role.
-
Grant required permissions. For more information, see Overview.
Consider the following scenarios when granting permissions to a RAM role:
Scenario 1: Authorization chain
For example, RAM user aRamUser1 of Account A can assume RAM role bRamRole1 of Account B, and bRamRole1 can assume RAM role cRamRole1 of Account C. Although aRamUser1 is not directly authorized to assume cRamRole1, it can access Account C's resources through bRamRole1. This is the authorization chain effect.
Scenario 2: Implicit authorization
If you set the current Alibaba Cloud account as the trusted entity of a RAM role, every RAM user or RAM role with
assumeRolepermission in that account can assume the role by default. If the role has elevated permissions, every RAM user or RAM role with onlyassumeRolepermission gains those elevated permissions. -