Row-level permission lets you control data access on a row-by-row basis, ensuring users see only the data they are authorized to access. This eliminates the need for separate views or sub-tables, reducing maintenance costs and securing your data. This topic describes how to add and manage row-level permission.
Prerequisites
You have purchased the row-level permission value-added service and the feature is enabled for the current tenant.
Limitations
A super administrator has full row and column permissions for all data tables and is exempt from row-level permission.
If row-level permission is enabled for a data table, the table owner has no row-level permission for that table unless they are on the authorization list.
Row-level permission is supported for both compute source tables and data source tables.
In offline development and analysis, you can view and perform a full download of row data that you are permitted to access. (Row-level permission applies only when querying table data and does not take effect when you modify the table structure, alter table data, or delete the table.)
In offline integration, when you select a project as the data table source, you can synchronize the row data that you have permission to access.
In Catalog - data preview, you can view the row data that you have permission to access.
When you create behavioral relationships or offline views, a production account can read the row data it has permission to access.
Row-level permission does not apply to API calls.
Row-level permission does not support cross-tenant publishing. You must create the row-level permission in the target tenant.
Permissions
System roles, including the super administrator and security administrator, as well as custom global roles with the Permission Management - Row-level Permission Management permission, can add and manage row-level permission.
Add row-level permission
In the Dataphin console, choose Management Center > Permission Management from the top menu bar.
In the left-side navigation pane, click Row-level Permission. On the Row-level Permission Management page, click +Add Row-level Permission to open the Add Row-level Permission page.
On the Add Row-level Permission page, configure the parameters.
Parameter
Description
Permission name
The name of the row-level permission. The name must be globally unique and be up to 64 characters long.
Description
A description of the row-level permission, up to 128 characters long.
Control field
Specify the fields to control. You can control access based on a combination of fields from a single table. The field name and description can be up to 64 characters long. Supported field types are text and numeric.
Click Add Control Field to add up to 10 control fields.
Control rule
Add a control rule for the permission. For configuration details, see Create a control rule.
When you add a new rule, the system adds a default rule that grants visibility to all rows. You can authorize users for this rule or enable or disable it.
You can edit or delete other rules.
Edit: Modify the configuration of the rule.
Delete: Deleting a rule revokes the permissions it granted.
Associated table
Add the data tables to control. You can perform Go to Asset and Delete operations on the added tables. For configuration details, see Add an associated table.
Go to Asset: Go to the details page of the current table in Catalog to view more information.
Delete: This action cannot be undone.
View affected production accounts
If a selected associated table has downstream tables, enabling row-level permission may affect their output tasks. We recommend that you grant the All rows visible permission to the production accounts of the projects where the downstream tables are located. For more information, see View affected production accounts.
Click OK to create the row-level permission.
Create control rule
Click +Create Control Rule. In the Add Control Rule dialog box, configure the parameters and click OK.
Parameter | Description |
Rule name | The name of the permission rule. The name must be unique within the permission and be up to 64 characters long. This rule name is displayed when you apply for permissions on the related data tables. |
Permission expression | Create an expression for the controlled fields. The system automatically populates the first control field. You can then select from all available control fields. The supported operators are described below:
You can add up to 20 rules, with each rule having a maximum of 5 levels of nesting. The filter conditions between each rule or relationship are AND or OR. Expression Preview: The system generates a SQL statement in real time based on the permission expression configuration. |
Authorized users | Click Add Authorized Account to grant permissions to users. Supported account types are personal account, production account, user group, and Data Service Application. Click the save Note You cannot re-authorize users who already have permission under the current rule. You must delete the existing authorization before granting a new one. |
 icon to add the account.
Add associated table
Click +Add Associated Table. In the Add Associated Table dialog box, configure the parameters and click OK.
You can add up to 50 data tables.
A single field cannot be associated with more than one control field.
If the associated field for a data table is empty, you cannot save the configuration. Use the quick filter to find and modify these tables before saving.
You can search for compute source tables and data source tables to associate. The system matches binding fields that have the same name and data type as the control field. You can modify these matches. To add data tables in batches, click Batch Search and Add. In the Batch Search dialog box, you can perform exact searches for compute source tables by using the ProjectName.TableName or BusinessCategory.TableName format, and for data source tables by using the DB/Schema.Table format. Separate multiple table names with semicolons (;), commas (,), or line breaks (\n). You can add up to 100 tables at a time.
Associated table list
You can perform a fuzzy search for associated tables by name, filter them by control field, or use the quick filter to find tables where the associated field is empty.
The filtered list displays information about the associated tables, including their names, parent business category/project/data source, associated fields, and control fields. You can also perform the following operations on the filtered tables.
Actions
Description
Go to Asset
Click the Go to Asset icon to open the table's details page in Governance > Asset Inventory.
Edit
Click the Edit icon to modify the associated field.
Delete
Click the Delete icon to remove all associated fields under the current table.
Affected production accounts
Click View Affected Production Accounts. In the Affected Production Accounts dialog box, configure the parameters and click OK.

Area | Description |
①Search | Search for affected production accounts. |
②List of affected production accounts | Displays the production account of the project to which the task belongs, its current permissions, and the permissions to be granted. You can also view the affected downstream tables.
|
③Authorize | Allows you to grant all row-level rules from the current row-level permission to production accounts in batches. Permissions configured here override those set in the Grant permissions section. |
Manage row-level permission
On the Row-level Permission Management page, you can view permission rules, associated tables, and related details.
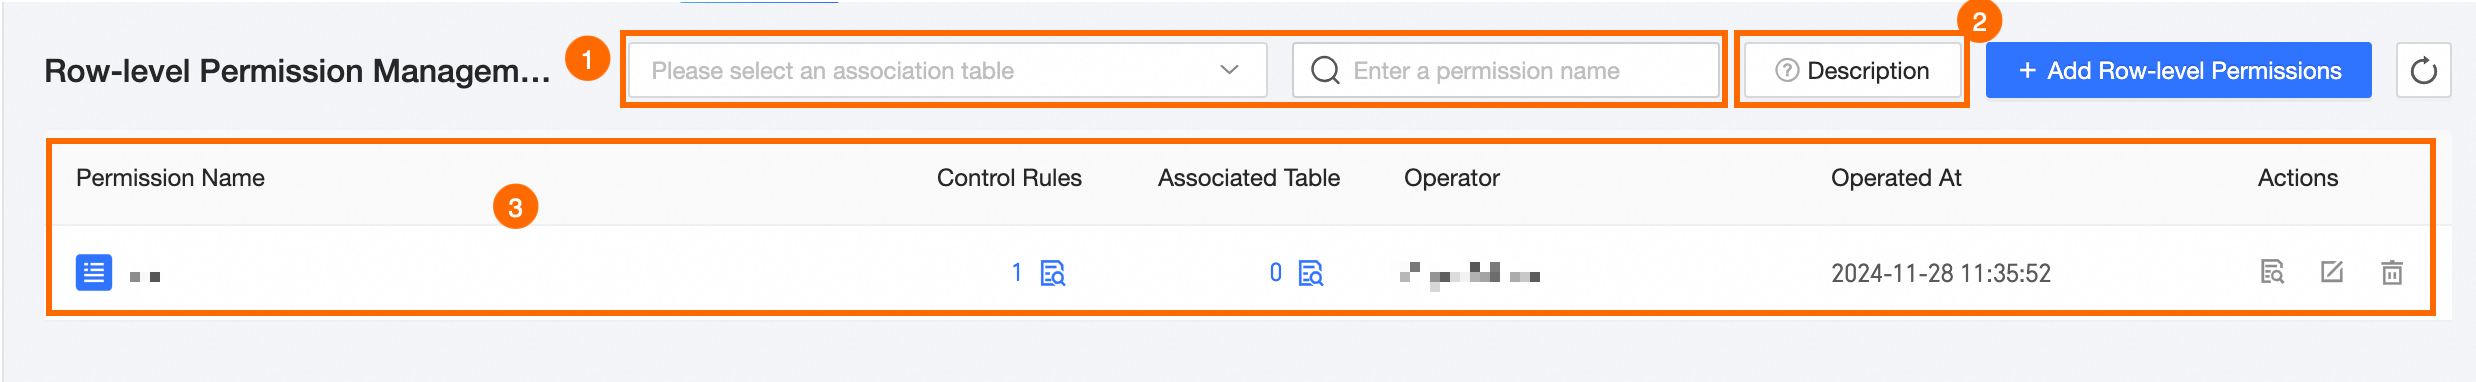
Area | Description |
①Filter and search | You can search for row-level permissions by name or filter by associated tables. |
②Description | View an introduction to how row-level permission works, including a diagram and SQL code.
|
③Row-level permission list | Displays the name, control rules, associated tables, operator, and operation time for each row-level permission. You can also view, edit, and delete permissions.
|
