同一个阿里云账号下往往同时存在多个 AgentSpace,分别对应不同团队或不同业务。如果直接授予 AgentLoop 的完整管理权限,成员可以看到并操作账号内所有 AgentSpace。本文提供可直接复制使用的 RAM 权限策略模板,把成员的权限收敛到单个 AgentSpace 及其关联资源上,在同一账号内实现多 AgentSpace 的权限隔离。
AgentSpace 关联的资源
AgentSpace 是 AgentLoop 中资源隔离与权限管理的最小单元。一个 AgentSpace 除了自身的 agentloop 资源,还会关联一组底层云资源:
日志服务(SLS):该 AgentSpace 关联的 SLS Project 与 SLS Trace Project,对应
log资源。微服务引擎(MSE):该 AgentSpace 关联的 MSE 命名空间,对应 RAM 的
airegistry资源前缀。云监控(CMS):该 AgentSpace 关联的 CMS Workspace,对应
cms资源。
因此,限制某个 AgentSpace 的权限,等价于用同一条策略把 agentloop、log、airegistry、cms 四类资源同时收敛到该 AgentSpace 关联的具体资源上。仅限制 agentloop 资源无法阻止成员访问其他 AgentSpace 的日志、监控数据和 Prompt/Skill 资产。
适用范围
本文所有模板都是 RAM 权限策略,需要在 RAM 控制台创建自定义权限策略后,再授予目标 RAM 用户或用户组。
策略模板选型
本文共提供四份策略模板,管控精度从单个 AgentSpace 隔离到全账号管理依次放宽。先按下表确定要使用的模板,再复制对应的策略文档:
策略模板 | 适用场景 | 资源范围 | 权限收敛程度 | 是否需叠加控制台首页最小权限策略 | 对应章节 |
完整版策略(推荐) | 需要把权限限定在单个 AgentSpace,并精确控制成员可执行的操作 | 目标 AgentSpace 及其关联的 SLS、MSE、CMS 资源 | Action 与 Resource 同时收敛,AgentLoop 新增操作时需同步维护 Action 列表 | 需要 | 完整版策略 |
简化版策略 | 只需要限定资源范围,不再细分操作 | 与完整版策略一致 | 仅收敛 Resource,成员在该资源范围内可执行各云产品的全部操作,后续维护成本更低 | 需要 | 简化版策略 |
控制台首页最小权限策略 | 成员需要从 AgentLoop 控制台首页进入 AgentSpace | 账号内全部 AgentSpace,仅开放 | 只放开首页列表操作,不含任何管理操作 | 本身即该策略 | 步骤三:叠加控制台首页最小权限 |
AgentLoopFullAccess | 成员需要管理账号内所有 AgentSpace 及其关联资源 | 不限定资源范围 | 不实现权限隔离,授予后可管理账号内全部 AgentSpace 及其关联资源 | 不需要, | 授予账号内全部 AgentSpace 的管理权限 |
完整版策略与简化版策略都只收敛资源范围,不包含控制台首页所需的 agentloop:ListAgentSpaces;成员如需从控制台首页进入 AgentSpace,还需叠加控制台首页最小权限策略。
将权限限定到某个 AgentSpace
一次可用的隔离授权由两条策略组成:一条把权限限定到目标 AgentSpace 的策略(完整版或简化版),一条放开控制台首页列表的最小权限策略。按以下三个步骤依次完成。
步骤一:收集需要限定的资源标识
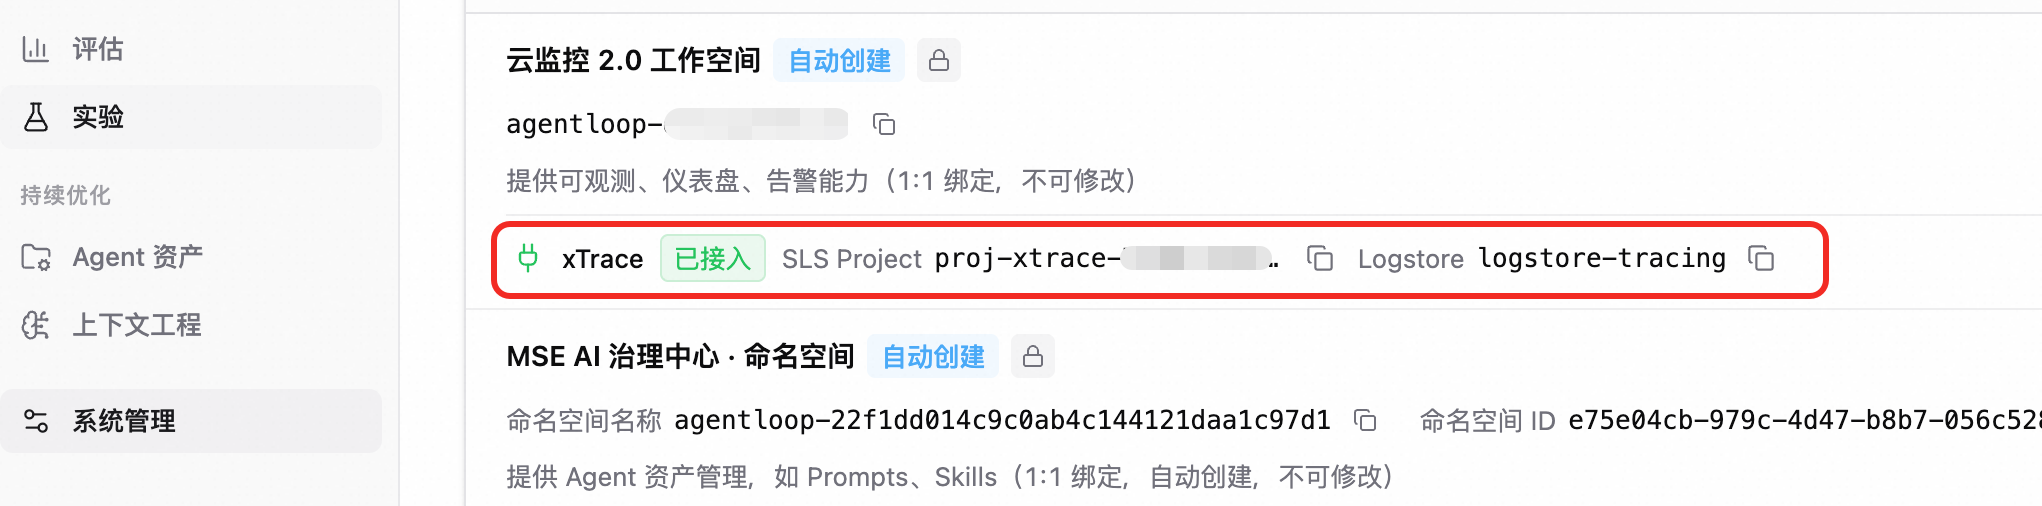
策略中的资源路径需要写入真实的资源标识,因此先在阿里云控制台逐个查到并记录下列取值: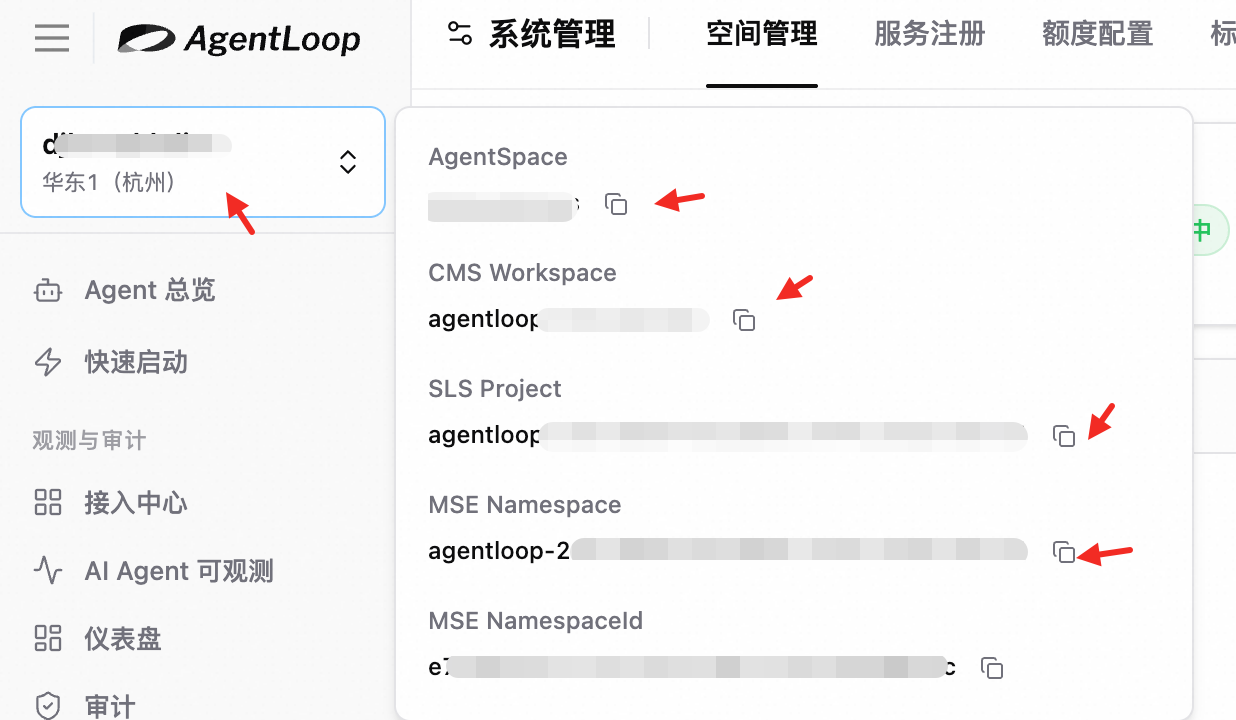
资源 | 取值类型 | 获取位置 | 对应占位符 |
AgentSpace | 名称 | AgentLoop 控制台的 AgentSpace 列表中打开目标 AgentSpace,查看其名称 |
|
SLS Project | 名称 | 日志服务控制台的 Project 列表中,找到该 AgentSpace 关联的 Project,查看其名称 |
|
SLS Trace Project | 名称 | 日志服务控制台的 Project 列表中,找到该 AgentSpace 用于存放链路数据的 Trace Project,查看其名称 |
|
MSE 命名空间 | Namespace ID | 微服务引擎控制台的命名空间列表中,找到该 AgentSpace 关联的命名空间,复制其 Namespace ID |
|
CMS Workspace | 名称 | 云监控 CMS 2.0 控制台的工作空间列表中,找到该 AgentSpace 关联的工作空间,查看其名称 |
|
airegistry 是 AI Registry(承载 Prompt、Skill 等资产)的 RAM 资源前缀。AgentLoop 侧的 AI Registry 资源以 MSE 命名空间承载,因此策略中 airegistry 的资源路径填写的是 MSE Namespace ID,形如 acs:airegistry:*:*:instance/saas/${MSENamespaceId}。
模板中的 ${AgentSpace}、${SLSProject}、${SLSTraceProject}、${MSENamespaceId}、${CMSWorkspace} 都是占位符,创建策略前必须按上表逐项替换为实际取值,否则策略不会生效于任何资源。
步骤二:创建并授予限定策略
按管控精度从完整版策略与简化版策略中选择一种模板,替换其中的占位符,然后在 RAM 控制台创建自定义权限策略,将替换后的内容粘贴为策略文档,再把策略授予目标 RAM 用户或用户组。
完整版策略
以下策略逐个列出每个云产品允许的 Action,并把 Resource 限定在步骤一收集的资源标识内。其 log、airegistry、cms 三段 Action 列表与 AgentLoopFullAccess 完全一致,差异仅在于 Resource 由 * 收敛为指定的资源路径:
{
    "Version": "1",
    "Statement": [
        {
            "Action": "agentloop:*",
            "Resource": [
                "acs:agentloop:*:*:agentspace/${AgentSpace}",
                "acs:agentloop:*:*:agentspace/${AgentSpace}/*"
            ],
            "Effect": "Allow"
        },
        {
            "Action": [
                "log:GetLogStoreLogs", "log:GetLogStoreHistogram", "log:GetIndex", "log:GetLogStore",
                "log:CreateIndex", "log:ListLogStores", "log:GetProject", "log:ListProject",
                "log:CreateLogStore", "log:UpdateIndex", "log:UpdateLogStore", "log:ListScheduledSQLs",
                "log:CreateScheduledSQL", "log:EnableScheduledSQL", "log:GetScheduledSQL",
                "log:UpdateScheduledSQL", "log:DisableScheduledSQL", "log:ListDashboard", "log:GetDashboard",
                "log:CreateDashboard", "log:UpdateDashboard", "log:DeleteDashboard", "log:ListTagResources",
                "log:TagResources", "log:UntagResources", "log:ListDashboardSharing",
                "log:CreateDashboardSharing", "log:AccessDashboardSharing", "log:UpdateDashboardSharing",
                "log:DeleteDashboardSharing"
            ],
            "Resource": [
                "acs:log:*:*:project/${SLSProject}",
                "acs:log:*:*:project/${SLSProject}/*",
                "acs:log:*:*:project/${SLSTraceProject}/logstore/*"
            ],
            "Effect": "Allow"
        },
        {
            "Action": [
                "airegistry:ListNamespaces", "airegistry:GetNamespace", "airegistry:GetPrompt",
                "airegistry:CreatePrompt", "airegistry:ListPrompts", "airegistry:UpdatePrompt",
                "airegistry:DeletePrompt", "airegistry:ListPromptVersions", "airegistry:GetPromptVersion",
                "airegistry:GetPromptVersionDetail", "airegistry:CreatePromptVersion",
                "airegistry:UpdatePromptVersion", "airegistry:SubmitPromptVersion",
                "airegistry:DeletePromptVersion", "airegistry:GetPromptGovernance",
                "airegistry:CreateSkillDraft", "airegistry:UpdateSkillDraft", "airegistry:DeleteSkillDraft",
                "airegistry:SubmitSkillVersion", "airegistry:PublishSkillVersion",
                "airegistry:ForcePublishSkillVersion", "airegistry:UpdateSkillBizTags",
                "airegistry:UpdateSkillLabels", "airegistry:OnlineSkill", "airegistry:OfflineSkill",
                "airegistry:UpdateSkillScope", "airegistry:GetSkillDetail",
                "airegistry:GetSkillVersionDetail", "airegistry:DownloadSkillVersion",
                "airegistry:ListSkills", "airegistry:DeleteSkill", "airegistry:UploadSkill",
                "airegistry:UploadSkillViaOss", "airegistry:DownloadSkillVersionViaOss"
            ],
            "Resource": [
                "acs:airegistry:*:*:instance/saas/${MSENamespaceId}",
                "acs:airegistry:*:*:instance/saas/${MSENamespaceId}/*"
            ],
            "Effect": "Allow"
        },
        {
            "Action": [
                "cms:ListWorkspaces", "cms:GetWorkspace", "cms:GetEntityStoreData", "cms:GetEntityStore",
                "cms:GetServiceObservability", "cms:DescribeIntranetRegions",
                "cms:DescribeVpcForIntranetSynthetic", "cms:DescribeVswitchForIntranetSynthetic",
                "cms:DescribeSecurityGroupForIntranetSynthetic", "cms:ListServices", "cms:CreateService",
                "cms:GetUmodelCommonSchemaRef", "cms:GetUmodel", "cms:UpsertUmodelCommonSchemaRef",
                "cms:UpsertUmodelData", "cms:ListAddons", "cms:GetAddon", "cms:GetAddonSchema",
                "cms:GetAddonCodeTemplate", "cms:GetAddonMetrics", "cms:GetAddonAlertTemplates",
                "cms:GetPrometheusUserSetting", "cms:GetCmsService", "cms:ListIntegrationPolicies",
                "cms:CreateIntegrationPolicy", "cms:CreateAddonRelease", "cms:GetAddonRelease",
                "cms:ListAddonReleases", "cms:ListIntegrationPolicyResources",
                "cms:ListIntegrationPolicyCollectors", "cms:ListPrometheusInstances",
                "cms:GetCloudResource", "cms:CreateCloudResource", "cms:GetCloudResourceData",
                "cms:ProxyApiForMemberAccount", "cms:CreateServiceObservability"
            ],
            "Resource": [
                "acs:cms:*:*:workspace/${CMSWorkspace}",
                "acs:cms:*:*:workspace/${CMSWorkspace}/*"
            ],
            "Effect": "Allow"
        },
        {
            "Action": "resourcecenter:GetResourceCenterServiceStatus",
            "Resource": "*",
            "Effect": "Allow"
        },
        {
            "Action": "ram:CreateServiceLinkedRole",
            "Resource": "*",
            "Effect": "Allow",
            "Condition": {
                "StringEquals": {
                    "ram:ServiceName": ["agentloop.aliyuncs.com"]
                }
            }
        },
        {
            "Action": "ram:PassRole",
            "Resource": "acs:ram::*:role/aliyunlogetlrole",
            "Effect": "Allow"
        }
    ]
}
简化版策略
如果不需要在 Action 层继续细分,可以在相同的资源限制下对每个云产品使用通配 Action。此时成员在限定的资源范围内可执行 agentloop、log、airegistry、cms 各产品的全部操作:
{
    "Version": "1",
    "Statement": [
        {
            "Action": "agentloop:*",
            "Resource": [
                "acs:agentloop:*:*:agentspace/${AgentSpace}",
                "acs:agentloop:*:*:agentspace/${AgentSpace}/*"
            ],
            "Effect": "Allow"
        },
        {
            "Action": "log:*",
            "Resource": [
                "acs:log:*:*:project/${SLSProject}",
                "acs:log:*:*:project/${SLSProject}/*",
                "acs:log:*:*:project/${SLSTraceProject}/logstore/*"
            ],
            "Effect": "Allow"
        },
        {
            "Action": "airegistry:*",
            "Resource": [
                "acs:airegistry:*:*:instance/saas/${MSENamespaceId}",
                "acs:airegistry:*:*:instance/saas/${MSENamespaceId}/*"
            ],
            "Effect": "Allow"
        },
        {
            "Action": "cms:*",
            "Resource": [
                "acs:cms:*:*:workspace/${CMSWorkspace}",
                "acs:cms:*:*:workspace/${CMSWorkspace}/*"
            ],
            "Effect": "Allow"
        },
        {
            "Action": "resourcecenter:GetResourceCenterServiceStatus",
            "Resource": "*",
            "Effect": "Allow"
        },
        {
            "Action": "ram:CreateServiceLinkedRole",
            "Resource": "*",
            "Effect": "Allow",
            "Condition": {
                "StringEquals": {
                    "ram:ServiceName": ["agentloop.aliyuncs.com"]
                }
            }
        },
        {
            "Action": "ram:PassRole",
            "Resource": "acs:ram::*:role/aliyunlogetlrole",
            "Effect": "Allow"
        }
    ]
}
步骤三:叠加控制台首页最小权限
AgentLoop 控制台首页通过 agentloop:ListAgentSpaces 拉取当前账号下的 AgentSpace 列表,成员如果没有该操作权限,首页无法展示任何 AgentSpace。步骤二的两种模板都不包含该操作,因此需要另建一条如下的自定义权限策略,与限定策略一并授予同一个 RAM 用户或用户组:
{
    "Version": "1",
    "Statement": [
        {
            "Action": "agentloop:ListAgentSpaces",
            "Resource": [
                "acs:agentloop:*:*:agentspace/*"
            ],
            "Effect": "Allow"
        }
    ]
}
该策略的资源路径为 acs:agentloop:*:*:agentspace/*,因此叠加后可见范围与可操作范围并不一致:成员在控制台首页可以列出账号内全部 AgentSpace,实际可操作的 AgentSpace 范围仍由步骤二的资源级授权收敛。
授予账号内全部 AgentSpace 的管理权限
AgentLoopFullAccess 模板不限定资源范围,不实现 AgentSpace 之间的权限隔离:授予后成员可管理账号内全部 AgentSpace 及其关联资源。仅当成员需要管理账号内所有 AgentSpace、以及 AgentLoop 依赖的日志、监控、Prompt/Skill 资源时使用该模板;需要权限隔离时请改用限定到单个 AgentSpace 的模板。策略除了 AgentLoop 自身的全部操作,还包含 AgentLoop 控制台读写 SLS、CMS、AI Registry 资源所需的操作,以及创建服务关联角色和向日志投递角色 aliyunlogetlrole 传递权限的授权。
在 RAM 控制台创建自定义权限策略,将以下内容粘贴为策略文档,再把策略授予目标 RAM 用户或用户组:
{
    "Version": "1",
    "Statement": [
        {
            "Action": "agentloop:*",
            "Resource": "*",
            "Effect": "Allow"
        },
        {
            "Action": [
                "log:GetLogStoreLogs", "log:GetLogStoreHistogram", "log:GetIndex", "log:GetLogStore",
                "log:CreateIndex", "log:ListLogStores", "log:GetProject", "log:ListProject",
                "log:CreateLogStore", "log:UpdateIndex", "log:UpdateLogStore", "log:ListScheduledSQLs",
                "log:CreateScheduledSQL", "log:EnableScheduledSQL", "log:GetScheduledSQL",
                "log:UpdateScheduledSQL", "log:DisableScheduledSQL", "log:ListDashboard", "log:GetDashboard",
                "log:CreateDashboard", "log:UpdateDashboard", "log:DeleteDashboard", "log:ListTagResources",
                "log:TagResources", "log:UntagResources", "log:ListDashboardSharing",
                "log:CreateDashboardSharing", "log:AccessDashboardSharing", "log:UpdateDashboardSharing",
                "log:DeleteDashboardSharing"
            ],
            "Resource": "*",
            "Effect": "Allow"
        },
        {
            "Action": [
                "airegistry:ListNamespaces", "airegistry:GetNamespace", "airegistry:GetPrompt",
                "airegistry:CreatePrompt", "airegistry:ListPrompts", "airegistry:UpdatePrompt",
                "airegistry:DeletePrompt", "airegistry:ListPromptVersions", "airegistry:GetPromptVersion",
                "airegistry:GetPromptVersionDetail", "airegistry:CreatePromptVersion",
                "airegistry:UpdatePromptVersion", "airegistry:SubmitPromptVersion",
                "airegistry:DeletePromptVersion", "airegistry:GetPromptGovernance",
                "airegistry:CreateSkillDraft", "airegistry:UpdateSkillDraft", "airegistry:DeleteSkillDraft",
                "airegistry:SubmitSkillVersion", "airegistry:PublishSkillVersion",
                "airegistry:ForcePublishSkillVersion", "airegistry:UpdateSkillBizTags",
                "airegistry:UpdateSkillLabels", "airegistry:OnlineSkill", "airegistry:OfflineSkill",
                "airegistry:UpdateSkillScope", "airegistry:GetSkillDetail",
                "airegistry:GetSkillVersionDetail", "airegistry:DownloadSkillVersion",
                "airegistry:ListSkills", "airegistry:DeleteSkill", "airegistry:UploadSkill",
                "airegistry:UploadSkillViaOss", "airegistry:DownloadSkillVersionViaOss"
            ],
            "Resource": "*",
            "Effect": "Allow"
        },
        {
            "Action": [
                "cms:ListWorkspaces", "cms:GetWorkspace", "cms:GetEntityStoreData", "cms:GetEntityStore",
                "cms:GetServiceObservability", "cms:DescribeIntranetRegions",
                "cms:DescribeVpcForIntranetSynthetic", "cms:DescribeVswitchForIntranetSynthetic",
                "cms:DescribeSecurityGroupForIntranetSynthetic", "cms:ListServices", "cms:CreateService",
                "cms:GetUmodelCommonSchemaRef", "cms:GetUmodel", "cms:UpsertUmodelCommonSchemaRef",
                "cms:UpsertUmodelData", "cms:ListAddons", "cms:GetAddon", "cms:GetAddonSchema",
                "cms:GetAddonCodeTemplate", "cms:GetAddonMetrics", "cms:GetAddonAlertTemplates",
                "cms:GetPrometheusUserSetting", "cms:GetCmsService", "cms:ListIntegrationPolicies",
                "cms:CreateIntegrationPolicy", "cms:CreateAddonRelease", "cms:GetAddonRelease",
                "cms:ListAddonReleases", "cms:ListIntegrationPolicyResources",
                "cms:ListIntegrationPolicyCollectors", "cms:ListPrometheusInstances",
                "cms:GetCloudResource", "cms:CreateCloudResource", "cms:GetCloudResourceData",
                "cms:ProxyApiForMemberAccount", "cms:CreateServiceObservability"
            ],
            "Resource": "*",
            "Effect": "Allow"
        },
        {
            "Action": "resourcecenter:GetResourceCenterServiceStatus",
            "Resource": "*",
            "Effect": "Allow"
        },
        {
            "Action": "ram:CreateServiceLinkedRole",
            "Resource": "*",
            "Effect": "Allow",
            "Condition": {
                "StringEquals": {
                    "ram:ServiceName": ["agentloop.aliyuncs.com"]
                }
            }
        },
        {
            "Action": "ram:PassRole",
            "Resource": "acs:ram::*:role/aliyunlogetlrole",
            "Effect": "Allow"
        }
    ]
}