This topic describes the precise access control feature, and how to enable and configure this feature.
Overview
The precise access control feature allows you to add custom match conditions to match user requests and perform specified actions on requests that matches the conditions. Match conditions support common HTTP fields such as IP, URL, and header. You can add different match conditions to meet the protection requirements in different scenarios.
ACL rules
An access control list (ACL) rule consists of one or more match conditions and one action. You can add one or more ACL rules. If you add multiple ACL rules, the rules are listed and matched against requests in descending order of priority. When a rule is matched, the system stops matching subsequent rules.
Enable precise access control
To enable the precise access control feature, visit the Contact Sales page, and leave your contact information. An Alibaba Cloud sales representative will contact you as soon as possible.
Procedure
-
Log on to the DCDN console.
-
In the left-side navigation pane, click Domain Names.
-
On the Domain Names page, find the domain name that you want to manage and click Configure in the Actions column.
- Click Security Settings and select the Precise Access Control tab.
- Add an ACL rule.
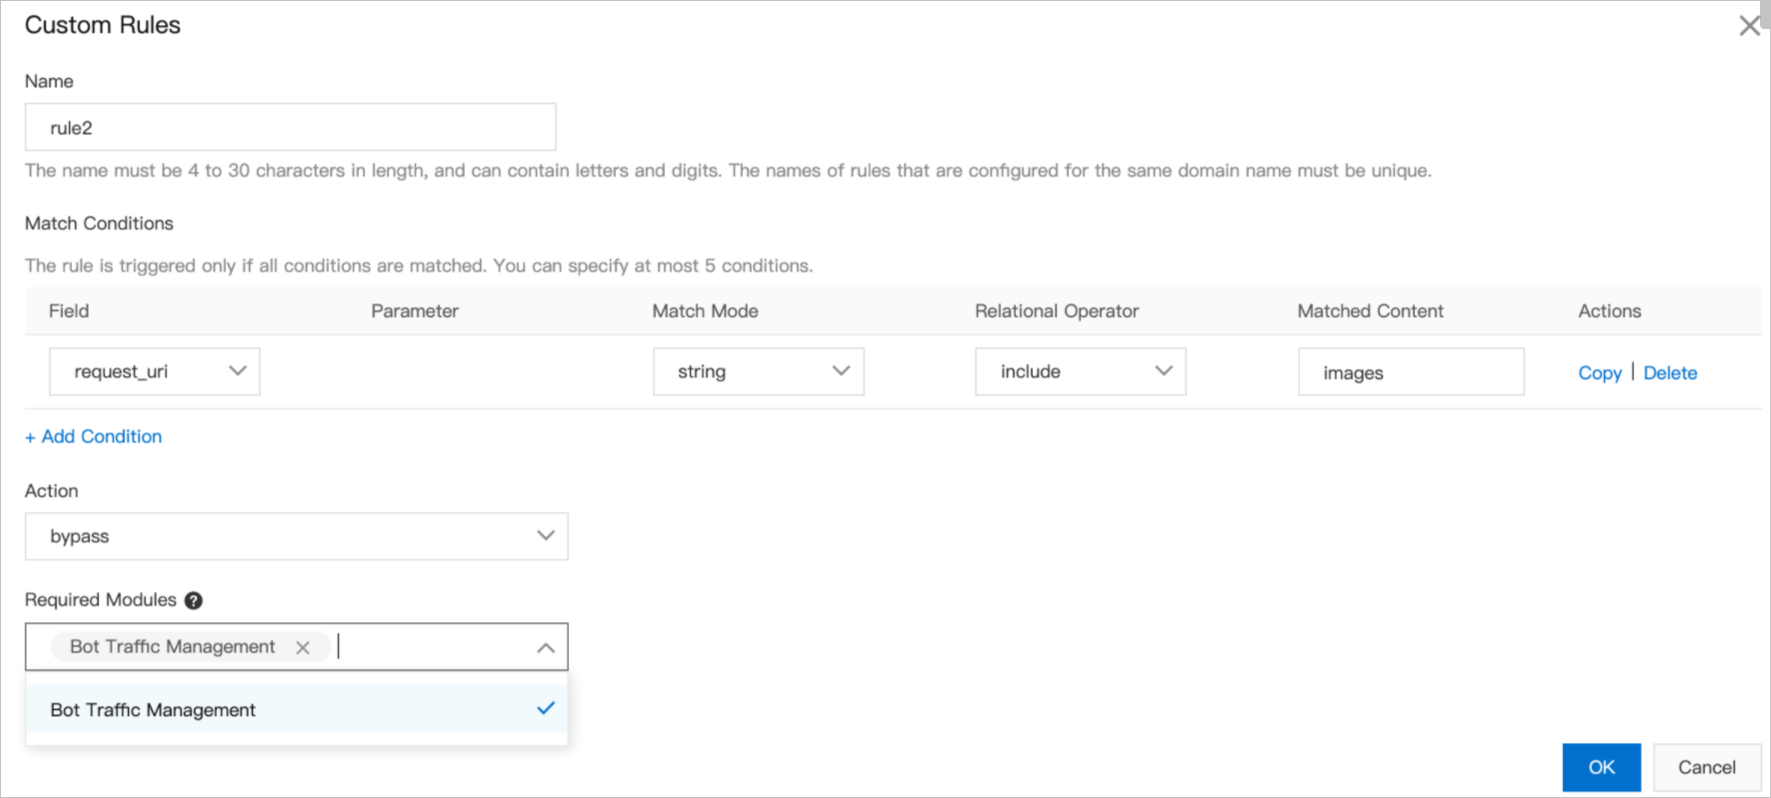
Match conditions
- Specifies the HTTP field of the request to match. Note
- You can add one or more match conditions. If you add multiple match conditions, the ACL rule is triggered only if all conditions are matched.
- A match condition consists of Field, Parameter, Match Mode, Relational Operator, and Match Content. When you configure a match condition, parameters that cannot be configured are not used in the match condition. You can ignore these parameters.
The following table describes the parameters of a match condition, such as Field and Relational Operator.
Field Parameter Match mode Relational operator Matched content requst_uri N/A RegEx match or NotMatch String string include, exclude, equal, or NotEqual String header Request header RegEx match or NotMatch String string include, exclude, equal, or NotEqual String string NotExist N/A method N/A string equal or NotEqual String ip N/A string in or NotIn IP addresses that are separated with commas (,). referer N/A RegEx match or NotMatch String string include, exclude, equal, or NotEqual String user-agent N/A RegEx match or NotMatch String string include, exclude, equal, or NotEqual String cookie N/A RegEx match or NotMatch String string include, exclude, equal, or NotEqual String content-type N/A RegEx match or NotMatch String string include, exclude, equal, or NotEqual String x-forwarded-for N/A RegEx match or NotMatch String string include, exclude, equal, or NotEqual String post-body N/A RegEx match or NotMatch String string include, exclude, equal, or NotEqual String params N/A RegEx match or NotMatch String string include, exclude, equal, or NotEqual String
- Specifies the HTTP field of the request to match.
Action
- The action that is performed when a request matches the conditions that you configure. Valid values:
- observe: Requests that match the configured conditions are allowed and recorded in the log. These requests carry a header when they are redirected to the origin server. This header defines the risk level of these requests and helps the origin server process these requests.
- block: Requests that match the configured conditions are rejected. A 403 status code is returned.
- bypass: Requests that match the configured conditions are allowed. You need to select a required module. The selected module will process requests that match the configured conditions. Modules that are not selected allow these requests.
- The action that is performed when a request matches the conditions that you configure. Valid values:
- After the ACL rule is configured, click OK.
- Optional: You can add multiple ACL rules and adjust the priority of the rules that you add.