Elastic Container Instance (ECI) provides software development kits (SDKs) for Go, Python, and Java. This topic uses the Java SDK as an example to show you how to create an ECI instance.
Install the Java SDK
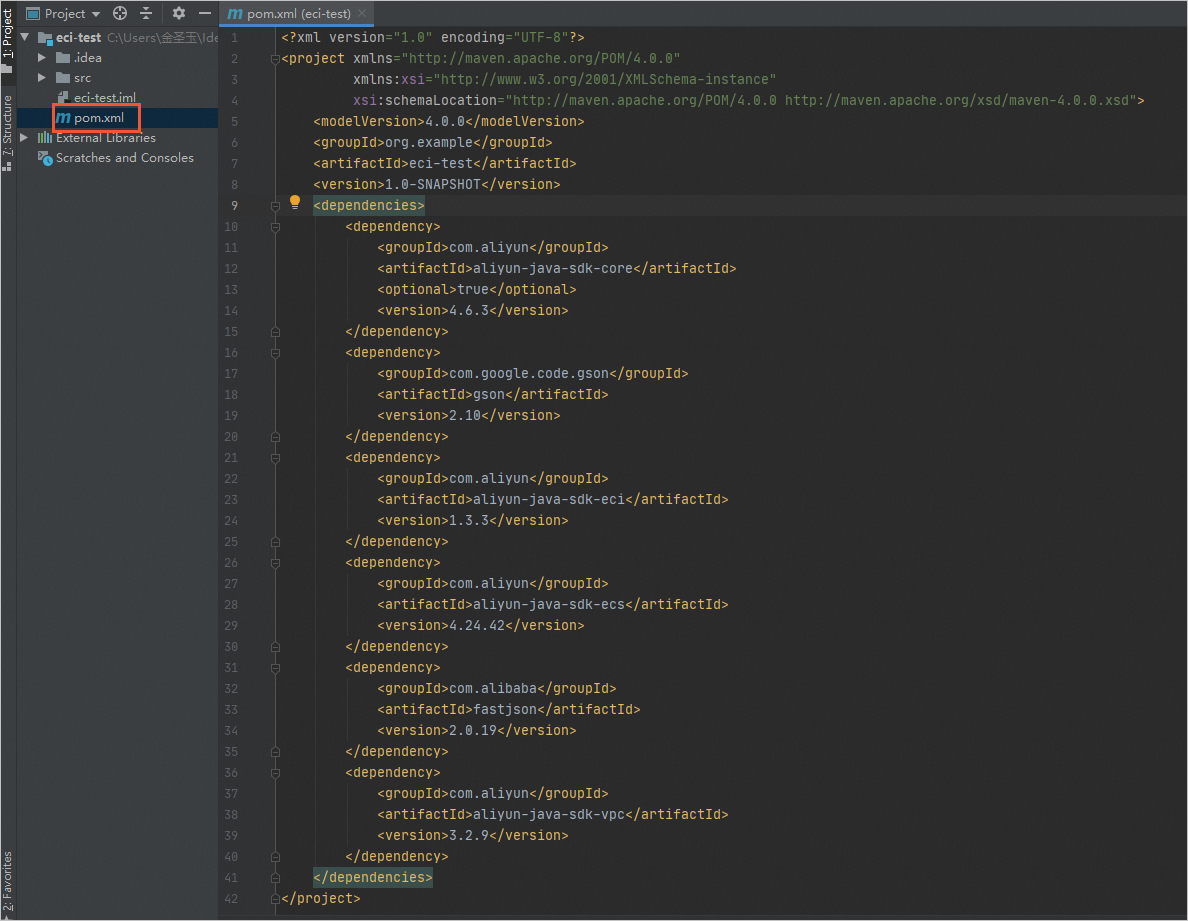
You can install the Java SDK using Apache Maven. Add the following dependencies to the pom.xml file of your Maven project:
If you already have a virtual private cloud (VPC), vSwitch, and security group, you do not need to create them using the SDK. In this case, you do not need to install the aliyun-java-sdk-vpc, aliyun-java-sdk-ecs, or fastjson dependencies.
The Alibaba Cloud core library: aliyun-java-sdk-core
Elastic Container Instance: aliyun-java-sdk-eci and the gson dependency
(Optional) Virtual Private Cloud: aliyun-java-sdk-vpc
(Optional) Elastic Compute Service: aliyun-java-sdk-ecs and the fastjson dependency
The following is an example:
Update the dependencies to their latest versions to use new features. For more information, see Maven.
<dependencies>
        <dependency>
            <groupId>com.aliyun</groupId>
            <artifactId>aliyun-java-sdk-core</artifactId>
            <optional>true</optional>
            <version>4.6.3</version>
        </dependency>
        <dependency>
            <groupId>com.google.code.gson</groupId>
            <artifactId>gson</artifactId>
            <version>2.10</version>
        </dependency>
        <dependency>
            <groupId>com.aliyun</groupId>
            <artifactId>aliyun-java-sdk-eci</artifactId>
            <version>1.3.3</version>
        </dependency>
          <dependency>
            <groupId>com.aliyun</groupId>
            <artifactId>aliyun-java-sdk-ecs</artifactId>
            <version>4.24.42</version>
        </dependency>
        <dependency>
            <groupId>com.alibaba</groupId>
            <artifactId>fastjson</artifactId>
            <version>2.0.19</version>
        </dependency>
        <dependency>
            <groupId>com.aliyun</groupId>
            <artifactId>aliyun-java-sdk-vpc</artifactId>
            <version>3.2.9</version>
        </dependency>
</dependencies>
The following procedure uses IntelliJ IDEA as an example:
Open IntelliJ IDEA and create a Maven project in one of the following ways.
Method 1: Create a Maven project in IntelliJ IDEA
In the menu bar, choose File > New > Project....
In the dialog box that appears, select Maven and complete the project configuration.
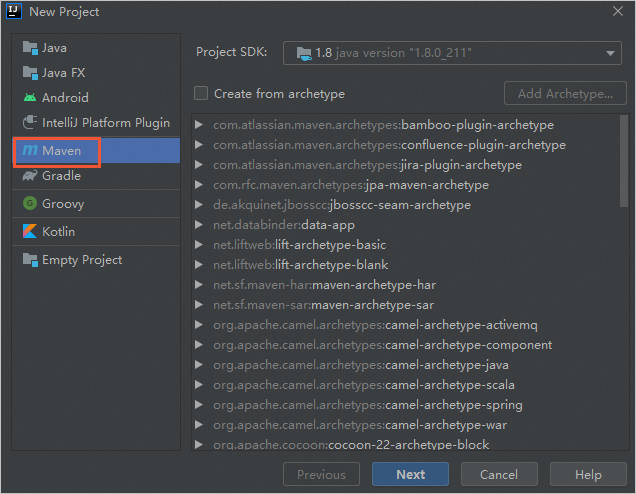
Method 2: Convert an existing project to a Maven project
Right-click the project that you want to convert and select Add Framework Support... from the pop-up menu.
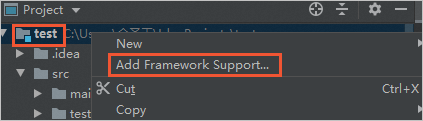
In the dialog box that appears, select Maven and then click OK.
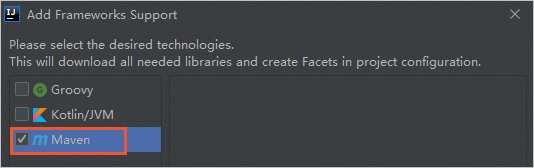
Open the pom.xml file in the Maven project folder and add the dependencies.
After you add the dependencies, Maven automatically downloads the required JAR packages.
Obtain AccessKey information
When you call Alibaba Cloud API operations, you must use an AccessKey for identity verification. To prevent security risks from a leaked AccessKey pair for your Alibaba Cloud account, create a Resource Access Management (RAM) user. Then, grant the RAM user permissions to access ECI and use the RAM user's AccessKey pair with the SDK.
The procedure is as follows:
For more information about creating a RAM user, see Create a RAM user.
For more information, see Grant permissions to a RAM user.
For more information about creating an AccessKey pair, see Create an AccessKey pair.
Create resources for an ECI instance
Before you create an ECI instance, you must create a VPC, a vSwitch, and a security group.
If you already have a VPC, a vSwitch, and a security group, you can retrieve their IDs and use them to create an ECI instance directly.
Create a VPC.
The following table describes the parameters that are used in the example. For more information, see CreateVpc.
Parameter
Example value
Description
RegionId
cn-shanghai
The region where the VPC resides.
Select a region that is supported by ECI. For more information, see Regions and Zones.
CidrBlock
192.168.0.0/16
The CIDR block of the VPC.
Use one of the following standard private CIDR blocks defined in RFCs or their subnets: 192.168.0.0/16, 172.16.0.0/12, or 10.0.0.0/8. The valid mask length is 8 to 28 bits.
The following code provides an example:
import com.aliyuncs.DefaultAcsClient;
import com.aliyuncs.IAcsClient;
import com.aliyuncs.exceptions.ClientException;
import com.aliyuncs.exceptions.ServerException;
import com.aliyuncs.profile.DefaultProfile;
import com.google.gson.Gson;
import com.aliyuncs.vpc.model.v20160428.*;

public class CreateVpc {

    public static void main(String[] args) {
        DefaultProfile profile = DefaultProfile.getProfile("cn-shanghai","<accessKeyId>", "<accessSecret>");
        IAcsClient client = new DefaultAcsClient(profile);

        CreateVpcRequest request = new CreateVpcRequest();
        request.setSysRegionId("cn-shanghai");
        request.setCidrBlock("192.168.0.0/16");

        try {
            CreateVpcResponse response = client.getAcsResponse(request);
            System.out.println(new Gson().toJson(response));
        } catch (ServerException e) {
            e.printStackTrace();
        } catch (ClientException e) {
            System.out.println("ErrCode:" + e.getErrCode());
            System.out.println("ErrMsg:" + e.getErrMsg());
            System.out.println("RequestId:" + e.getRequestId());
        }

    }
}
If the request is successful, the following response is returned:
{
	"vpcId": "vpc-uf6d60ru912b6jvco****",
	"vRouterId": "vrt-uf68fw505rxavz4hk****",
	"requestId": "2C7AA1E2-4407-5B41-89F2-3DADC5AEE18E",
	"routeTableId": "vtb-uf6orqxrmsyuv8gba****",
	"resourceGroupId": "rg-acfmzw2jz2z****"
}
Create a vSwitch in the VPC.
The following table describes the parameters that are used in the example. For more information, see CreateVSwitch.
Parameter
Example value
Description
VpcId
vpc-uf6d60ru912b6jvco****
The ID of the VPC to which the vSwitch belongs.
ZoneId
cn-shanghai-m
The ID of the zone to which the vSwitch belongs.
Please select a recommended zone in the selected region. For more information, see Regions and Zones.
CidrBlock
192.168.0.0/24
The CIDR block of the vSwitch. The CIDR block must meet the following requirements:
The mask length must be from 16 to 29 bits.
The CIDR block must be a subnet of the CIDR block of the VPC.
The CIDR block cannot be the same as the destination CIDR block of a route entry in the VPC, but it can be a subset of the destination CIDR block.
The following code provides an example:
import com.aliyuncs.DefaultAcsClient;
import com.aliyuncs.IAcsClient;
import com.aliyuncs.exceptions.ClientException;
import com.aliyuncs.exceptions.ServerException;
import com.aliyuncs.profile.DefaultProfile;
import com.google.gson.Gson;
import java.util.*;
import com.aliyuncs.vpc.model.v20160428.*;

public class CreateVSwitch {

    public static void main(String[] args) {
        DefaultProfile profile = DefaultProfile.getProfile("cn-shanghai", "<accessKeyId>", "<accessSecret>");
        IAcsClient client = new DefaultAcsClient(profile);

        CreateVSwitchRequest request = new CreateVSwitchRequest();
        request.setSysRegionId("cn-shanghai");
        request.setCidrBlock("192.168.0.0/24");
        request.setVpcId("vpc-uf6d60ru912b6jvco****");
        request.setZoneId("cn-shanghai-m");

        try {
            CreateVSwitchResponse response = client.getAcsResponse(request);
            System.out.println(new Gson().toJson(response));
        } catch (ServerException e) {
            e.printStackTrace();
        } catch (ClientException e) {
            System.out.println("ErrCode:" + e.getErrCode());
            System.out.println("ErrMsg:" + e.getErrMsg());
            System.out.println("RequestId:" + e.getRequestId());
        }

    }
}
If the request is successful, the following response is returned:
{
	"vSwitchId": "vsw-uf6uma67wlgxwuyb5****",
	"requestId": "B94FAE14-043C-56B5-A763-F2E03C75AC3F"
}
Create a security group.
When you create a security group, you must specify a VPC. The following code provides an example:
import com.aliyuncs.DefaultAcsClient;
import com.aliyuncs.IAcsClient;
import com.aliyuncs.exceptions.ClientException;
import com.aliyuncs.exceptions.ServerException;
import com.aliyuncs.profile.DefaultProfile;
import com.google.gson.Gson;
import java.util.*;
import com.aliyuncs.ecs.model.v20140526.*;

public class CreateSecurityGroup {

    public static void main(String[] args) {
        DefaultProfile profile = DefaultProfile.getProfile("cn-shanghai", "<accessKeyId>", "<accessSecret>");
        IAcsClient client = new DefaultAcsClient(profile);

        CreateSecurityGroupRequest request = new CreateSecurityGroupRequest();
        request.setSysRegionId("cn-shanghai");
        request.setVpcId("vpc-uf6d60ru912b6jvco****");

        try {
            CreateSecurityGroupResponse response = client.getAcsResponse(request);
            System.out.println(new Gson().toJson(response));
        } catch (ServerException e) {
            e.printStackTrace();
        } catch (ClientException e) {
            System.out.println("ErrCode:" + e.getErrCode());
            System.out.println("ErrMsg:" + e.getErrMsg());
            System.out.println("RequestId:" + e.getRequestId());
        }

    }
}
If the request is successful, the following response is returned:
{
	"securityGroupId": "sg-uf63jawzncdab6xb****",
	"requestId": "73D5964C-686A-59AF-8433-209067AB51D7"
}
Create an ECI instance
This example specifies the following parameters. For more information, see CreateContainerGroup.
Parameter | Example value | Description |
RegionId | cn-shanghai | The region where the ECI instance resides. |
SecurityGroupId | sg-uf63jawzncdab6xb**** | The security group to which the ECI instance belongs. |
VSwitchId | vsw-uf6uma67wlgxwuyb5**** | The vSwitch to which the ECI instance belongs. |
ContainerGroupName | test | The name of the ECI instance. |
Container.N.Image | registry-vpc.cn-shanghai.aliyuncs.com/eci_open/nginx:1.14.2 | The container image. |
Container.N.Name | nginx | The name of the container. |
The following code provides an example:
import com.aliyuncs.DefaultAcsClient;
import com.aliyuncs.IAcsClient;
import com.aliyuncs.exceptions.ClientException;
import com.aliyuncs.exceptions.ServerException;
import com.aliyuncs.profile.DefaultProfile;
import com.google.gson.Gson;
import java.util.*;
import com.aliyuncs.eci.model.v20180808.*;
public class CreateContainerGroup {
    public static void main(String[] args) {
        DefaultProfile profile = DefaultProfile.getProfile("cn-shanghai", "<accessKeyId>", "<accessSecret>");
        IAcsClient client = new DefaultAcsClient(profile);
        CreateContainerGroupRequest request = new CreateContainerGroupRequest();
        request.setRegionId("cn-shanghai");
        request.setSecurityGroupId("sg-uf63jawzncdab6xb****");
        request.setVSwitchId("vsw-uf6uma67wlgxwuyb5****");
        request.setContainerGroupName("test");
        List<CreateContainerGroupRequest.Container> containerList = new ArrayList<CreateContainerGroupRequest.Container>();
        CreateContainerGroupRequest.Container container1 = new CreateContainerGroupRequest.Container();
        container1.setImage("registry-vpc.cn-shanghai.aliyuncs.com/eci_open/nginx:1.14.2");
        container1.setName("nginx");
        containerList.add(container1);
        request.setContainers(containerList);
        try {
            CreateContainerGroupResponse response = client.getAcsResponse(request);
            System.out.println(new Gson().toJson(response));
        } catch (ServerException e) {
            e.printStackTrace();
        } catch (ClientException e) {
            System.out.println("ErrCode:" + e.getErrCode());
            System.out.println("ErrMsg:" + e.getErrMsg());
            System.out.println("RequestId:" + e.getRequestId());
        }
    }
}
If the request is successful, the following response is returned. The value of containerGroupId is the ID of the created ECI instance.
{
	"requestId": "FA8DB391-3F54-5998-BDA0-8195113108E8",
	"containerGroupId": "eci-uf6g69s8wou20ns7****"
}