A Variable Replacement filter lets you switch between query intervals, such as 10, 60, or 600 seconds, without modifying your query statement each time. This example uses NGINX access logs.
Prerequisites
-
You have collected NGINX access logs. For more information, see Collect text logs from servers.
-
You have created indexes. For more information, see Create indexes.
Procedure
The following workflow shows how to add a Variable Replacement filter for NGINX access logs.

Simple Log Service also supports other filter types. For more information, see Filter types.
Step 1: Query and analyze data
Query the per-minute page view (PV) count:
Log on to the Simple Log Service console.
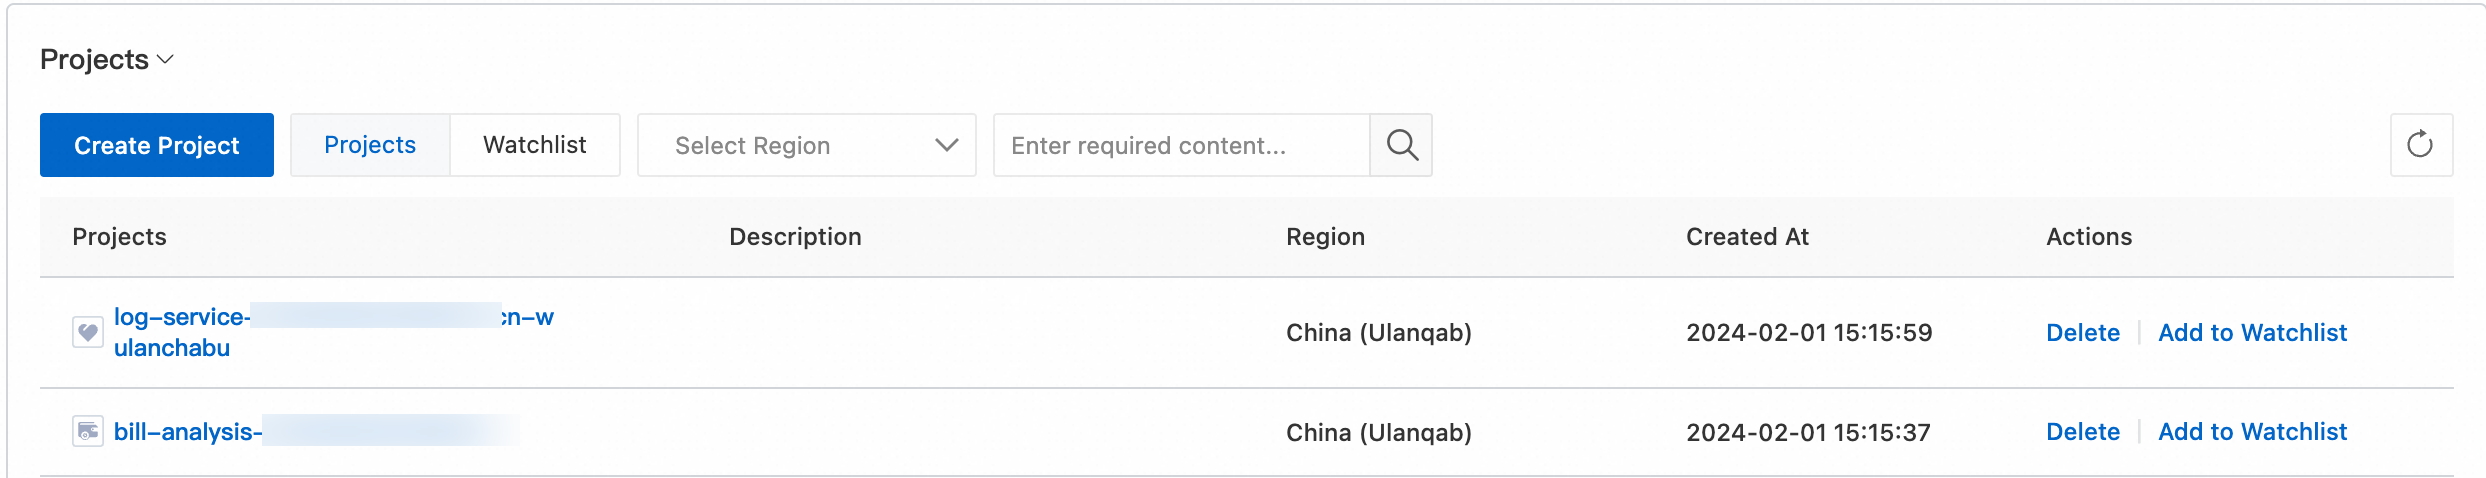
In the Projects section, click the one you want.
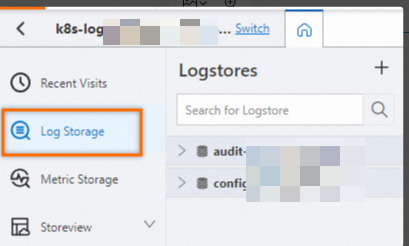
On the tab, click the logstore you want.
-
Enter a query statement, and then click Last 15 Minutes to set the time range.
For example, to view the number of PVs per minute, use the following query statement:
* | SELECT date_format(__time__ - __time__ % 60, '%H:%i:%s') as time, count(1) as count GROUP BY time ORDER BY timeA chart displays the number of PVs per minute.
Step 2: Add the chart to a dashboard
Add the per-minute PV chart to the NGINX Access Log dashboard:
-
On the Graph tab, click Add to New Dashboard.
-
In the Add to New Dashboard dialog box, configure the parameters and click Confirm.
Key parameters include Operation Type (for example, select Create New Dashboard), Layout Mode (for example, select Grid Layout), and Dashboard Name (for example, enter
NGINX Access Log).For more information about dashboard parameters, see Add a chart to a dashboard.
Step 3: Define a variable
Define the query time interval as a variable:
-
In the navigation pane on the left, choose .
-
In the Dashboard list, click NGINX Access Logs.
-
In the upper-right corner of the NGINX Access Logs page, click Edit. Find the chart to modify, and choose
 > Edit.
-
In the query statement, change 60 to ${{interval|60}}, click Apply, and then click OK.
In this expression,
intervalis the variable name and 60 is its default value. You set the actual value when you add a filter. If you use ${{interval}} without a default value, the query fails.-
Query statement before the change:
* | SELECT date_format(__time__ - __time__ % 60, '%H:%i:%s') as time, count(1) as count GROUP BY time ORDER BY time -
Query statement after the change:
* | SELECT date_format(__time__ - __time__ % ${{interval|60}}, '%H:%i:%s') as time, count(1) as count GROUP BY time ORDER BY time
For more information about variables, see Use variables to dynamically adjust query parameters.
-
Step 4: Add the filter
Add a filter based on the variable you defined:
-
In the upper-right corner of the NGINX Access Logs dashboard, click the
 icon.
-
In the Filter panel, configure the following settings and then click OK.
Note-
Set Type to Variable Replacement.
-
For Key Value, you must enter the variable that you defined in Step 3. In this example, the value is interval.
-
Use Static List Items to configure different values for the query interval.
Set the filter name to PV Filter. For the display component type, select drop-down list. In the Static List Items field, add three values:
10(alias: 10 seconds),60(alias: 60 seconds), and600(alias: 600 seconds). For more information, see Add a filter to a dashboard. -
-
Adjust the page layout and click Save.
-
In the Save Dashboard dialog box, click Confirm.
The time interval filter appears on the NGINX Access Log dashboard.
The PV Filter panel contains an interval input box and a Query button. The query results appear in a table with time and count columns showing the per-minute PV count. Use the pagination controls at the bottom of the table to browse the data.
Step 5: Verify the results
-
On the NGINX Access Logs dashboard, in the PV Filter section, select 10 from the interval drop-down list to query the number of PVs every 10 seconds.
The corresponding query statement is as follows:
* | SELECT date_format(__time__ - __time__ % 10, '%H:%i:%s') as time, count(1) as count GROUP BY time ORDER BY timeThe NGINX Access Log dashboard displays the number of PVs per 10 seconds.
-
On the NGINX Access Logs dashboard, in the PV Filter section, select 60 from the interval drop-down list to query the number of PVs every 60 seconds.
The corresponding query statement is as follows:
* | SELECT date_format(__time__ - __time__ % 60, '%H:%i:%s') as time, count(1) as count GROUP BY time ORDER BY timeThe NGINX Access Log dashboard displays the number of PVs per 60 seconds.