You can access Hologres by assuming a RAM role through role-based single sign-on (SSO).
Background information
Alibaba Cloud enterprise users typically log on to the console with a username and password. As security requirements become stricter, many enterprises prefer role-based SSO to centralize authentication. For more information, see Overview of SAML-based role SSO.
Scenarios
To meet stricter security regulations and centralize authentication, enterprises often adopt SSO, which allows users to log on once and access all trusted applications. Hologres supports role-based SSO. For more information, see Overview of SAML-based role SSO. With this feature, you can use your enterprise account to assume a RAM role and access a Hologres instance. The access permissions are controlled by the RAM role. 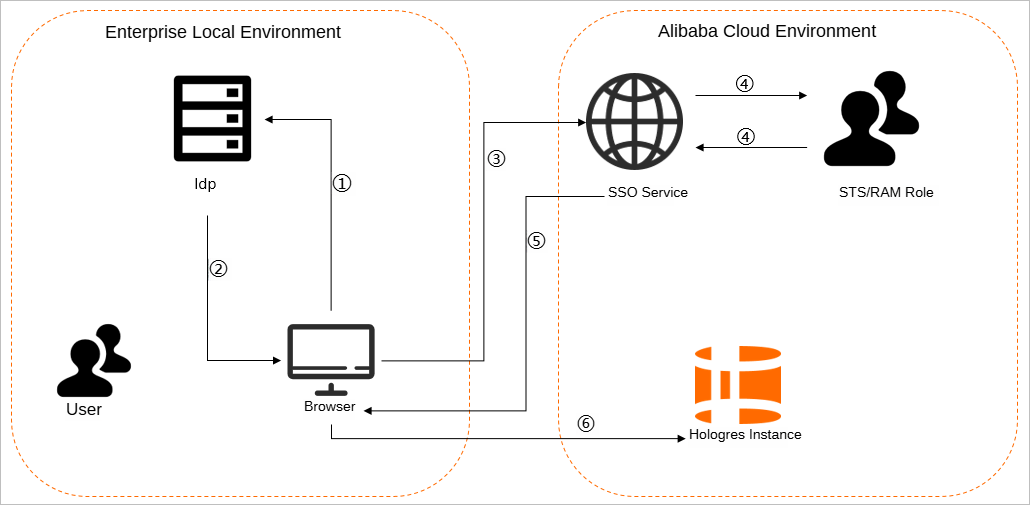
-
The user opens a browser and selects Alibaba Cloud as the target service on the identity provider's (IdP) logon page.
For example, if your enterprise IdP is Microsoft Active Directory Federation Services (AD FS), the logon URL is AD FS sign-on page, where
<adfsservicename>is your AD FS service name.NoteSome IdPs require users to log on before they can select the SSO application that represents Alibaba Cloud.
-
The IdP generates a SAML response and returns it to the browser.
-
The browser redirects to the SSO service page and forwards the SAML response to the SSO service.
-
The SSO service uses the SAML response to request temporary security credentials from the Alibaba Cloud Security Token Service (STS) and generates a logon URL for the Alibaba Cloud Management Console.
NoteIf the SAML response contains attributes that map to multiple RAM roles, the user is prompted to select a role to access Alibaba Cloud.
-
The SSO service returns the URL to the browser.
-
The browser redirects to the URL, logging the user on to the Alibaba Cloud Management Console as the specified RAM role. The user then accesses the Hologres instance by assuming this role.
Supported access methods in Hologres
Hologres supports the following two access methods:
-
Access Hologres by using a cloud account (an Alibaba Cloud account or a RAM user).
You can log on to the Alibaba Cloud Management Console by entering a username and password, and then use Hologres as the current account. In this case, the Alibaba Cloud account becomes a member of a Hologres instance with permissions to use the service.
-
Log on to Hologres by using role-based SSO.
You can also log on to Alibaba Cloud by using role-based SSO (Overview of SAML-based role SSO) and use Hologres. In this case, the RAM role becomes a member of a Hologres instance. Users who assume this RAM role have the same permissions as members who use Alibaba Cloud accounts. For more information about RAM roles, see RAM role overview.
In Hologres, a RAM role is equivalent to an Alibaba Cloud account (either a root account or a RAM user). Therefore, a RAM role is considered a standard logon account. A superuser must grant permissions, such as SELECT, INSERT, or UPDATE, directly to the RAM role, not to the underlying Alibaba Cloud account. The RAM role can then use Hologres within the scope of its granted permissions.
Role-based SSO (STS)
Role-based SSO for Hologres uses the Alibaba Cloud Security Token Service (STS). STS issues temporary security credentials with custom validity periods and permissions to users managed by your on-premises identity system. Users can use these credentials to directly connect to Hologres and access authorized resources.
STS tokens provide the following benefits:
-
Reduces the risk of exposing your AccessKey pair. You only need to generate temporary credentials for users.
-
Enables flexible permission control. STS tokens automatically expire after a limited validity period, eliminating the need to manually revoke permissions.
Follow these steps to create a RAM role and grant it permissions to access Hologres.
Step 1: Create a RAM role
Log on to the Resource Access Management (RAM) console to create a RAM role. For the principal type, select either Alibaba Cloud Account or Identity Provider.
-
If you need to switch identities on the Alibaba Cloud Management Console to assume the role, create a role with the Alibaba Cloud Account principal type. For more information, see Assume a role as a RAM user and grant permissions.
-
If you need to log on to Alibaba Cloud by using an on-premises IdP account to assume the role, create a role with the Identity Provider principal type. For more information, see Assume a role as an IdP user and grant permissions.
Assume a role as a RAM user
If you need a RAM user to assume a RAM role by switching identities on the Alibaba Cloud Management Console, log on to the Resource Access Management (RAM) console and create a RAM role. For the principal type, select Alibaba Cloud Account.
-
Create a RAM role whose principal type is Alibaba Cloud Account.
-
Log on to the Resource Access Management (RAM) console. In the left-side navigation pane, choose Identities > Roles.
-
On the Create Role page, click Create Role. For Principal Type, select Alibaba Cloud Account. For Principal Name, select Current Account. Click OK.
-
In the Create Role dialog box, enter a Role Name and click OK to create the role.
-
-
Create and attach a permission policy.
-
On the RAM role management page, click the name of the target role to go to its details page.
-
Click the Trust Policy tab. Click Edit Trust Policy and replace the policy with the following script.
-
Parameter description
When you configure the policy, in the string
acs:ram::root_account_ID:root, replaceroot_account_IDwith the ID of the account that you want to authorize. Go to the User Information page to obtain the account ID. -
Policy example
{
    "Statement": [
        {
            "Action": "sts:AssumeRole",
            "Effect": "Allow",
            "Principal": {
                "RAM": [
                    "acs:ram::
-
-
Click OK to save the trust policy.
-
-
Create a RAM user and grant it permissions to assume a role.
To assume a RAM role as a RAM user, you must create a RAM user and grant it permission to assume roles.
-
Log on to the Resource Access Management (RAM) console. In the left-side navigation pane, choose .
-
(Optional) If you already have a RAM user, skip this step. Click Create User to create one or more RAM users. For more information, see Create a RAM user.
-
Click Add Permissions in the Actions column of the target RAM user.
-
On the Add Permissions page, grant the
AliyunSTSAssumeRoleAccesspermission to the RAM user to allow the user to call theAssumeRoleoperation of the STS API. In the permissions section, click the System Policy tab, then search for and select the AliyunSTSAssumeRoleAccess policy. -
Click OK to finish the setup.
-
Assume a role as an IdP user
If you need to log on to Alibaba Cloud by using an on-premises IdP account to assume a RAM role, log on to the Resource Access Management (RAM) console and create a RAM role. For the principal type, select Identity Provider.
-
Create a RAM role whose principal type is Identity Provider.
-
Log on to the Resource Access Management (RAM) console. In the left-side navigation pane, choose Identities > Role.
-
On the Role page, click Create Role. For Principal Type, select Identity Provider.
-
Click OK. Configure the Role Name and Note parameters.
-
Select an IdP Type and an Select IdP. Review the conditions and click Complete. A message appears, indicating that the role is created.
-
-
Create and attach a permission policy.
-
On the role list page, click the name of the target role to go to its details page.
-
Click the Trust Policy tab. Click Edit Trust Policy and replace the policy with the following script.
-
Parameter description
When you configure a policy, you must replace
RootAccountIDin the scriptacs:ram::RootAccountID:saml-provider/IDPwith the information for the account that you want to authorize. Go to the User Information page to obtain the account ID. -
Policy example
{
    "Statement": [
        {
            "Action": "sts:AssumeRole",
            "Condition": {
                "StringEquals": {
                    "saml:recipient": "https://signin.alibabacloud.com/saml-role/sso"
                }
            },
            "Effect": "Allow",
            "Principal": {
                "Federated": [
                    "acs:ram::
-
-
Click OK to save the trust policy.
-
Step 2: Add and authorize the RAM role
A RAM role must have development permissions on a Hologres instance before it can use Hologres. By default, a RAM role cannot view or manage instances on the Hologres console, so the root account must first grant the required permissions in RAM. For more information, see Grant permissions to a RAM user. You can add the RAM role to a Hologres instance and grant permissions by using one of the following methods.
-
Log on to the Hologres console to grant permissions.
-
In the left-side navigation pane, go to the Instances page. Click the instance to which you want to grant permissions. On the User Management tab, find the RAM role and add it as a new user to the instance.
-
On the Database Authorization tab, grant the required instance development permissions to the RAM role.
-
-
Grant permissions using SQL statements.
You can grant permissions by using SQL statements. For more information, see Permission management overview.
-
When a RAM user assumes a RAM role, the role does not have permissions to access the Hologres console by default. The root account must grant the AliyunRAMReadOnlyAccess permission to the RAM user on the RAM console. Otherwise, the role cannot perform any operations on the Hologres console. For more information, see Grant permissions to a RAM user.
Step 3: Log on and use Hologres
Console and HoloWeb logon
After granting the permissions, users can assume the RAM role to log on to and use Hologres.
-
Assume the RAM role to log on to the Hologres console and manage your Hologres instances.
-
On the Hologres console page, click Go to HoloWeb in the left-side navigation pane to open the HoloWeb page. You can then design schemas and develop data. For more information, see Connect to HoloWeb and run a query.
JDBC and psql client logon
Hologres V2.0 and later allow you to specify a security token in the PostgreSQL protocol connection options to access Hologres as a RAM role from a PostgreSQL client, such as JDBC or psql.
Before you connect, ensure the following prerequisites are met:
-
You have added the RAM role to the Hologres instance and granted permissions. For more information, see Step 2: Add the RAM role to a Hologres instance and grant permissions.
-
You have called the AssumeRole - Get temporary security credentials for assuming a role API operation in Resource Access Management (RAM) to obtain the STS token triplet: an AccessKey ID, an AccessKey Secret, and a security token. For more information, see STS SDK call examples. The following code shows a sample STS token:
"Credentials": {
    "SecurityToken": "CAISuwJ1q6Ft5B2yu****KiAA",
    "AccessKeyId": "STS.NTKaenSkmLhG4HpM5****76UV",
    "AccessKeySecret": "6itECZnhbG2RU6ktTSBSd6JxeLHKPWyBt****SS62",
    "Expiration": "2025-02-21T03:47:07Z"
  }
After completing these prerequisites, connect to Hologres in one of the following ways.
-
Connect by using JDBC (Java): For more information, see Connect to Hologres by using JDBC.
-
Example 1: Load the STS token triplet using the properties of the PGProperty class from the PostgreSQL JDBC driver to complete identity verification.
import org.postgresql.PGProperty; import java.sql.*; import java.io.IOException; import java.util.Properties; public class JdbcLinkHologres1 { public static void main(String[] args) throws IOException, ClassNotFoundException, SQLException { // This example shows how to store the AccessKey ID and AccessKey Secret in environment variables. You can also store them in a configuration file based on your business needs. // To prevent key leakage, do not hard-code the AccessKey ID and AccessKey Secret in your code. String accessKeyId = "ALIBABA_CLOUD_ACCESS_KEY_ID"; String accessKeySecret = "ALIBABA_CLOUD_ACCESS_KEY_SECRET"; String securityToken = "<SecurityToken>"; String url = "jdbc:postgresql://<host>:<port>/<database>"; Properties props = new Properties(); PGProperty.USER.set(props, accessKeyId); PGProperty.PASSWORD.set(props, accessKeySecret); PGProperty.OPTIONS.set(props, "sts_token=" + securityToken); Class.forName("org.postgresql.Driver"); Connection connection = DriverManager.getConnection(url, props); Statement statement = connection.createStatement(); ResultSet resultSet = statement.executeQuery("SELECT * FROM tabletest"); // Process the resultSet while (resultSet.next()) { System.out.println("Result: " + resultSet.getInt(1)); System.out.println("Result: " + resultSet.getString(2)); } } } -
Example 2: URL-encode the security token, append it to the JDBC URL, and then load the AccessKey ID and AccessKey Secret when the driver class establishes the Hologres connection to complete identity verification.
import java.net.URLEncoder;
import java.sql.*;
import java.io.IOException;
public class JdbcLinkHologres2 {
    public static void main(String[] args) throws IOException, ClassNotFoundException, SQLException {
        // This example shows how to store the AccessKey ID and AccessKey Secret in environment variables. You can also store them in a configuration file based on your business needs.
	// To prevent key leakage, do not hard-code the AccessKey ID and AccessKey Secret in your code.
        String accessKeyId = "ALIBABA_CLOUD_ACCESS_KEY_ID";
        String accessKeySecret = "ALIBABA_CLOUD_ACCESS_KEY_SECRET";
        String securityToken = "<SecurityToken>";
        String url = "jdbc:postgresql://<host>:<port>/<database>";
        String urlWithOptions = url + "?options=sts_token=" + URLEncoder.encode(securityToken, "UTF-8");
        Class.forName("org.postgresql.Driver");
        Connection connection = DriverManager.getConnection(urlWithOptions, accessKeyId, accessKeySecret);
        Statement statement = connection.createStatement();
        ResultSet resultSet = statement.executeQuery("SELECT * FROM tabletest");
        // Process the resultSet
        while (resultSet.next()) {
            System.out.println("Result: " + resultSet.getInt(1));
            System.out.println("Result: " +  resultSet.getString(2));
        }
    }
}
-
-
Connect using a psql client: The following command is for Linux systems. For more information, see Connect to Hologres by using a psql client.
PGUSER=<AccessKeyId> PGPASSWORD=<AccessKeySecret> PGOPTIONS="sts_token=<SecurityToken>" psql -h <host> -p <port> -d <database>
FAQ
What should I do if I receive the error password authentication failed for user "<AccessKeyId>" when logging on as a RAM role?
This error indicates that the AccessKey ID, AccessKey Secret, or security token is incorrect, or the user does not exist in the Hologres instance. Check the following:
-
Check whether the user exists in the instance. If not, add the RAM role to the instance. For more information, see Step 2: Add the RAM role to a Hologres instance and grant permissions.
-
Check whether the security token is passed correctly. If you pass it in the URL, you must encode it using
URLEncoder.encode. -
Check whether the AccessKey ID, AccessKey Secret, and security token are correct.