After you add members to Dataphin, you can delete, disable, and transfer ownership from them. This topic describes how to manage Dataphin members.
Permissions
Super administrators and system administrators can disable members, delete members, transfer ownership, and configure the contact information for all members.
System administrators cannot disable or delete super administrators. They also cannot transfer ownership from super administrators or other system administrators.
Manage Dataphin members
On the Dataphin home page, in the top navigation bar, select Admin > Member management. The Member management page opens by default.
(Optional) On the member management page, find a specific member. You can search by the user's name or ID, or filter by Abnormal Account, user role, and member status.
Abnormal Account: At 00:00 every day, the system automatically refreshes, identifies accounts that have been deleted from the source system, and marks them with the
 tag.
On the member management page, you can perform operations such as editing, disabling, enabling, and transferring ownership for members. The following table describes the available operations.
Actions
Description
Batch update DingTalk UserIDs
Only users with the member management - manage tenant members permission can perform this action. For more information, see Batch update DingTalk UserIDs.
NoteThis feature is available only after you enable DingTalk OA approval.
Edit
You can modify a user's user role and contact information (such as email, mobile phone, and DingTalk group chatbot). Members can receive monitoring alerts only if their contact information is configured. For more information, see Edit member account information.
Edit a single member:
Click the
 icon in the Actions column of the target member.
In the Edit Account dialog box, modify the user role and contact information, and then click OK.
Edit members in batches:
In the member list, select multiple members or select Select all on this page at the bottom of the page, and then click Edit at the bottom of the page.
In the Batch Edit dialog box, edit the information for the selected members, and then click OK.
NoteAfter you modify the contact information, notify the relevant personnel to ensure they can receive monitoring alerts promptly.
Disable
You can disable an enabled account. After an account is disabled, the user cannot log in to Dataphin and will no longer receive monitoring alerts. Before disabling an account, we recommend transferring the ownership of its assets.
Disable a single account: In the Actions column for the target member, click the
 icon. In the Disable Account dialog box, click OK.
Disable accounts in batches:
In the member list, select multiple members or select Select all on this page at the bottom of the page. Then, click Disable at the bottom of the page.
In the Batch Disable dialog box, click OK.
Enable
You can enable a disabled account. After an account is enabled, the user can log in to Dataphin again and will receive monitoring alerts.
Enable a single account: In the Actions column for the target member, click the
 icon. In the Enable Account dialog box, click OK.
Enable accounts in batches:
In the member list, select multiple members or select Select all on this page at the bottom of the page. Then, click Enable at the bottom of the page.
In the Batch Enable dialog box, click OK.
Transfer ownership
When a user's role or status changes in Dataphin, you can quickly transfer ownership. The original owner will no longer have their permissions. Ensure that you transfer ownership only as needed. For more information, see Transfer ownership.
In the Actions column for the target member, click the
 icon.
In the Transfer ownership dialog box, select a transferee, enter a transfer description, and then click OK.
Add to user group
Add one or more users to a specified user group. Each user group can contain a maximum of 1,000 members.
Add a single member:
In the Actions column for the target member, click the
 icon and select Add to user group.
In the Add to user group dialog box, select a user group, and then click OK.
Add members in batches:
In the member list, select multiple members or select Select all on this page at the bottom of the page. Then, click Add to user group at the bottom of the page.
In the Add to user group dialog box, select a user group, and then click OK.
Delete
Delete redundant or unnecessary members. After a member is deleted, they cannot log in to Dataphin and will no longer receive monitoring alerts. Before deleting a user account, we recommend transferring ownership of its assets. When Dataphin is integrated with other authentication systems, deleting a member only removes the user from the Dataphin member list. It does not delete the user from the integrated authentication system.
Delete a single member:
In the Actions column for the target member, click the
icon and select Delete.In the Delete Account dialog box, click OK.
Delete members in batches:
In the member list, select multiple members or select Select all on this page at the bottom of the page. Then, click Delete at the bottom of the page.
In the Delete Account dialog box, click OK.
Edit member account information
On the member management page, click the icon in the Actions column for the target member to open the Edit Account dialog box.
In the Edit Account dialog box, you can edit the user role, IP allowlist, email address, and mobile phone number. The following table lists the parameters and their descriptions.
Parameter
Description
User role
You can modify the user's global roles or add new global roles. You can select multiple roles. For more information about global roles, see User roles and permissions.
ImportantA super administrator account has most system permissions. You cannot remove the super administrator role, but you can add other roles, such as quality administrator or security administrator, to grant the corresponding permissions.
Email
Enter a valid email address, for example, username@example.com.
Mobile phone
Select a country code and enter the mobile number. You can search for the country code by keyword.
DingTalk UserID
The user's ID in DingTalk. This ID is used for account matching during DingTalk OA approval. You can find it in the address book of the DingTalk admin console. Only users with the member management - manage tenant members permission can edit this field. Users cannot edit their own information.
NoteThis parameter can be configured only after DingTalk OA approval is enabled.
DingTalk group chatbot, Lark group chatbot, WeCom group chatbot
Enter the webhook URL for the DingTalk group chatbot, Lark group chatbot, or WeCom group chatbot. For configuration details, see Add a DingTalk group chatbot as a contact method, Add a Lark group chatbot as a contact method, and Add a WeCom group chatbot as a contact method.
IP allowlist
After you configure an IP allowlist, the user can log in only from the specified IP addresses. This feature is disabled by default and takes effect immediately upon being enabled. You can configure the IP allowlist in the following ways:
Specific IP address: For example, 192.168.0.1. Allows access from the IP address 192.168.0.1.
IP address range: For example, 192.168.0.0/24 allows access from IP addresses in the range of 192.168.0.1 to 192.168.0.255. You can also use the format 192.168.0.0-192.168.0.255.
Multiple IP settings: Enter each address or range on a new line.
NoteThe allowlist applies to the user and will enforce login restrictions across all tenants.
If the allowlist is enabled but misconfigured, the user might be unable to log in from any network.
The settings take effect immediately. Currently logged-in users will be blocked when they refresh the page or open a new one.
Before enabling this feature, confirm the network topology with Dataphin operations personnel and register the IP addresses of all network components between the user's client and the Dataphin server. Otherwise, the system cannot retrieve the user's client IP address.
If the client user connects through technologies such as a VPN or virtual desktop, Dataphin can only identify the IP address after it has been forwarded by the VPN or virtual desktop.
Transfer ownership
Super administrators and system administrators can access the Transfer ownership and Ownership transfer records pages from the Admin center. Regular members can only access these pages from their personal center. The functionality is identical. The following instructions use the member management page as an example.
Transfer ownership
On the member management page, click the
 icon in the Actions column for the target member to open the Transfer ownership dialog box.
In the Transfer ownership dialog box, select a transferee, enter a transfer description, and then click OK.
Transferee: Select the user who will receive ownership. When a regular member initiates a transfer, the system sends an approval task to the selected transferee.
Transfer description: Enter a description for the transfer, up to 128 characters in length.
View ownership transfer records
Super administrators and system administrators can view all historical transfer records. Regular members can only view records where they are the creator, transferor, or transferee.
On the member management page, click the Ownership transfer records  icon in area ① of the figure to view historical transfer records. The features on the My and All tabs are identical. The following figure uses the My tab as an example.
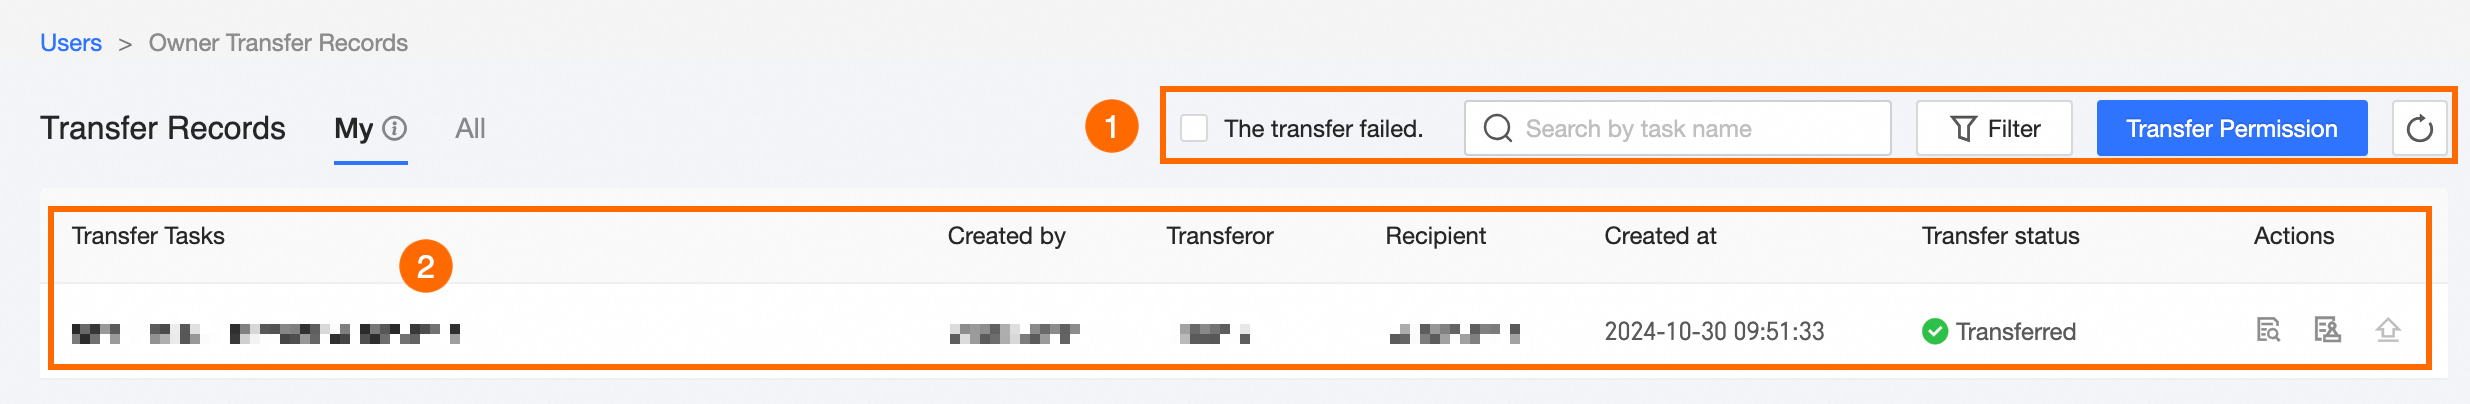
Area | Description |
① Filter and search area |
|
② List area | Displays the Transfer task, Creator, Transferor, Transferee, Creation time, and Transfer status. You can also perform operations such as View details, View approval task, and Resubmit in the Actions column.
|
 icon next to a failed transfer to view the reason for the failure.