Configure an HTTPS certificate for your accelerated domain name to encrypt the connection between clients and CDN nodes. This prevents data interception and tampering over the public network and improves your business security.
Prerequisites
A valid ssl certificate that matches the accelerated domain name is required.
To purchase an ssl certificate, go to the Certificate Management Service (Original SSL Certificate) consolepurchase a commercial certificate.
Certificates issued by a third-party certificate authority (CA) must meet the format requirements. For more information, see Certificate format requirements.
If a client does not pass SNI information when initiating an SSL handshake with a DCDN POP, the DCDN POP cannot guarantee a successful handshake.
Configure or update an HTTPS certificate
Enabling this feature incurs pay-as-you-go charges based on the number of HTTPS requests. These fees are not covered by DCDN data transfer plans. For more information about billing, see HTTPS and dynamic HTTP requests.
If you have configured an HTTPS certificate on another platform, such as a website builder platform, the certificate is not automatically synchronized to DCDN after you add your domain name to DCDN. DCDN nodes deploy certificates independently. You must upload the certificate again in the DCDN console.
-
Log on to the DCDN console.
-
In the left-side navigation pane, click Domain Names.
-
On the Domain Names page, find the target domain name and click Configure.
-
In the left-side navigation tree of the domain name, click HTTPS Settings.
In the SSL Certificate section, click Modify.
In the HTTPS Settings dialog box, enable SSL Acceleration and configure the parameters.
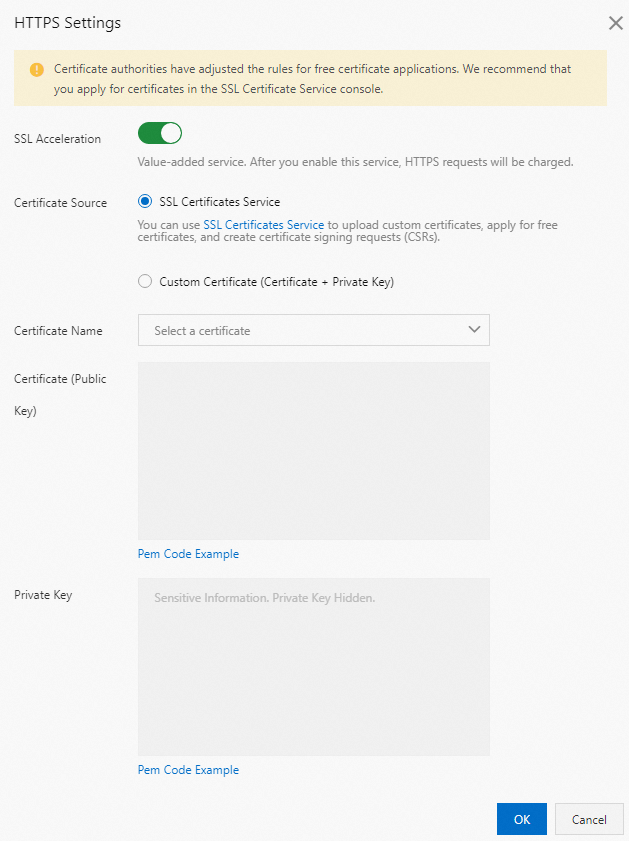
If you have a certificate purchased from Alibaba Cloud Certificate Management Service (Original SSL Certificate), select SSL Certificates Service, and then select your certificate from the Certificate Name drop-down list.
NoteIf you cannot find your certificate, check whether the domain name bound to the certificate is the same as the accelerated domain name.
If you are using a certificate from a third-party CA, select Custom Certificate (Certificate + Private Key). Then, set a Certificate Name and provide the Certificate (Public Key) and Private Key. The certificate is saved in Alibaba Cloud Certificate Management Service (Original SSL Certificate). You can view it in My Certificates.
Parameter
Description
Certificate Name
Enter a name for the certificate.
The name can contain letters, digits, periods (.), underscores (_), and hyphens (-).
NoteThe certificate name must be unique. You can view existing certificates in My Certificates.
If the system prompts that the certificate name already exists, change the name and try uploading again.
Certificate (Public Key)
Paste the content of the PEM-formatted certificate file.
See the Pem Code Example below the text box.
Private Key
Paste the PEM-encoded content of the certificate's private key.
See the Pem Code Example below the text box.
NoteIf your private key starts with
-----BEGIN PRIVATE KEY-----and ends with-----END PRIVATE KEY-----, you must use an OpenSSL tool to convert it. Run the following command, and then paste the content of thenew_server_key.pemfile into the text box.openssl rsa -in old_server_key.pem -out new_server_key.pem
Click OK to complete the configuration.
The certificate name displayed in the DCDN console is different from the certificate name in Alibaba Cloud Certificate Management Service (Original SSL Certificate). The DCDN console automatically generates a name in the format cert-{accelerated domain name}-{timestamp} when you deploy the certificate. This name and the Certificate Name that you set in Certificate Management Service (Original SSL Certificate) belong to two independent naming systems.
If you rename a certificate in Certificate Management Service (Original SSL Certificate), the name displayed in the DCDN console is not automatically updated. To refresh the certificate name shown in the DCDN console, redeploy the certificate on this HTTPS configuration page. This operation only refreshes the displayed certificate name and does not trigger cache purge.
Verify the HTTPS configuration
Browser verification: Access
https://your-accelerated-domain-namein a browser. A lock icon in the address bar with valid certificate details indicates that the configuration is successful.Command-line verification: Run
curl -I https://your-accelerated-domain-name. A200status code confirms the HTTPS service is active.
Disable HTTPS acceleration
You can disable it at any time in the CDN console. The change takes effect immediately. After the feature is disabled, clients can no longer access resources over HTTPS, and the certificate and private key information is removed.
To re-enable HTTPS secure acceleration, select and configure a certificate again.