Most ESA users invest heavily in edge security: WAF rules, DDoS mitigation, bot management. These work well - as long as traffic actually passes through ESA.
The problem is that attackers do not always enter through the front door. If your origin's IP address is discoverable, an attacker can send traffic directly to it, bypassing every security control configured at the edge. Your WAF, DDoS protection, and bot rules become irrelevant because the malicious traffic never touches them.
This is not a theoretical risk. Origin IPs leak through DNS history archives, SSL certificate transparency logs, forgotten subdomains, and misconfigured email headers. Once exposed, the address is out there forever.
Most mature teams already protect their origin with an entry layer - an Alibaba Cloud Server Load Balancer (SLB), a WAF appliance, or both. The load balancer handles traffic distribution and health checks; the WAF filters malicious requests; the origin pool sits behind a controlled boundary. But if that entry layer still accepts traffic from anywhere on the internet, you have moved the front door, not locked it. The attacker simply targets the load balancer or WAF IP instead of a backend server IP.
Origin Protection closes this gap. It ensures that your origin entry layer - whether that is an ALB, CLB, NLB, WAF endpoint, or host firewall - only accepts traffic from ESA's Points of Presence (POPs). Everything else is dropped before it reaches your application.
You might assume your origin IP is private. In practice, it has probably been public at least once. Here are the most common leak paths:
| Leak Source | How It Happens | Why It Persists |
|---|---|---|
| DNS history services | SecurityTrails, ViewDNS.info, and similar tools archive DNS records indefinitely. | If your domain ever pointed directly to your origin - even for a day during setup - the record is stored forever. |
| SSL certificate transparency logs | Certificate Authorities log every issued certificate publicly. | Attackers scrape these logs, extract domain names, and resolve them to find origin IPs. |
| Forgotten subdomains |
dev.example.com, staging.example.com, or old microsites bypass ESA. |
These subdomains often point directly to the origin and are never cleaned up. |
| Email headers | Application servers send mail directly from the origin. | SMTP headers can expose the origin IP if not routed through a third-party mail service. |
Once an attacker has the origin or load-balancer IP, they can send DDoS traffic directly, probe for vulnerabilities without triggering WAF rules, exploit origin weaknesses that ESA would have blocked, or cause outages while ESA dashboards report that everything is fine. The result is the same: your edge security investment is undermined by a single exposed address.
Origin Protection is conceptually simple: allow inbound traffic only from ESA's POP IP addresses. Drop everything else.
Even if an attacker discovers your origin or load-balancer IP, their traffic cannot get through. The only path to your origin is through ESA, where WAF, DDoS, bot management, and custom rules all apply.
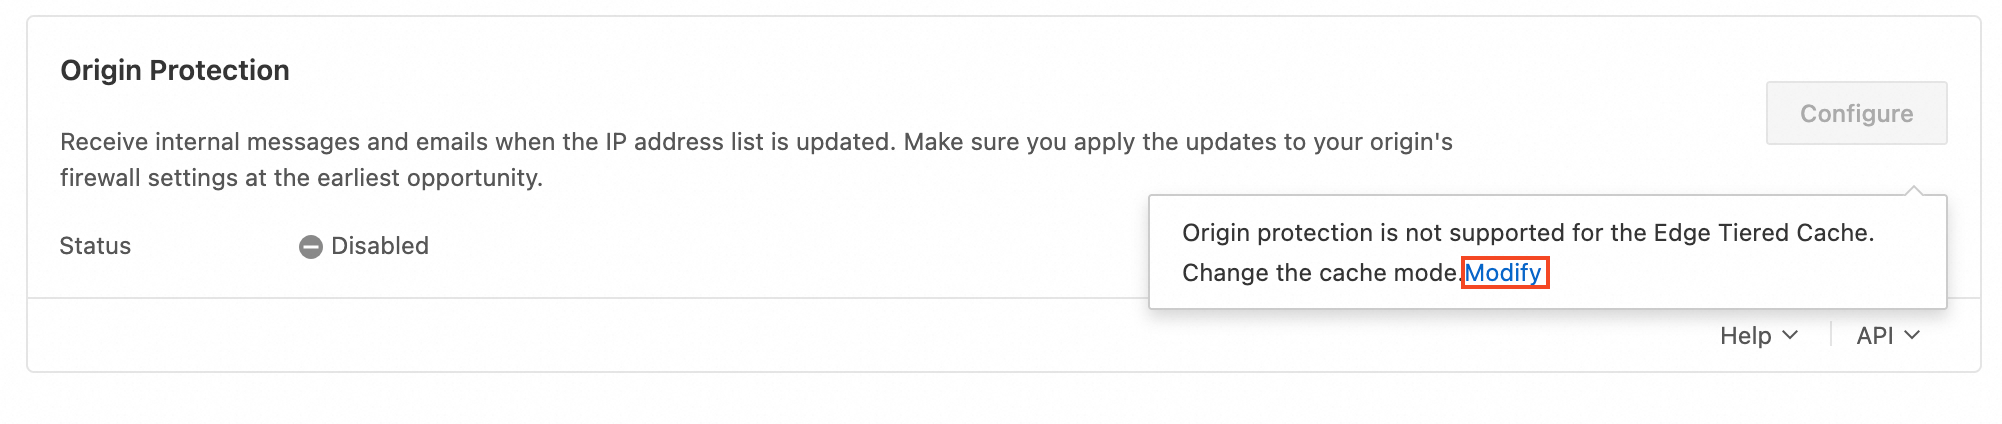
Prerequisite: Origin Protection requires a caching architecture with at least two tiers. If your Tiered Cache policy is set to Edge Tiered Cache (single tier), you cannot enable Origin Protection - ESA's back-to-origin traffic would come from too many POP IPs to whitelist effectively.
To fix this, hover over the Configure button and click Modify in the tooltip to jump to the Tiered Cache page:
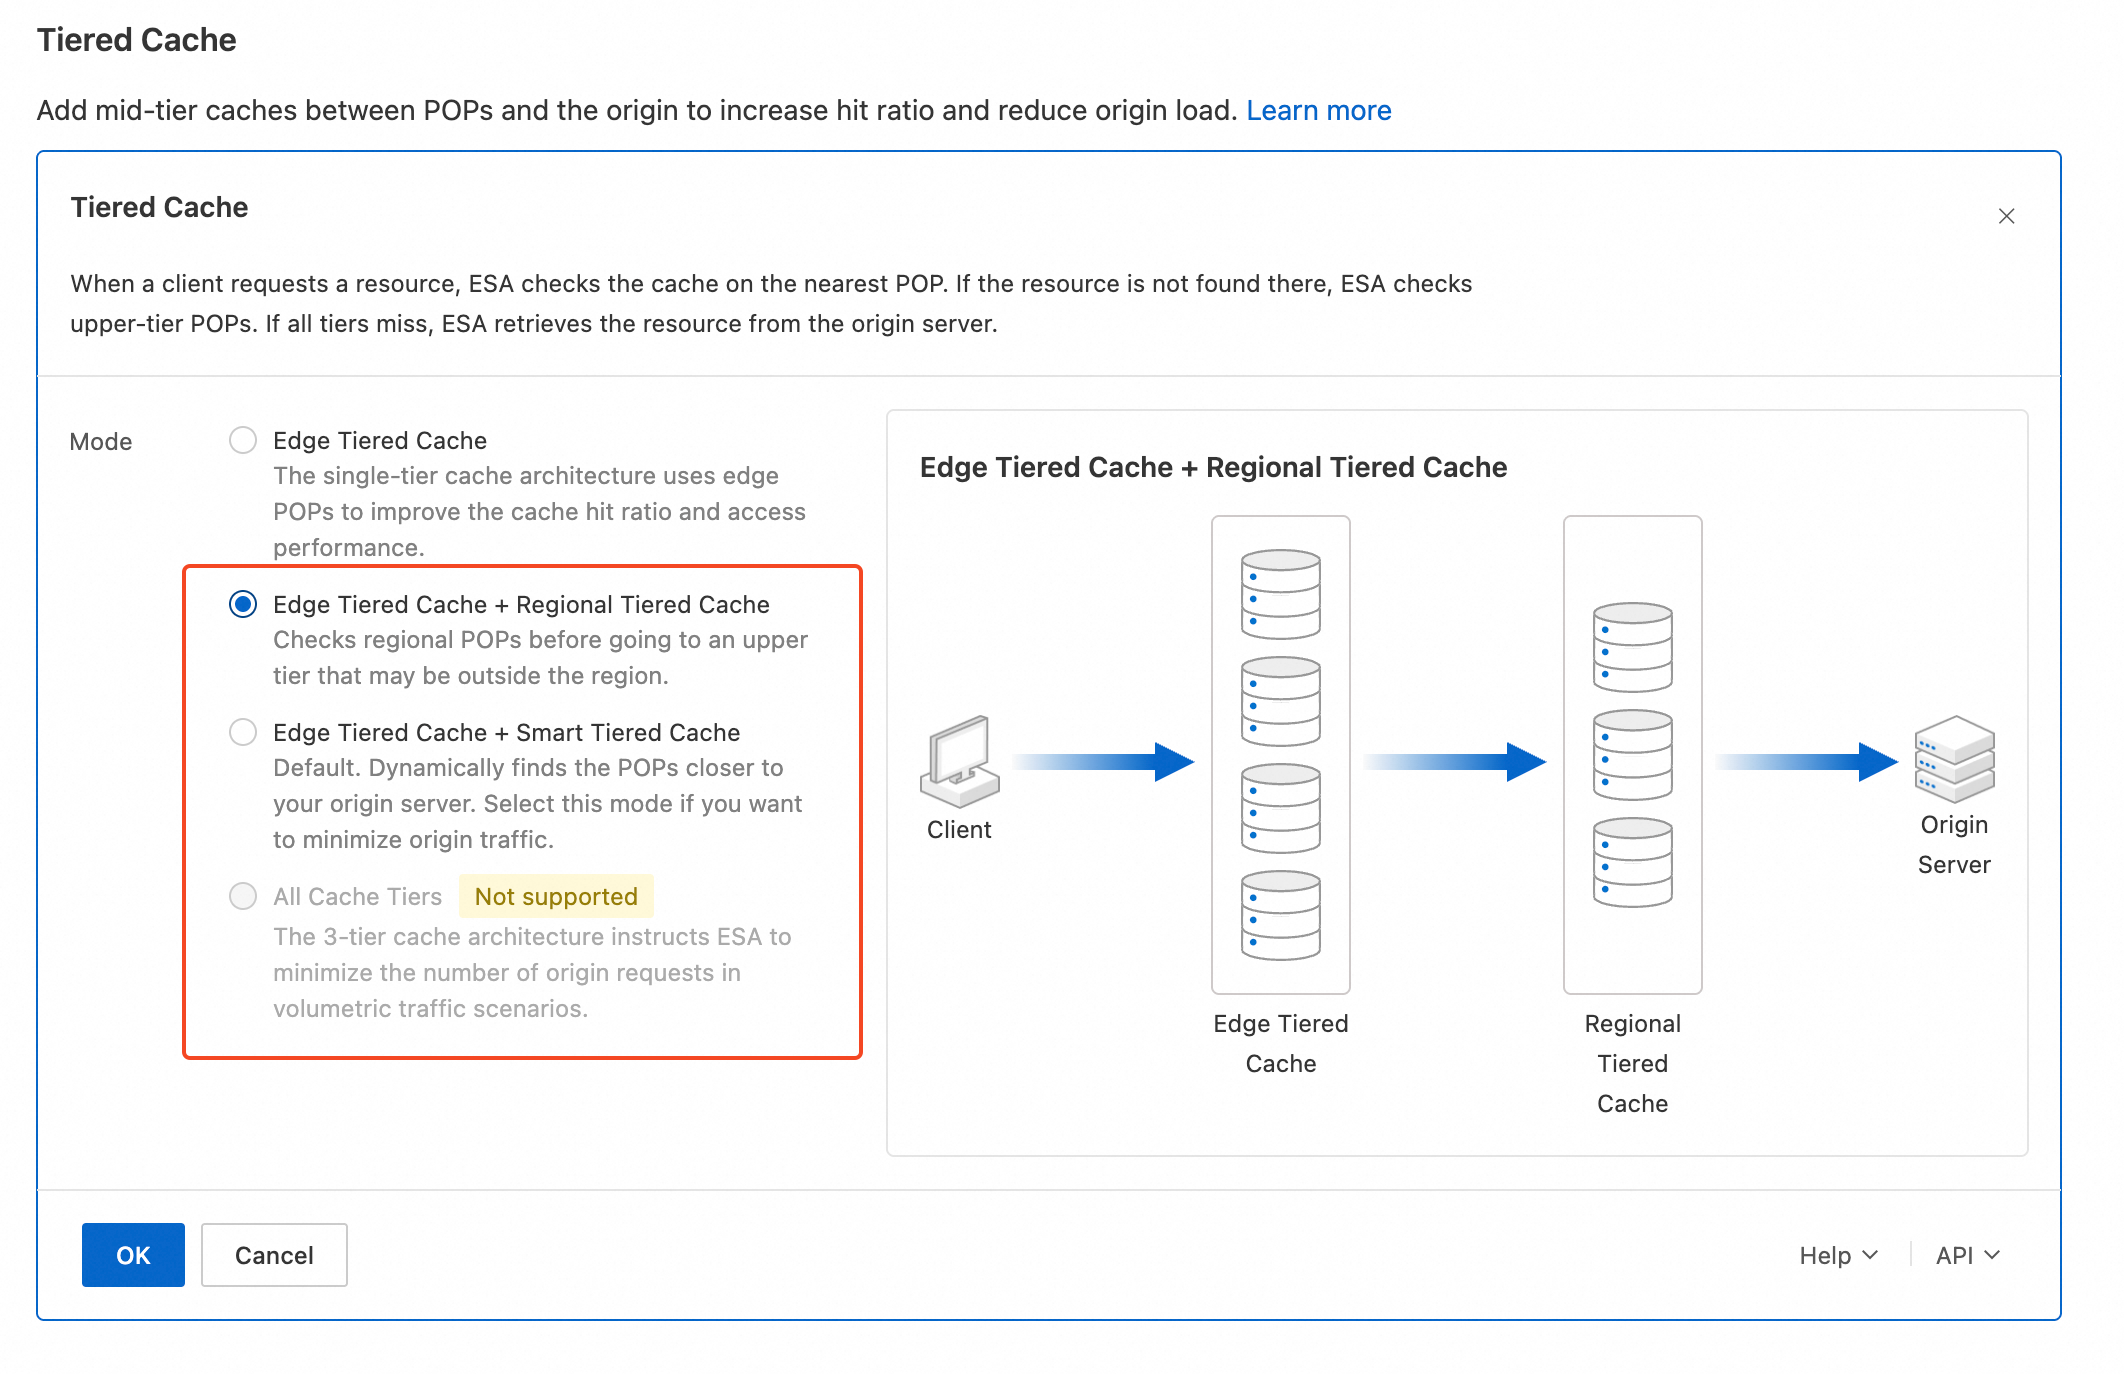
On the Tiered Cache page, click Configure, select a multi-tier caching architecture (Regional, Smart, or Cache Reserve), and then you can enable Origin Protection:
The core of Origin Protection happens in the ESA console - you turn the feature on and copy the POP IP list, then apply that list wherever your origin lives.
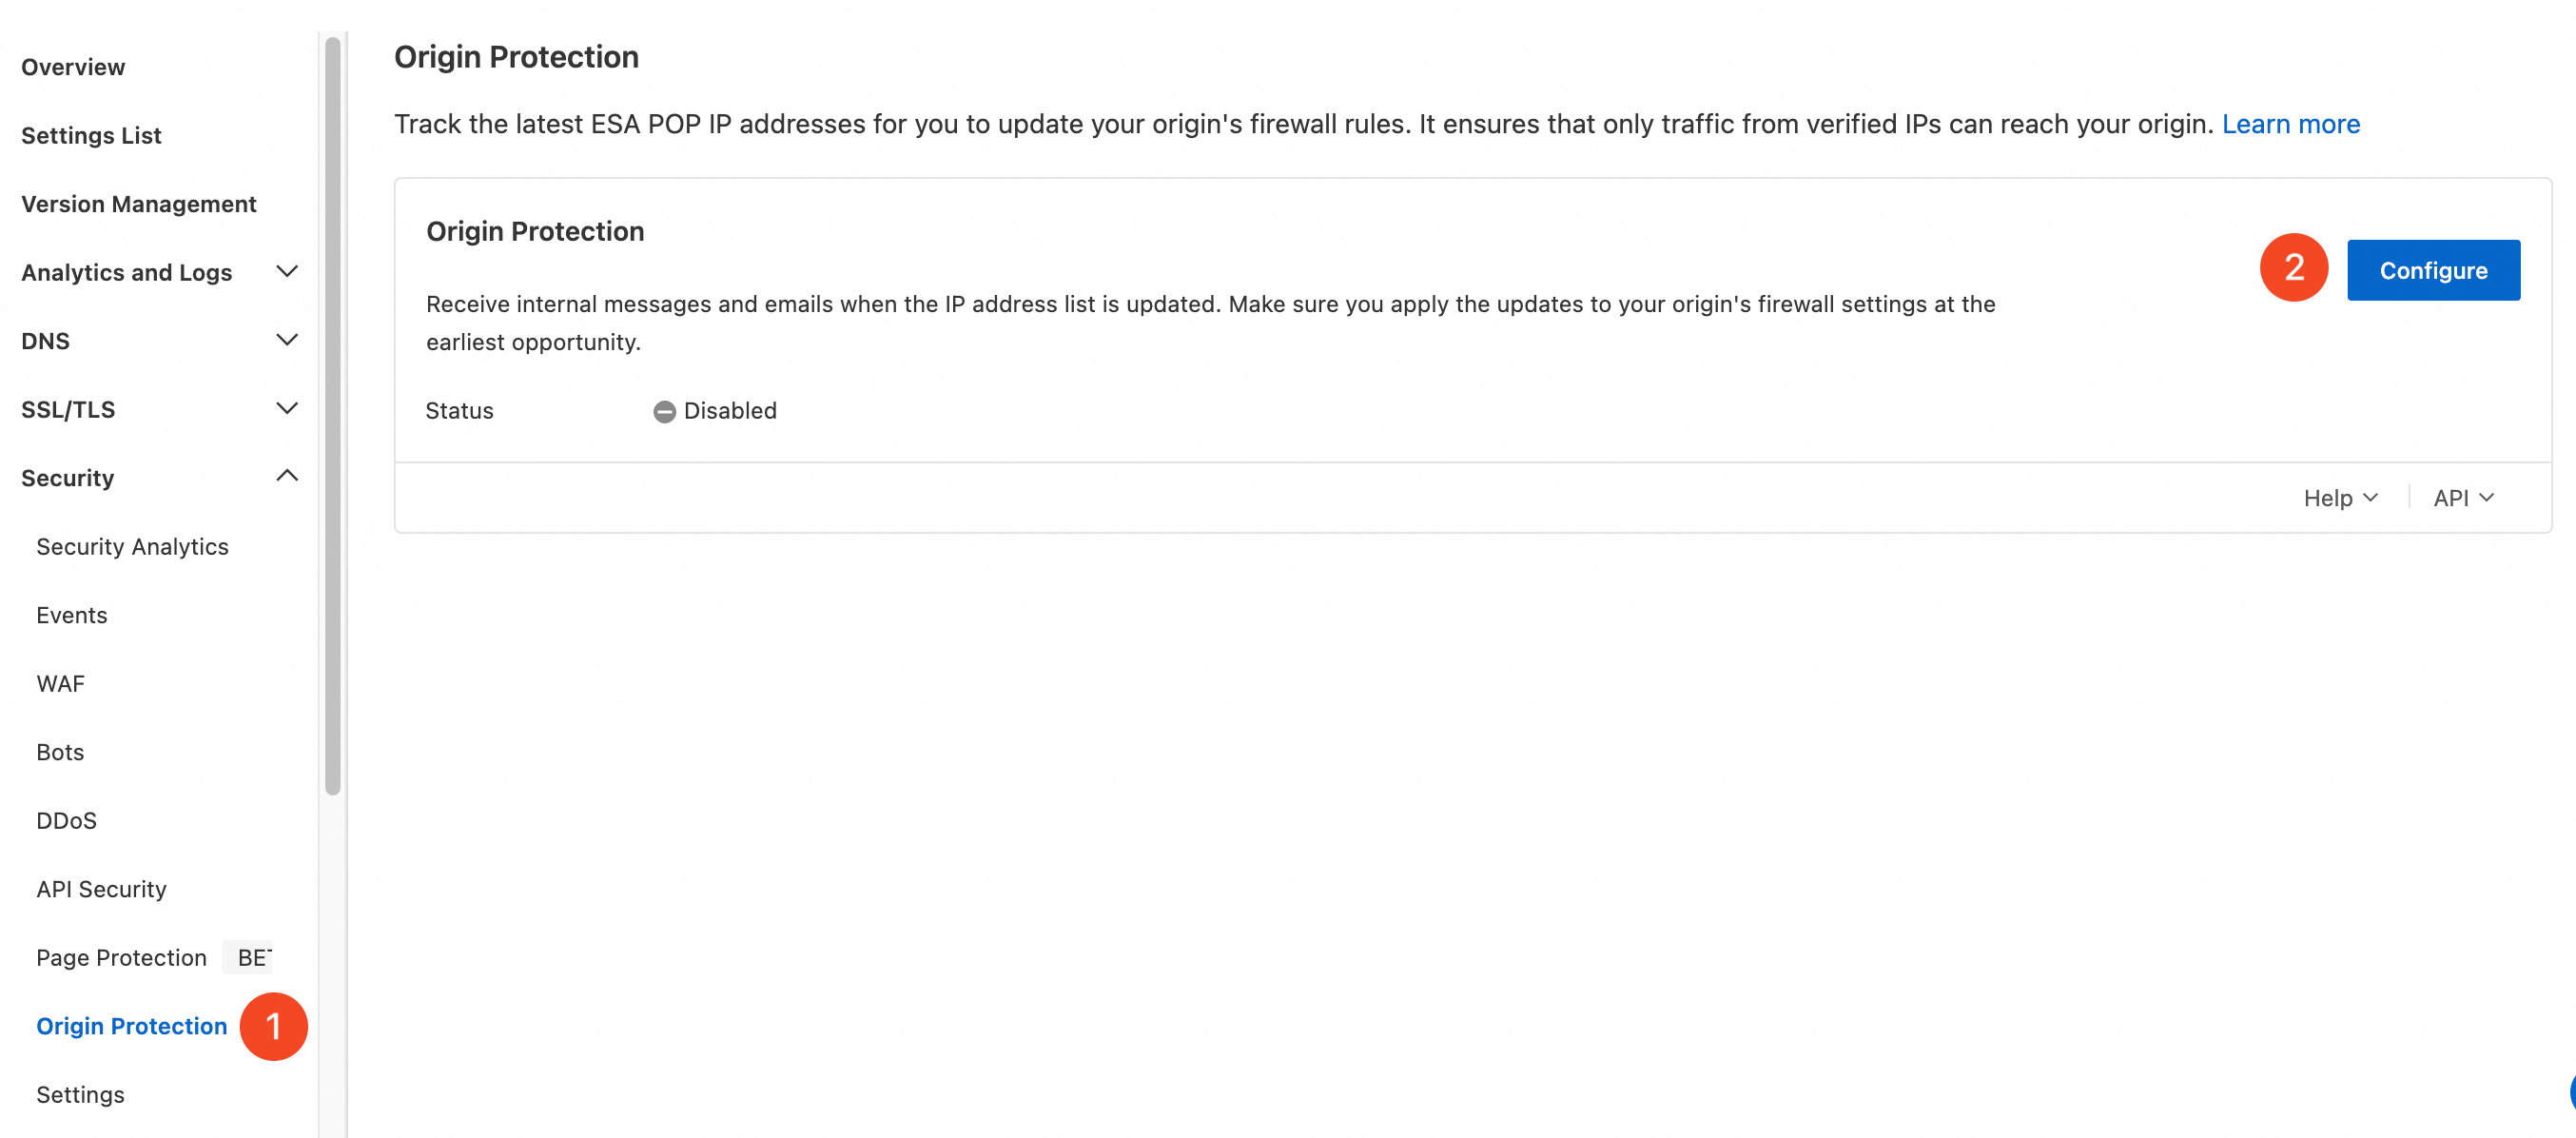
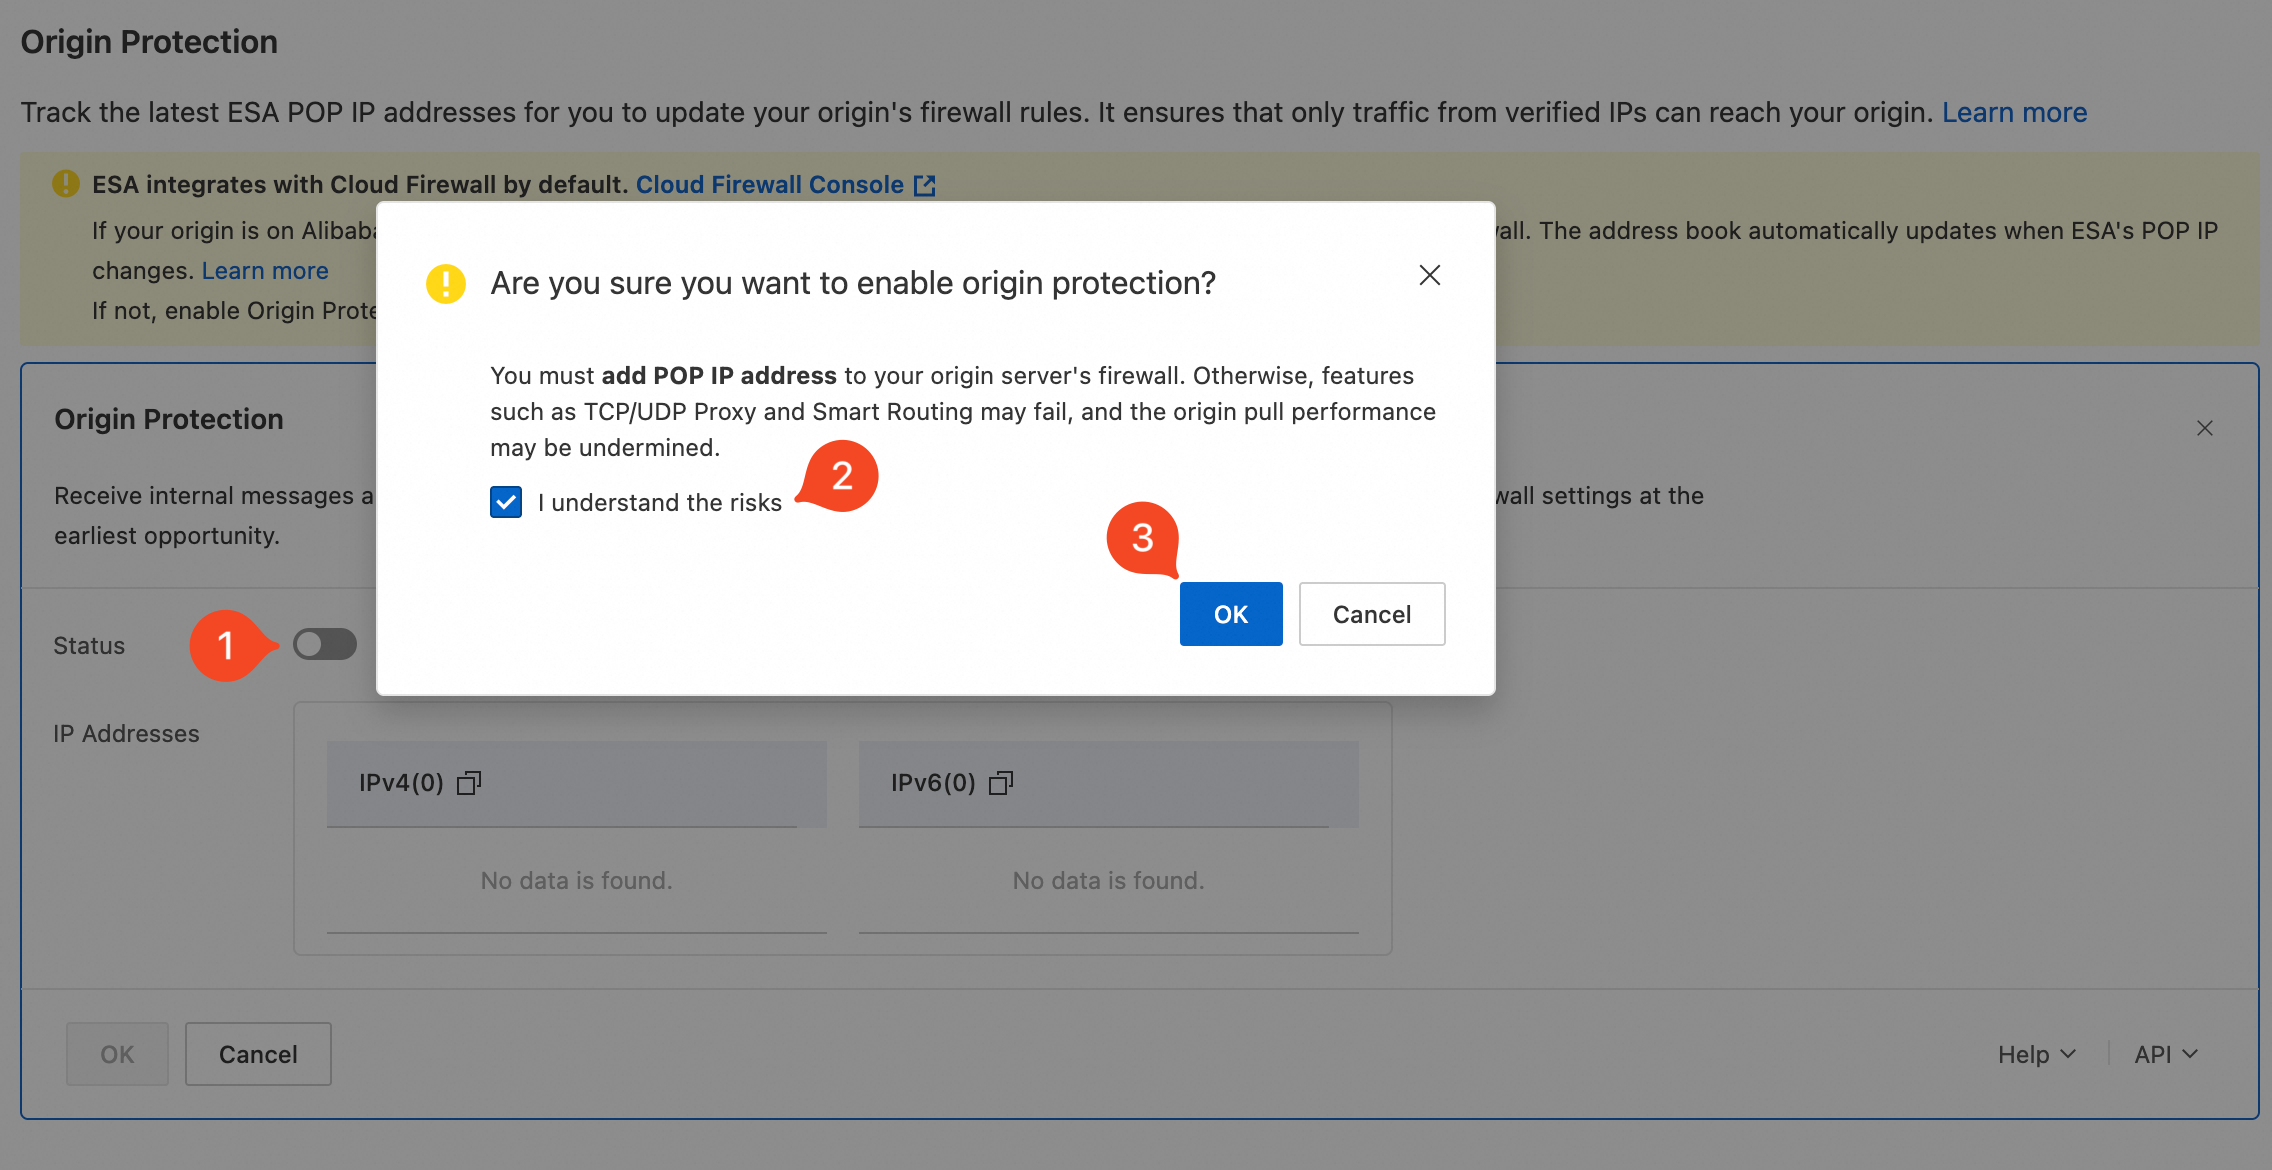
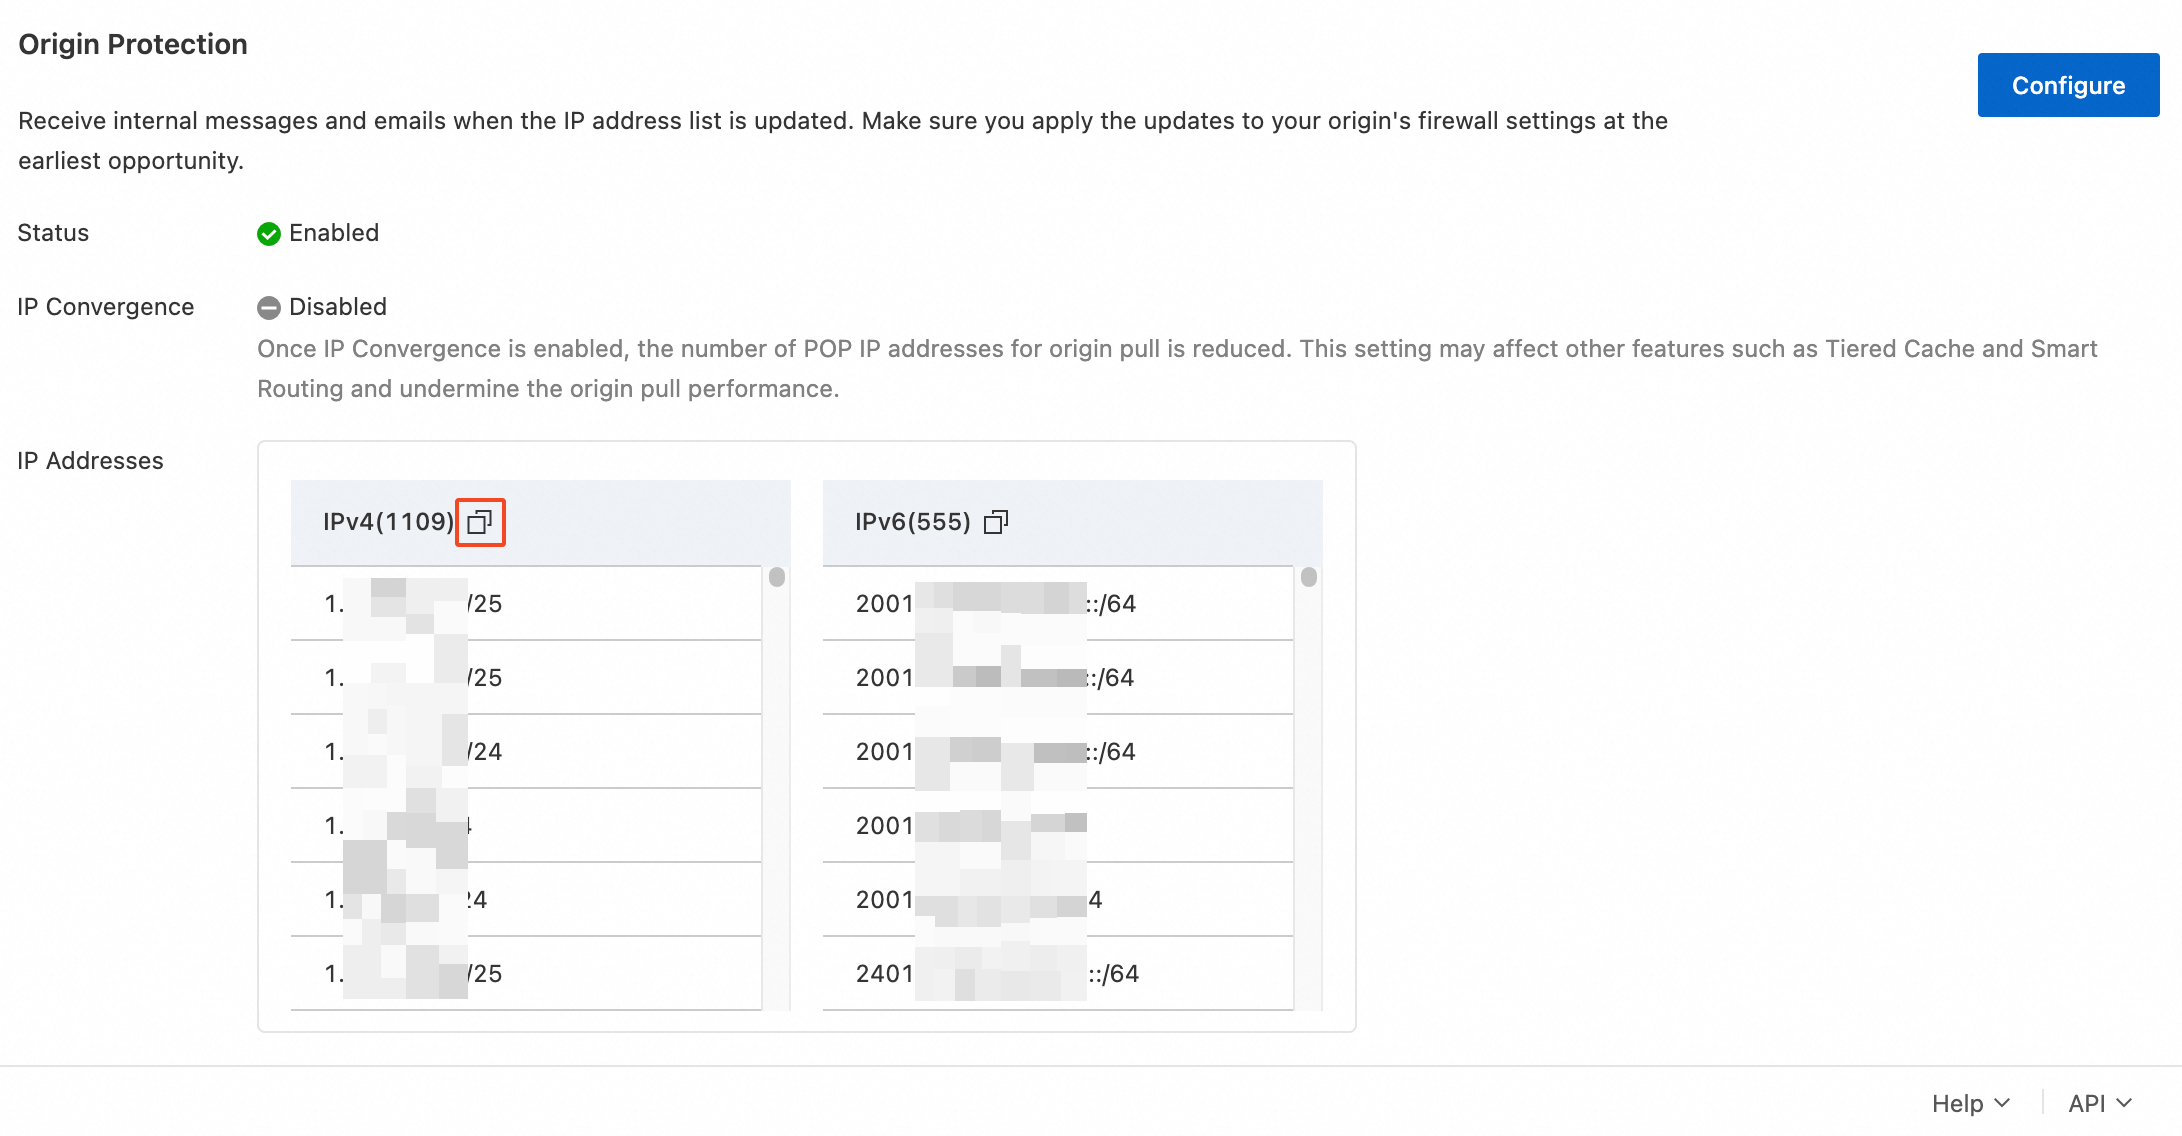
Important: If you stop using ESA, you must manually remove these rules from your origin firewall to prevent access disruptions.
There is no single "correct" place to apply the list. Enforce it at the outermost layer that only ESA talks to - everything behind it then inherits the protection.
| Enforcement Point | Best For | Maintenance | IP-List Updates |
|---|---|---|---|
| Load Balancer ACL (ALB / CLB / NLB) | Origins behind an Alibaba Cloud SLB | Low - configured in the LB console | Manual |
| Cloud Firewall | Multi-origin, hybrid, or regulated environments | Low - fully managed address book | Automatic |
| ECS Security Group | Origins running directly on ECS, no LB in front | Medium | Manual (update Prefix List) |
| Host firewall (iptables, firewalld) | On-premise or non-Alibaba Cloud origins | High | Manual (re-apply rules) |
If your origin already sits behind an Alibaba Cloud load balancer, the load balancer's access control list is the cleanest enforcement point - no deeper firewall changes.
esa-origin-pops and add the ESA POP CIDR blocks as ACL entries.esa-origin-pops ACL, then Save.Whitelist mode means the listener allows access only from IP addresses in the ACL and denies all other requests. The same pattern applies to CLB (access-control whitelist) and NLB (ACL association).
ESA is integrated with Cloud Firewall. If your origins are all on Alibaba Cloud and you use Cloud Firewall, enable Origin Protection and then turn on the Auto-apply Latest Origin Fetch IP List switch - Cloud Firewall then updates the origin-fetch IP information automatically.
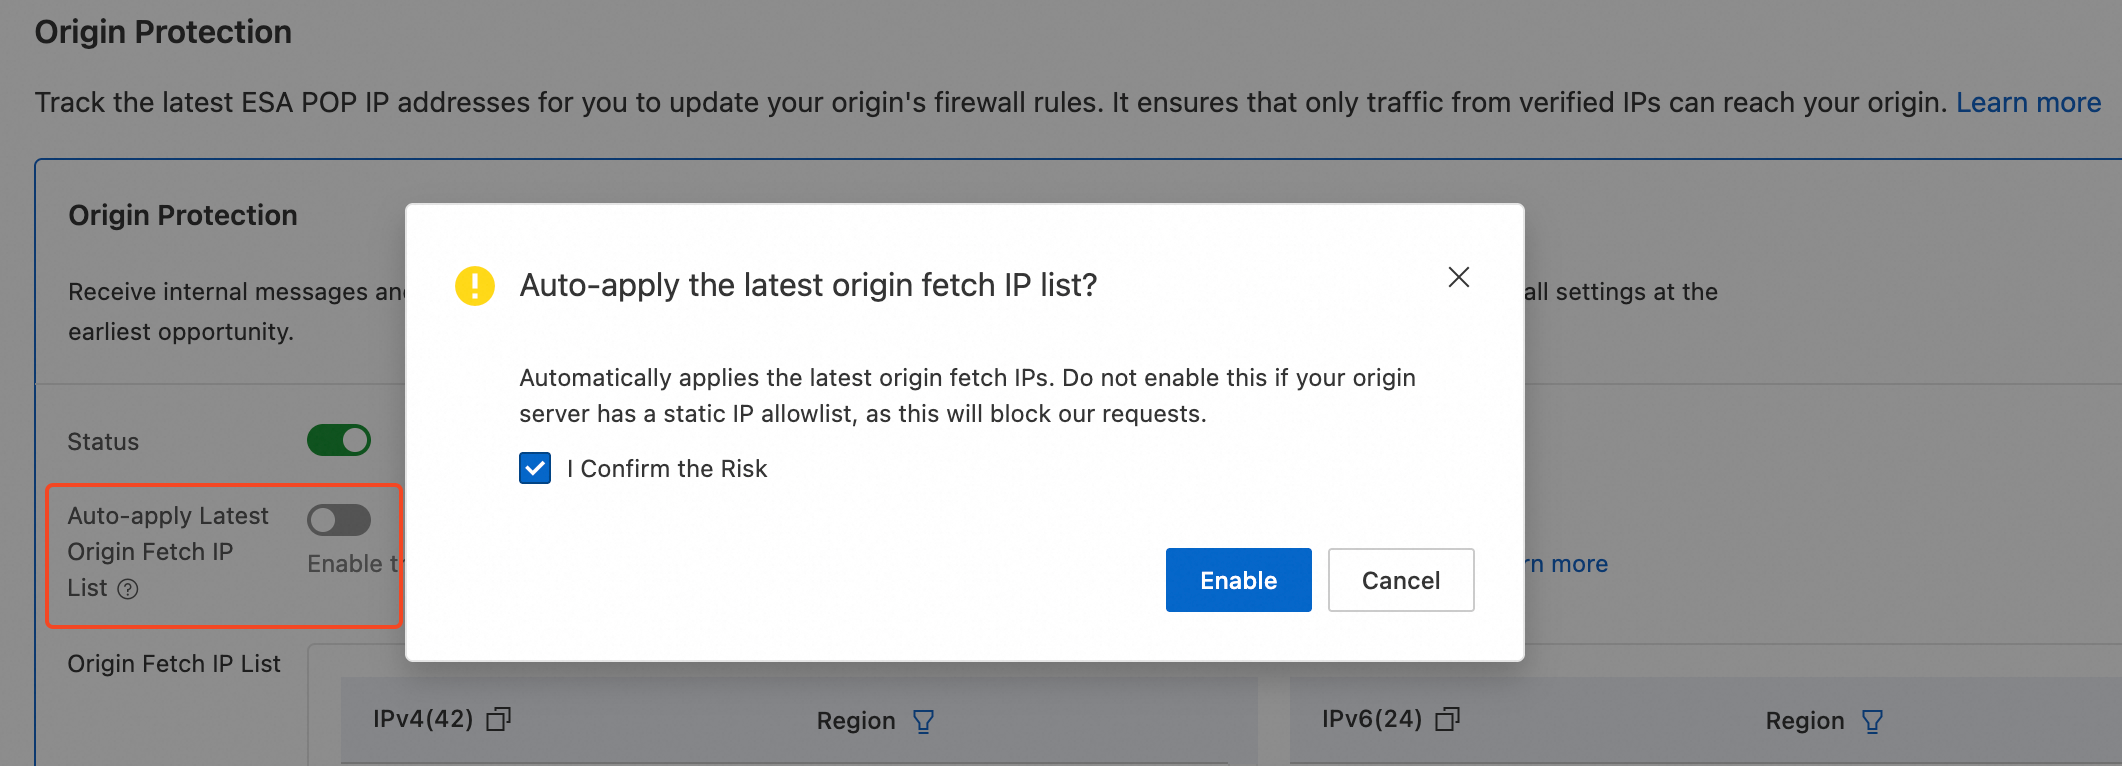
Then create an inbound rule in Cloud Firewall > Access Control > Internet Border Firewall:
Add a second rule to deny all other inbound traffic to those ports. When ESA adds or removes POPs, the address book updates on its own - no manual edits.
If your origin is an ECS instance, use Prefix Lists so you can whitelist both IPv4 and IPv6 ranges in one object.
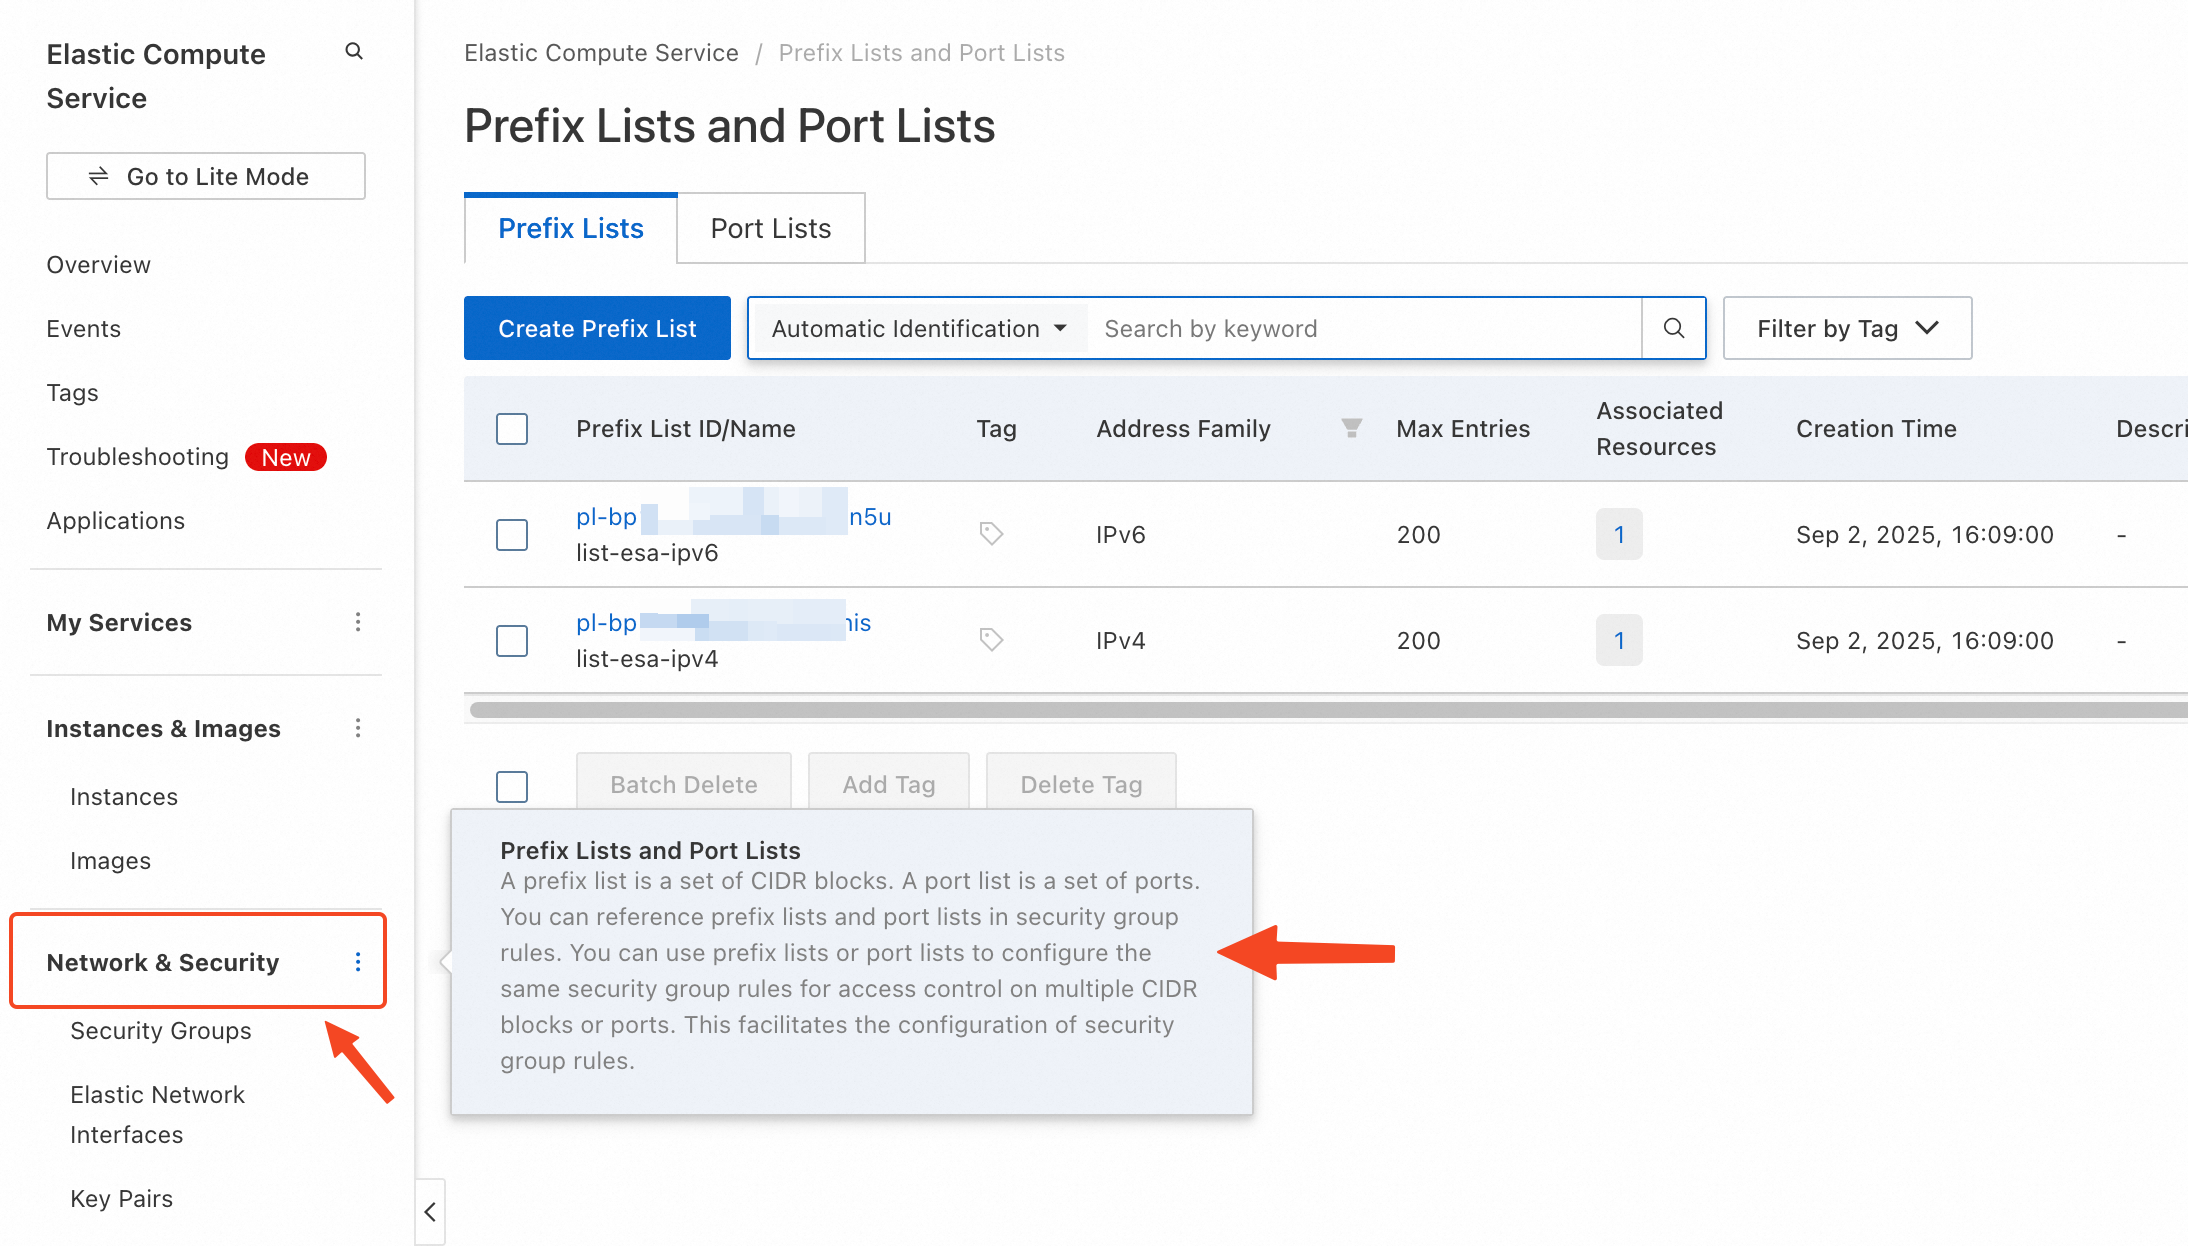
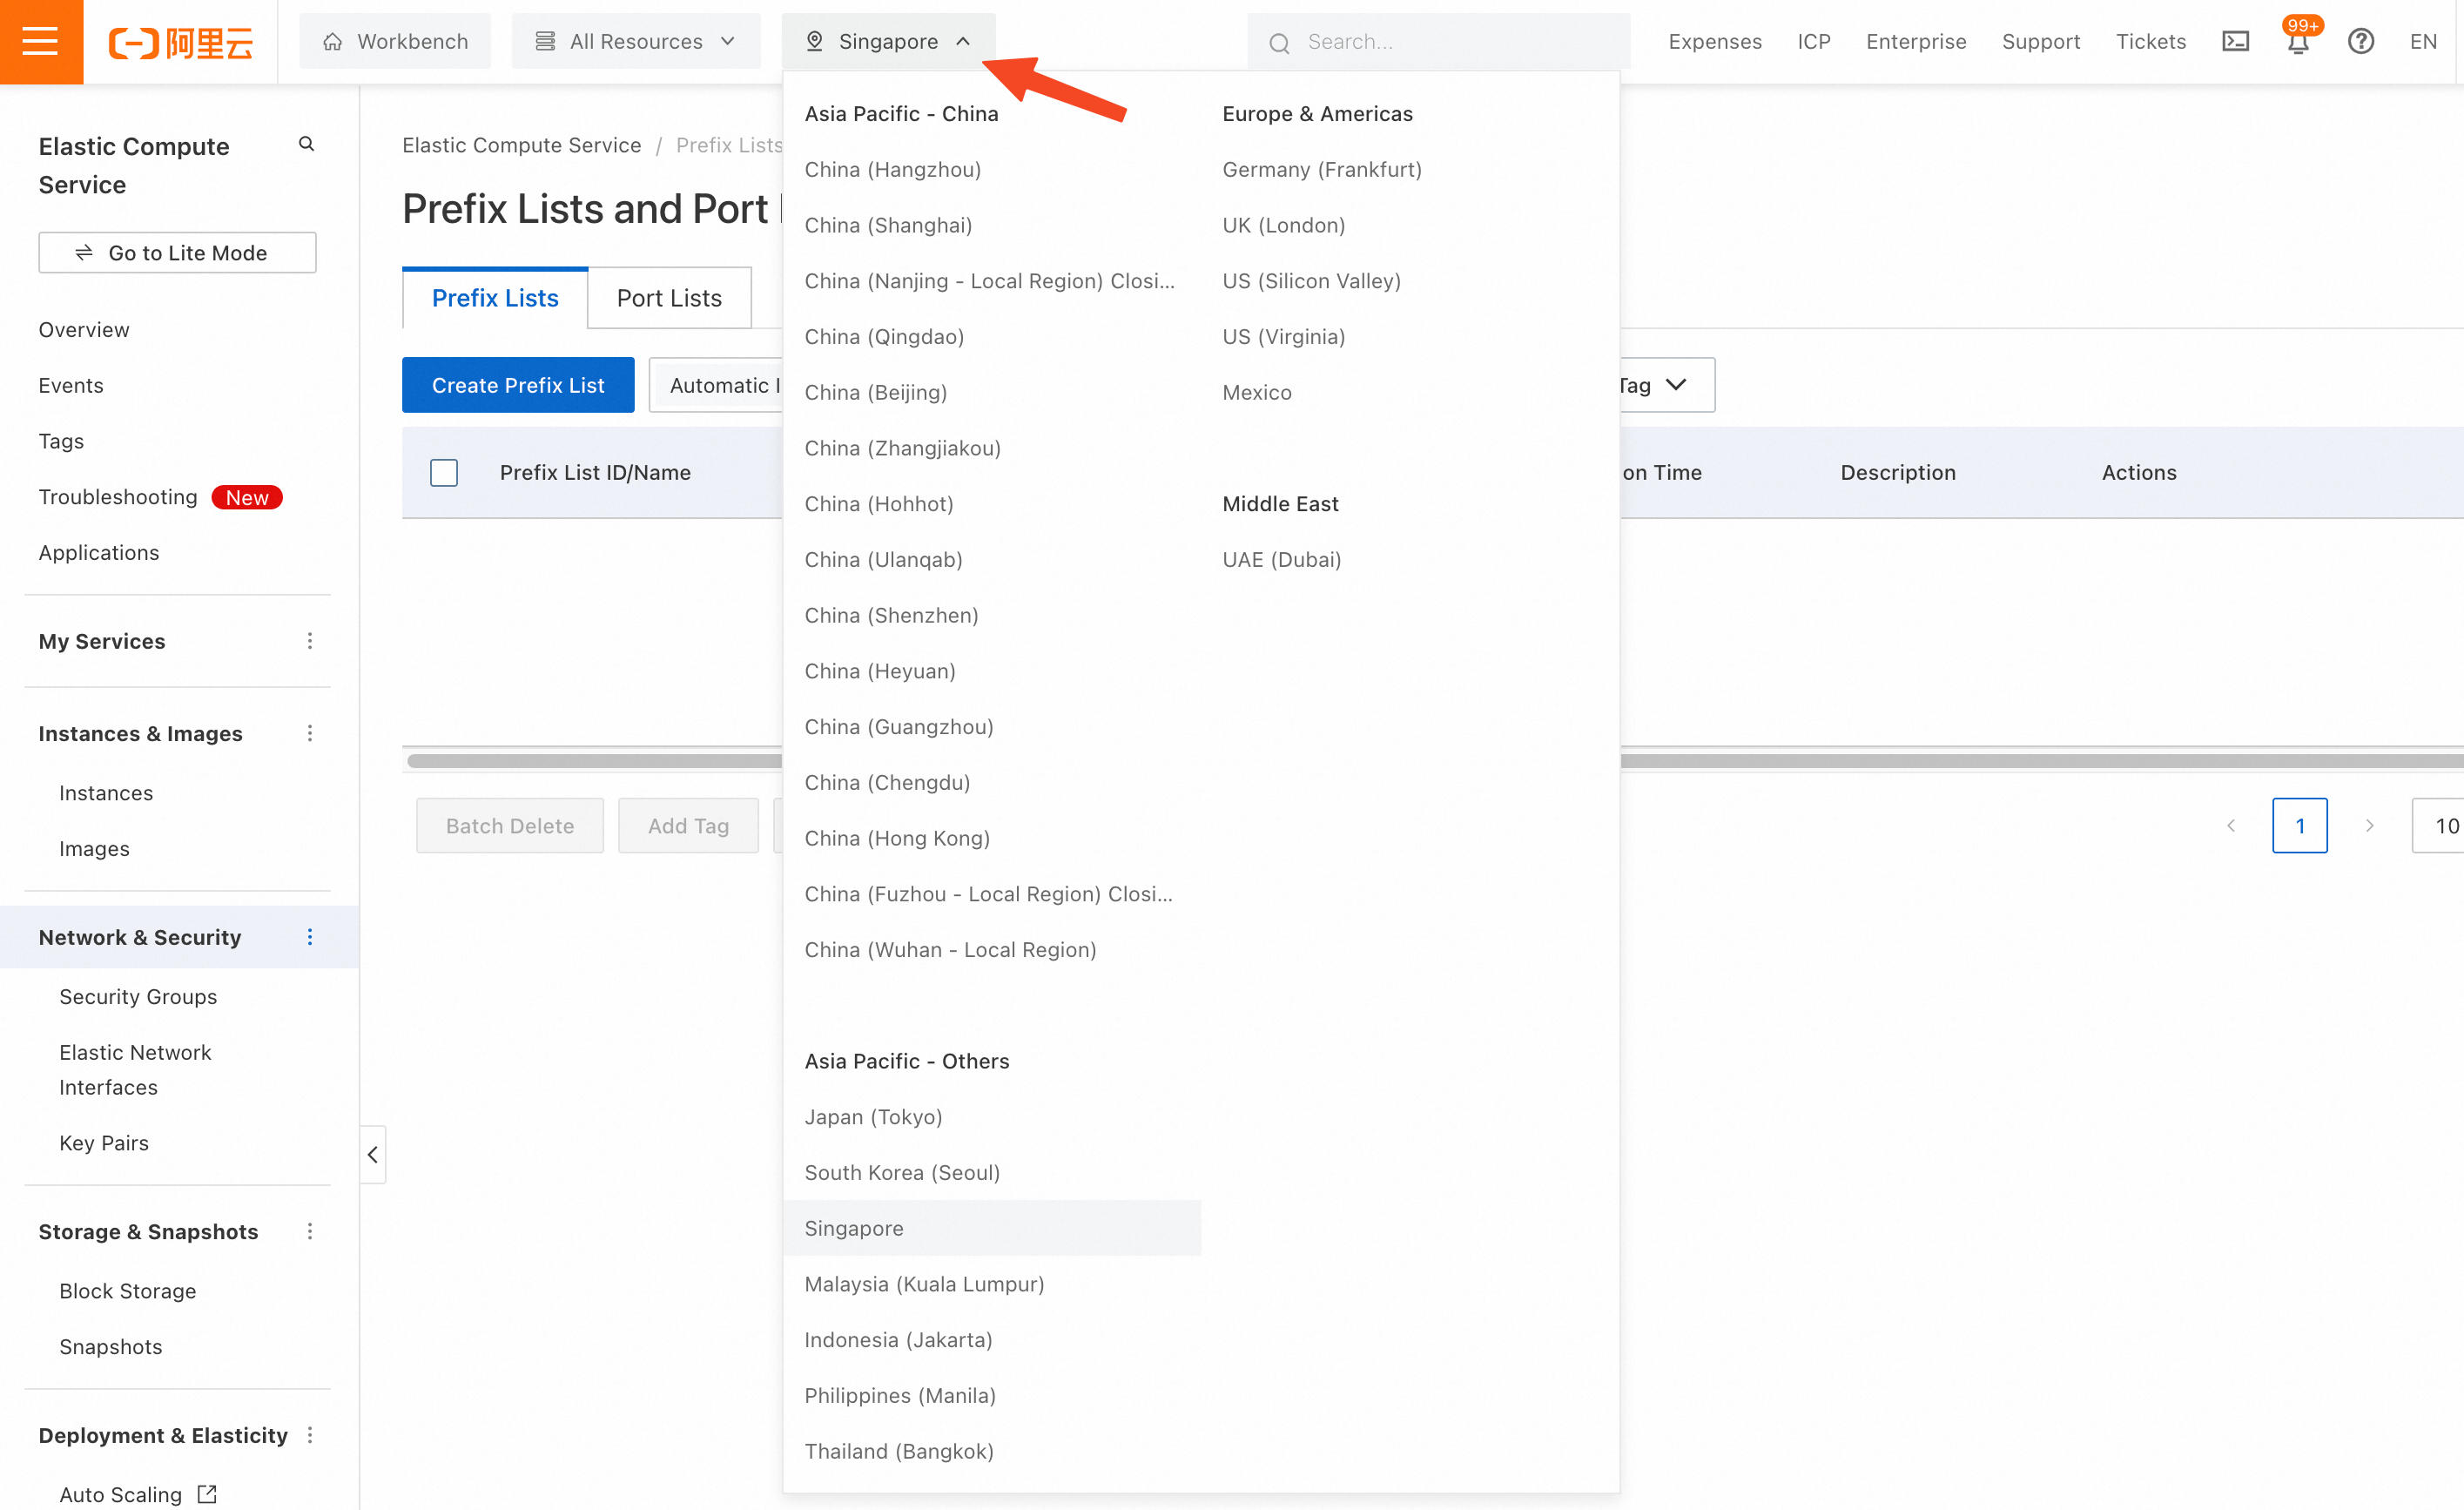
list-esa-ipv4, Address family = IPv4, Max entries = 200, then paste the IPv4 CIDR blocks from the ESA list under Prefix list entries and click OK.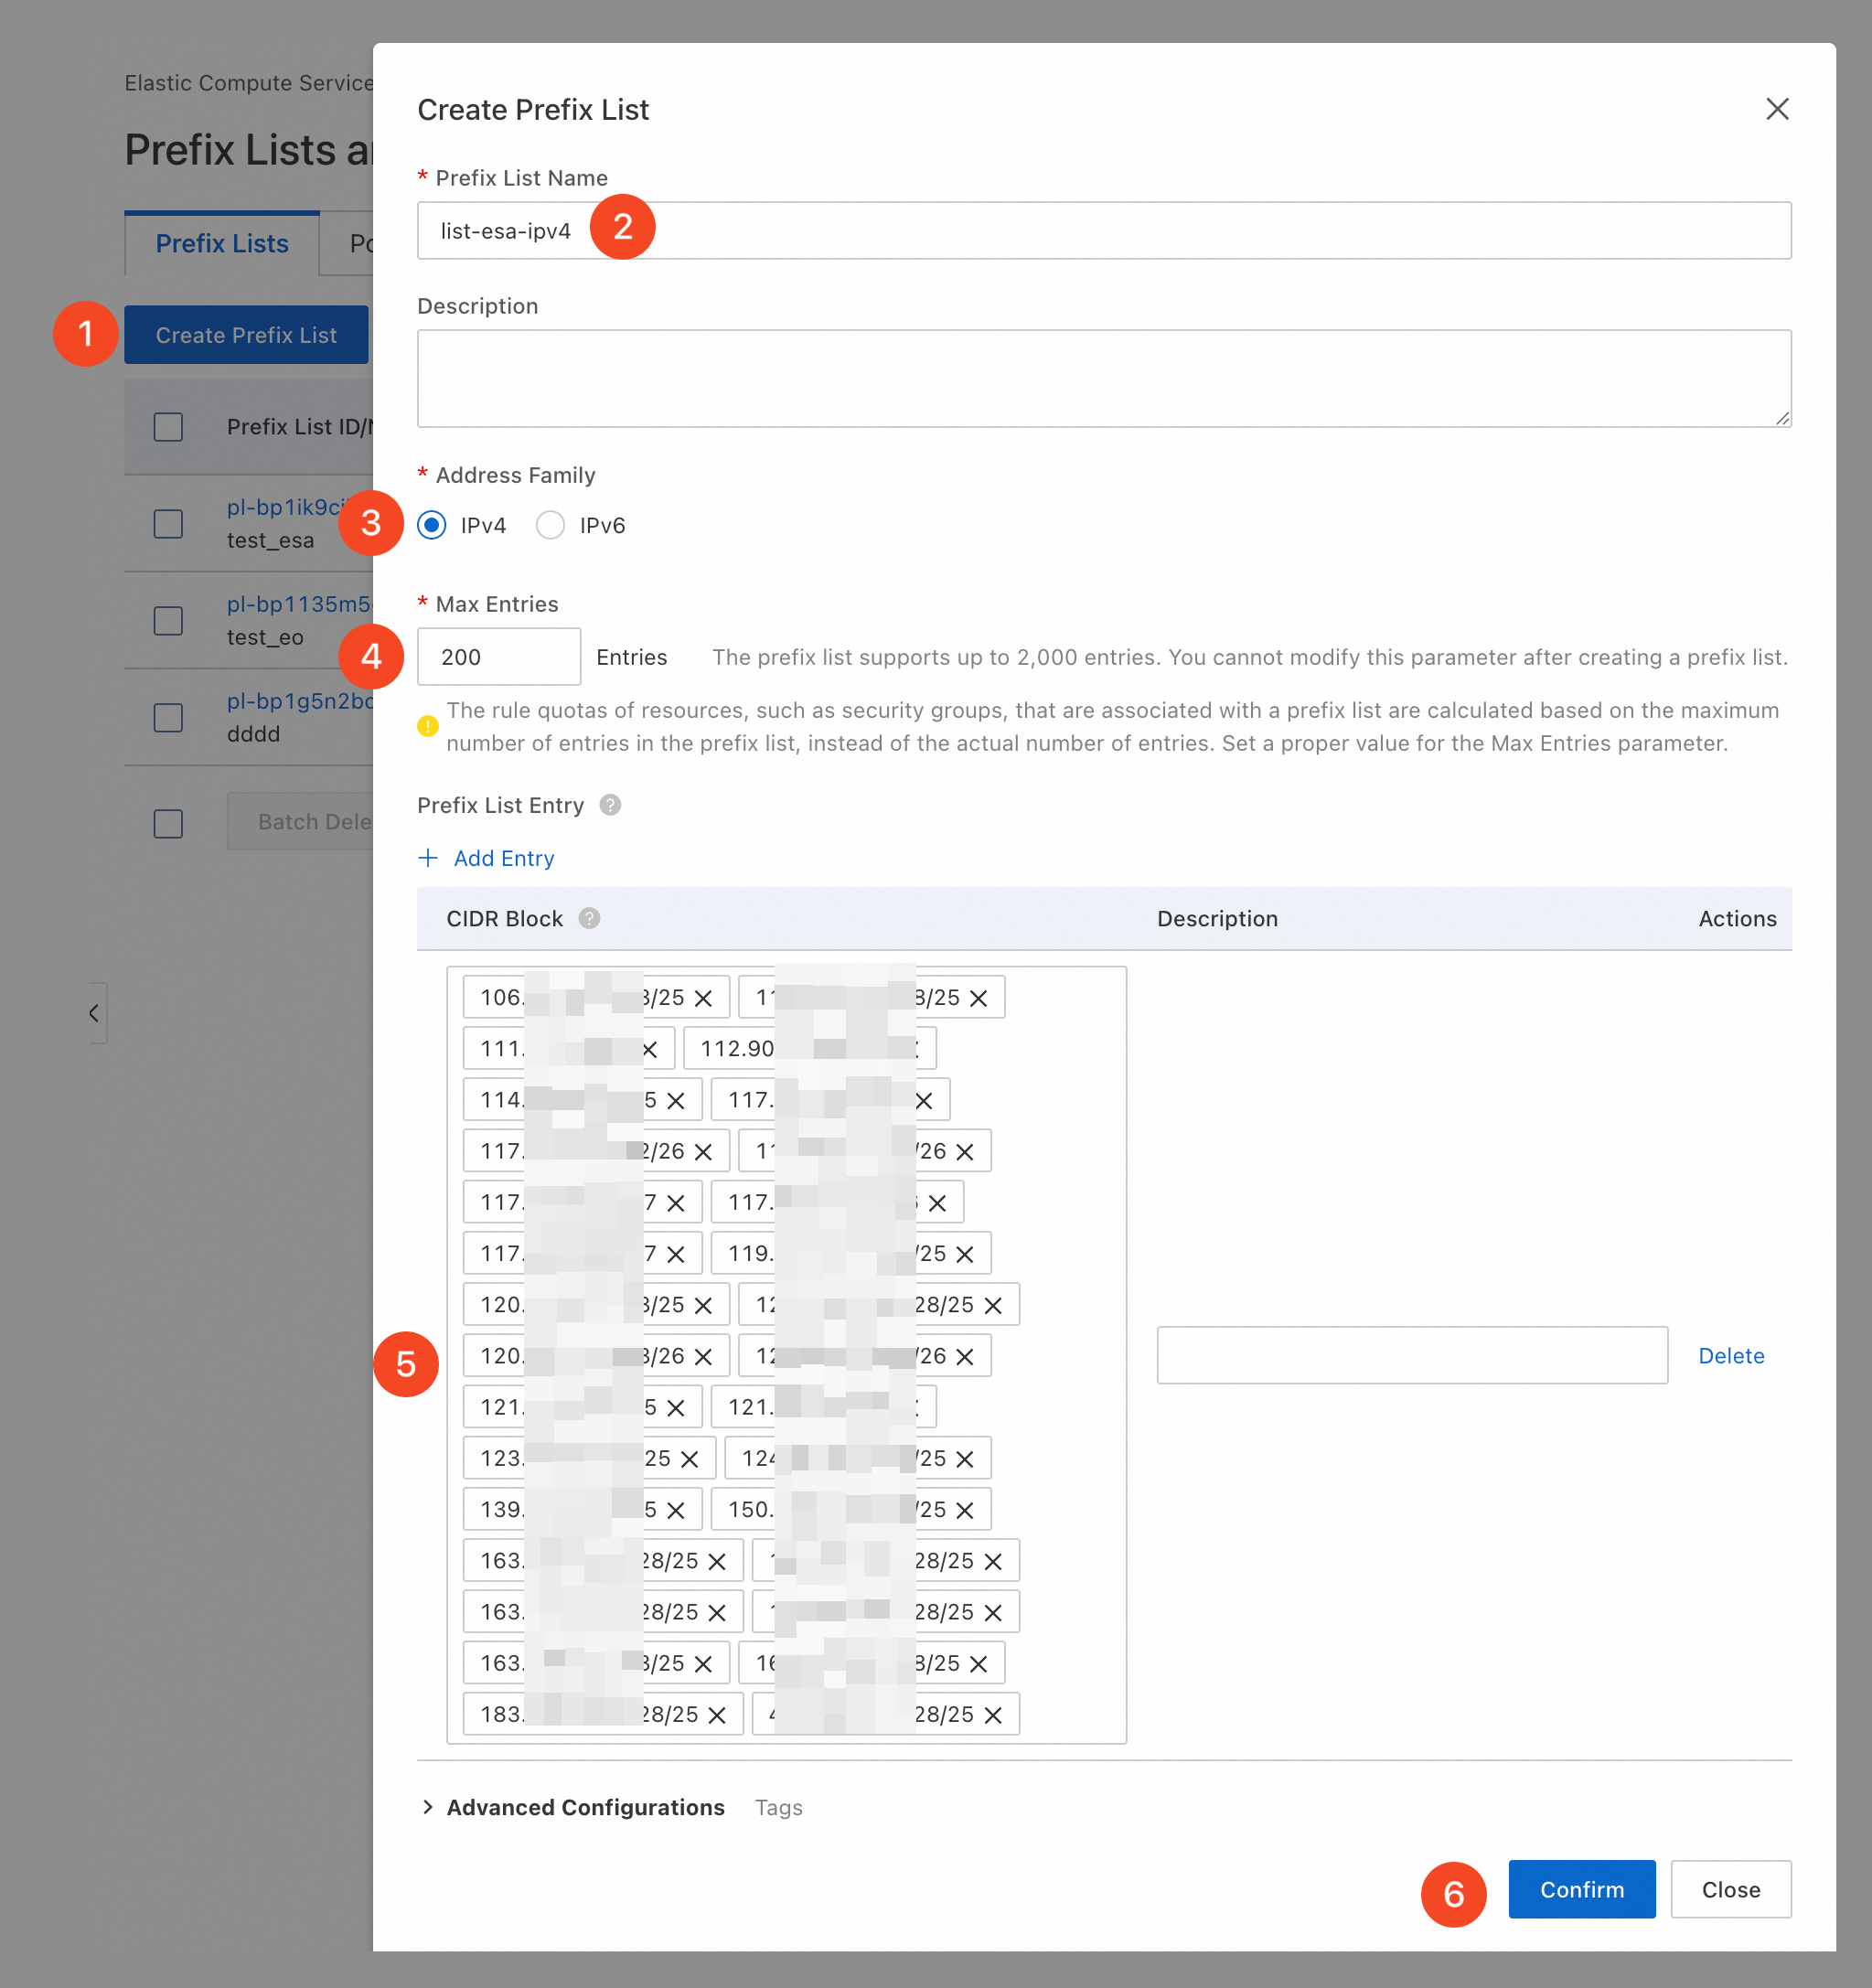
list-esa-ipv6, Address family = IPv6, Max entries = 200, paste the IPv6 blocks, click OK.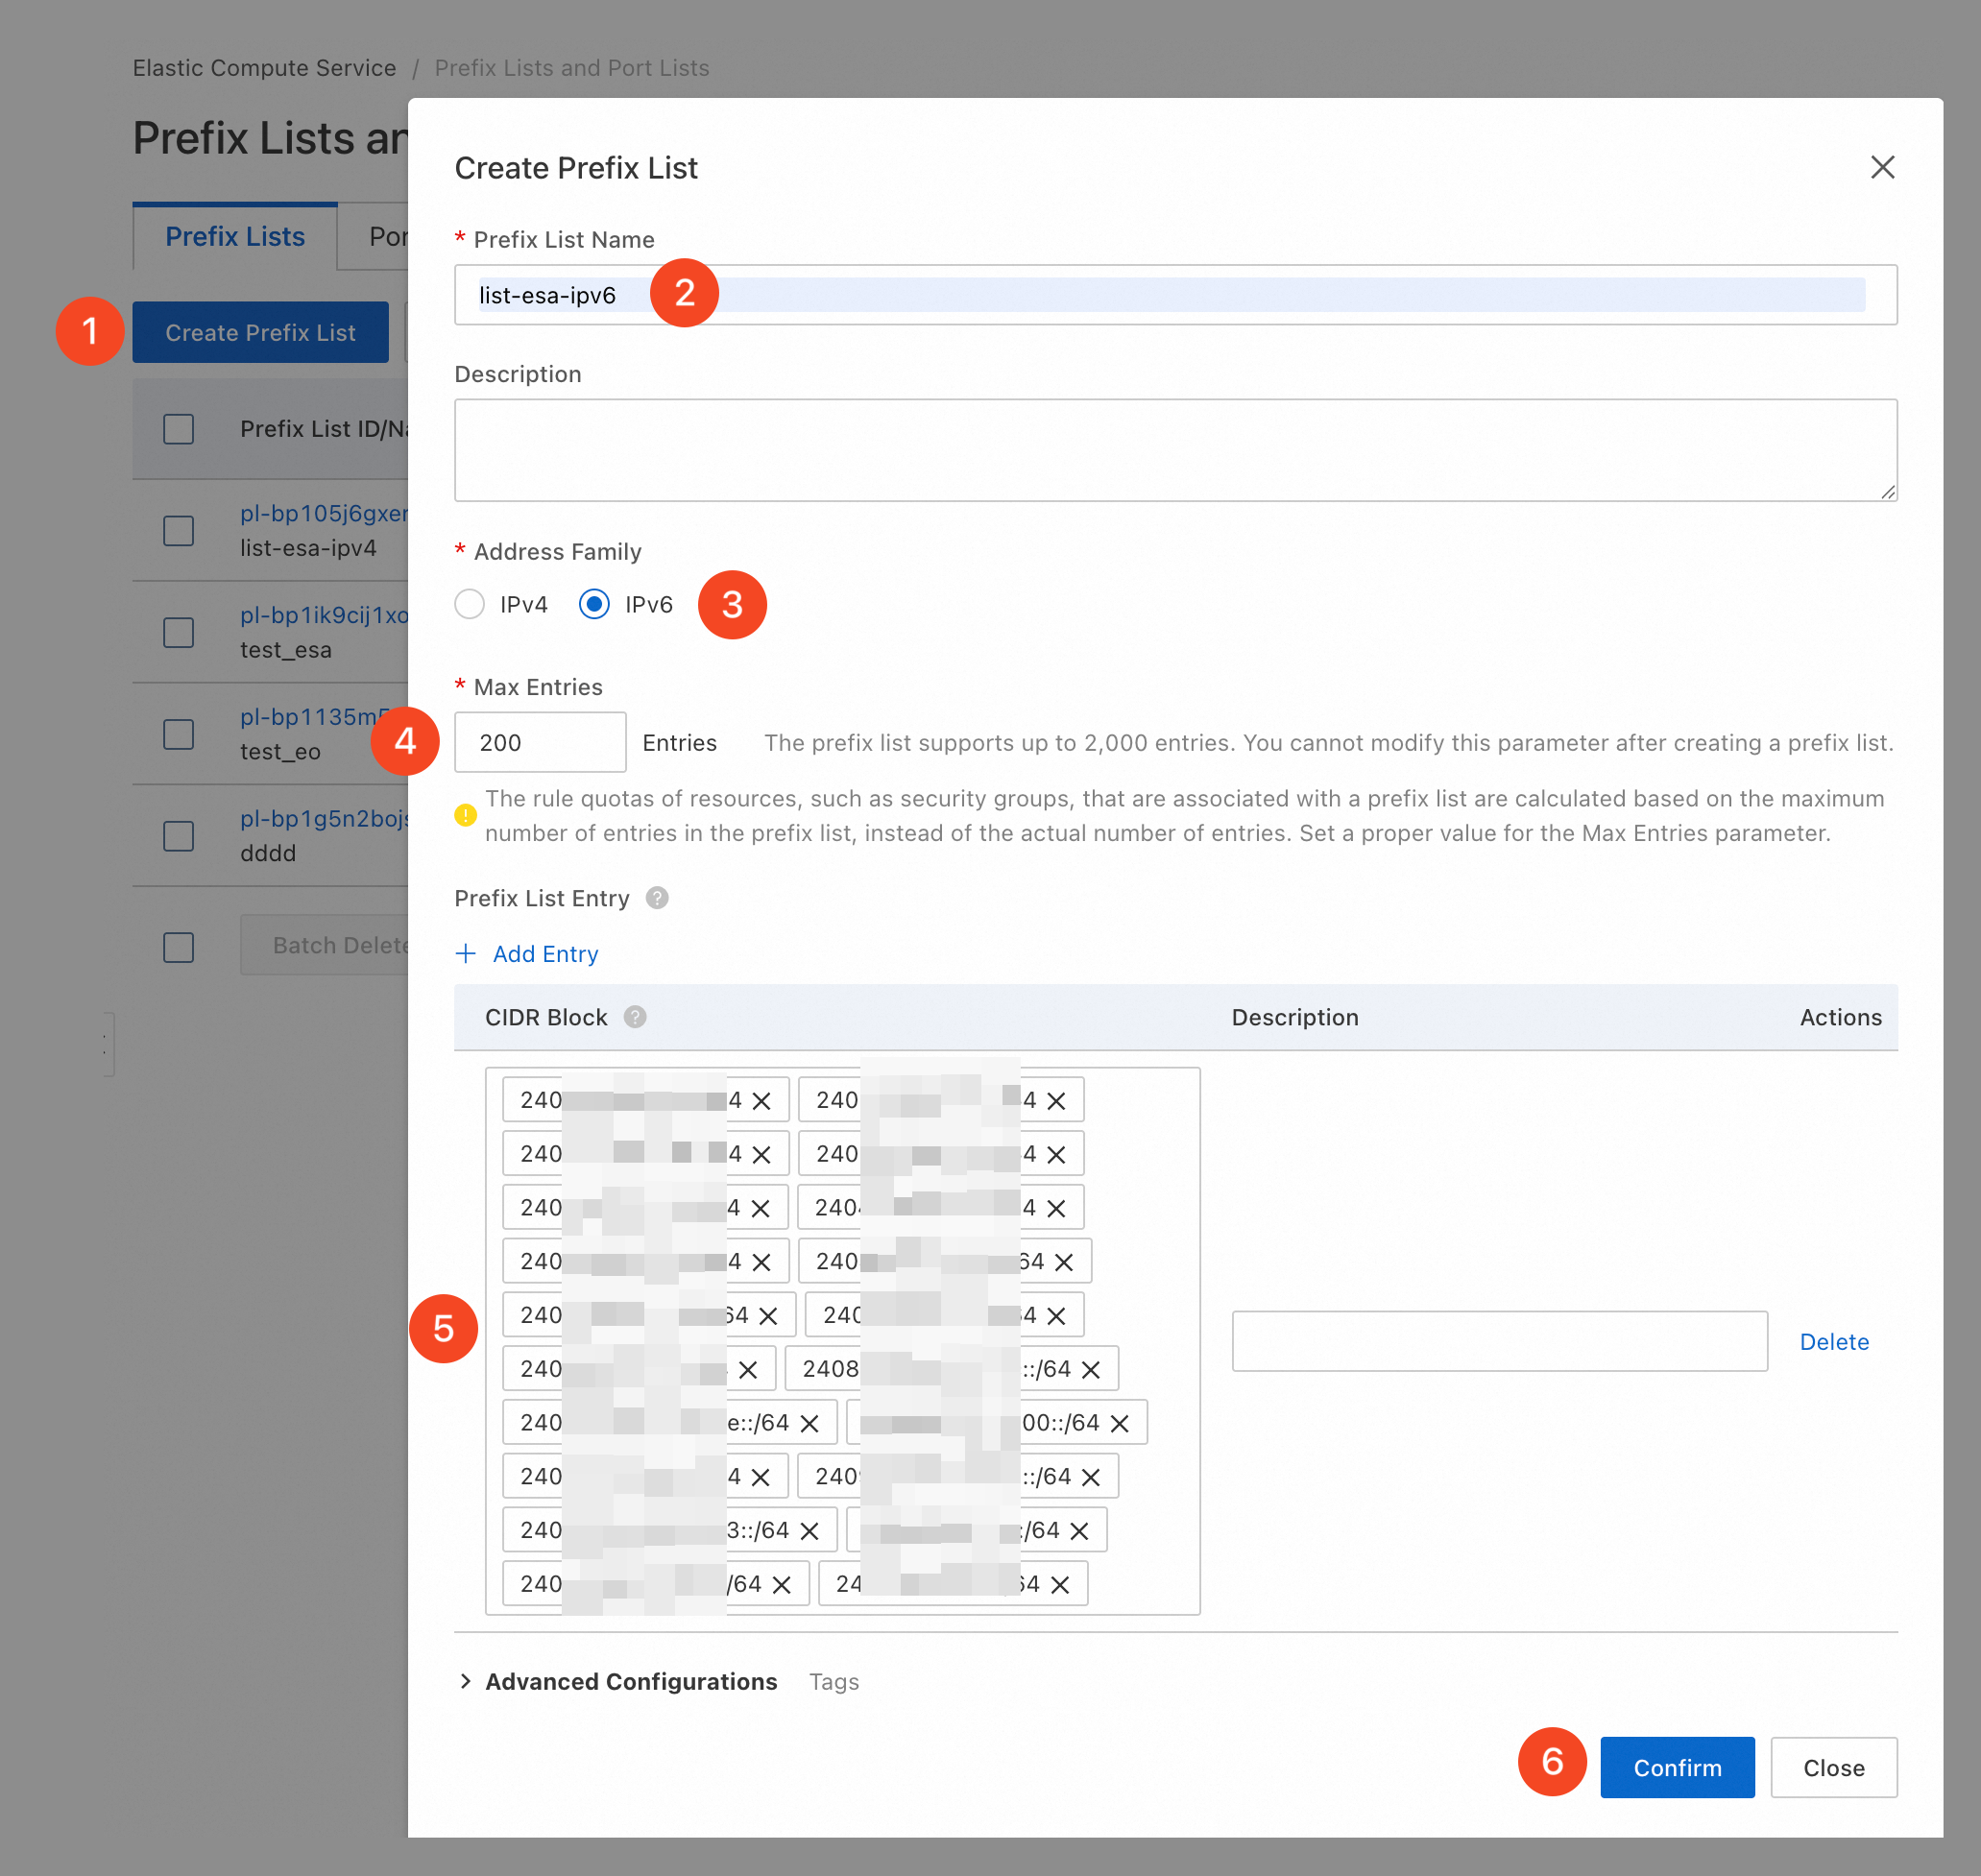
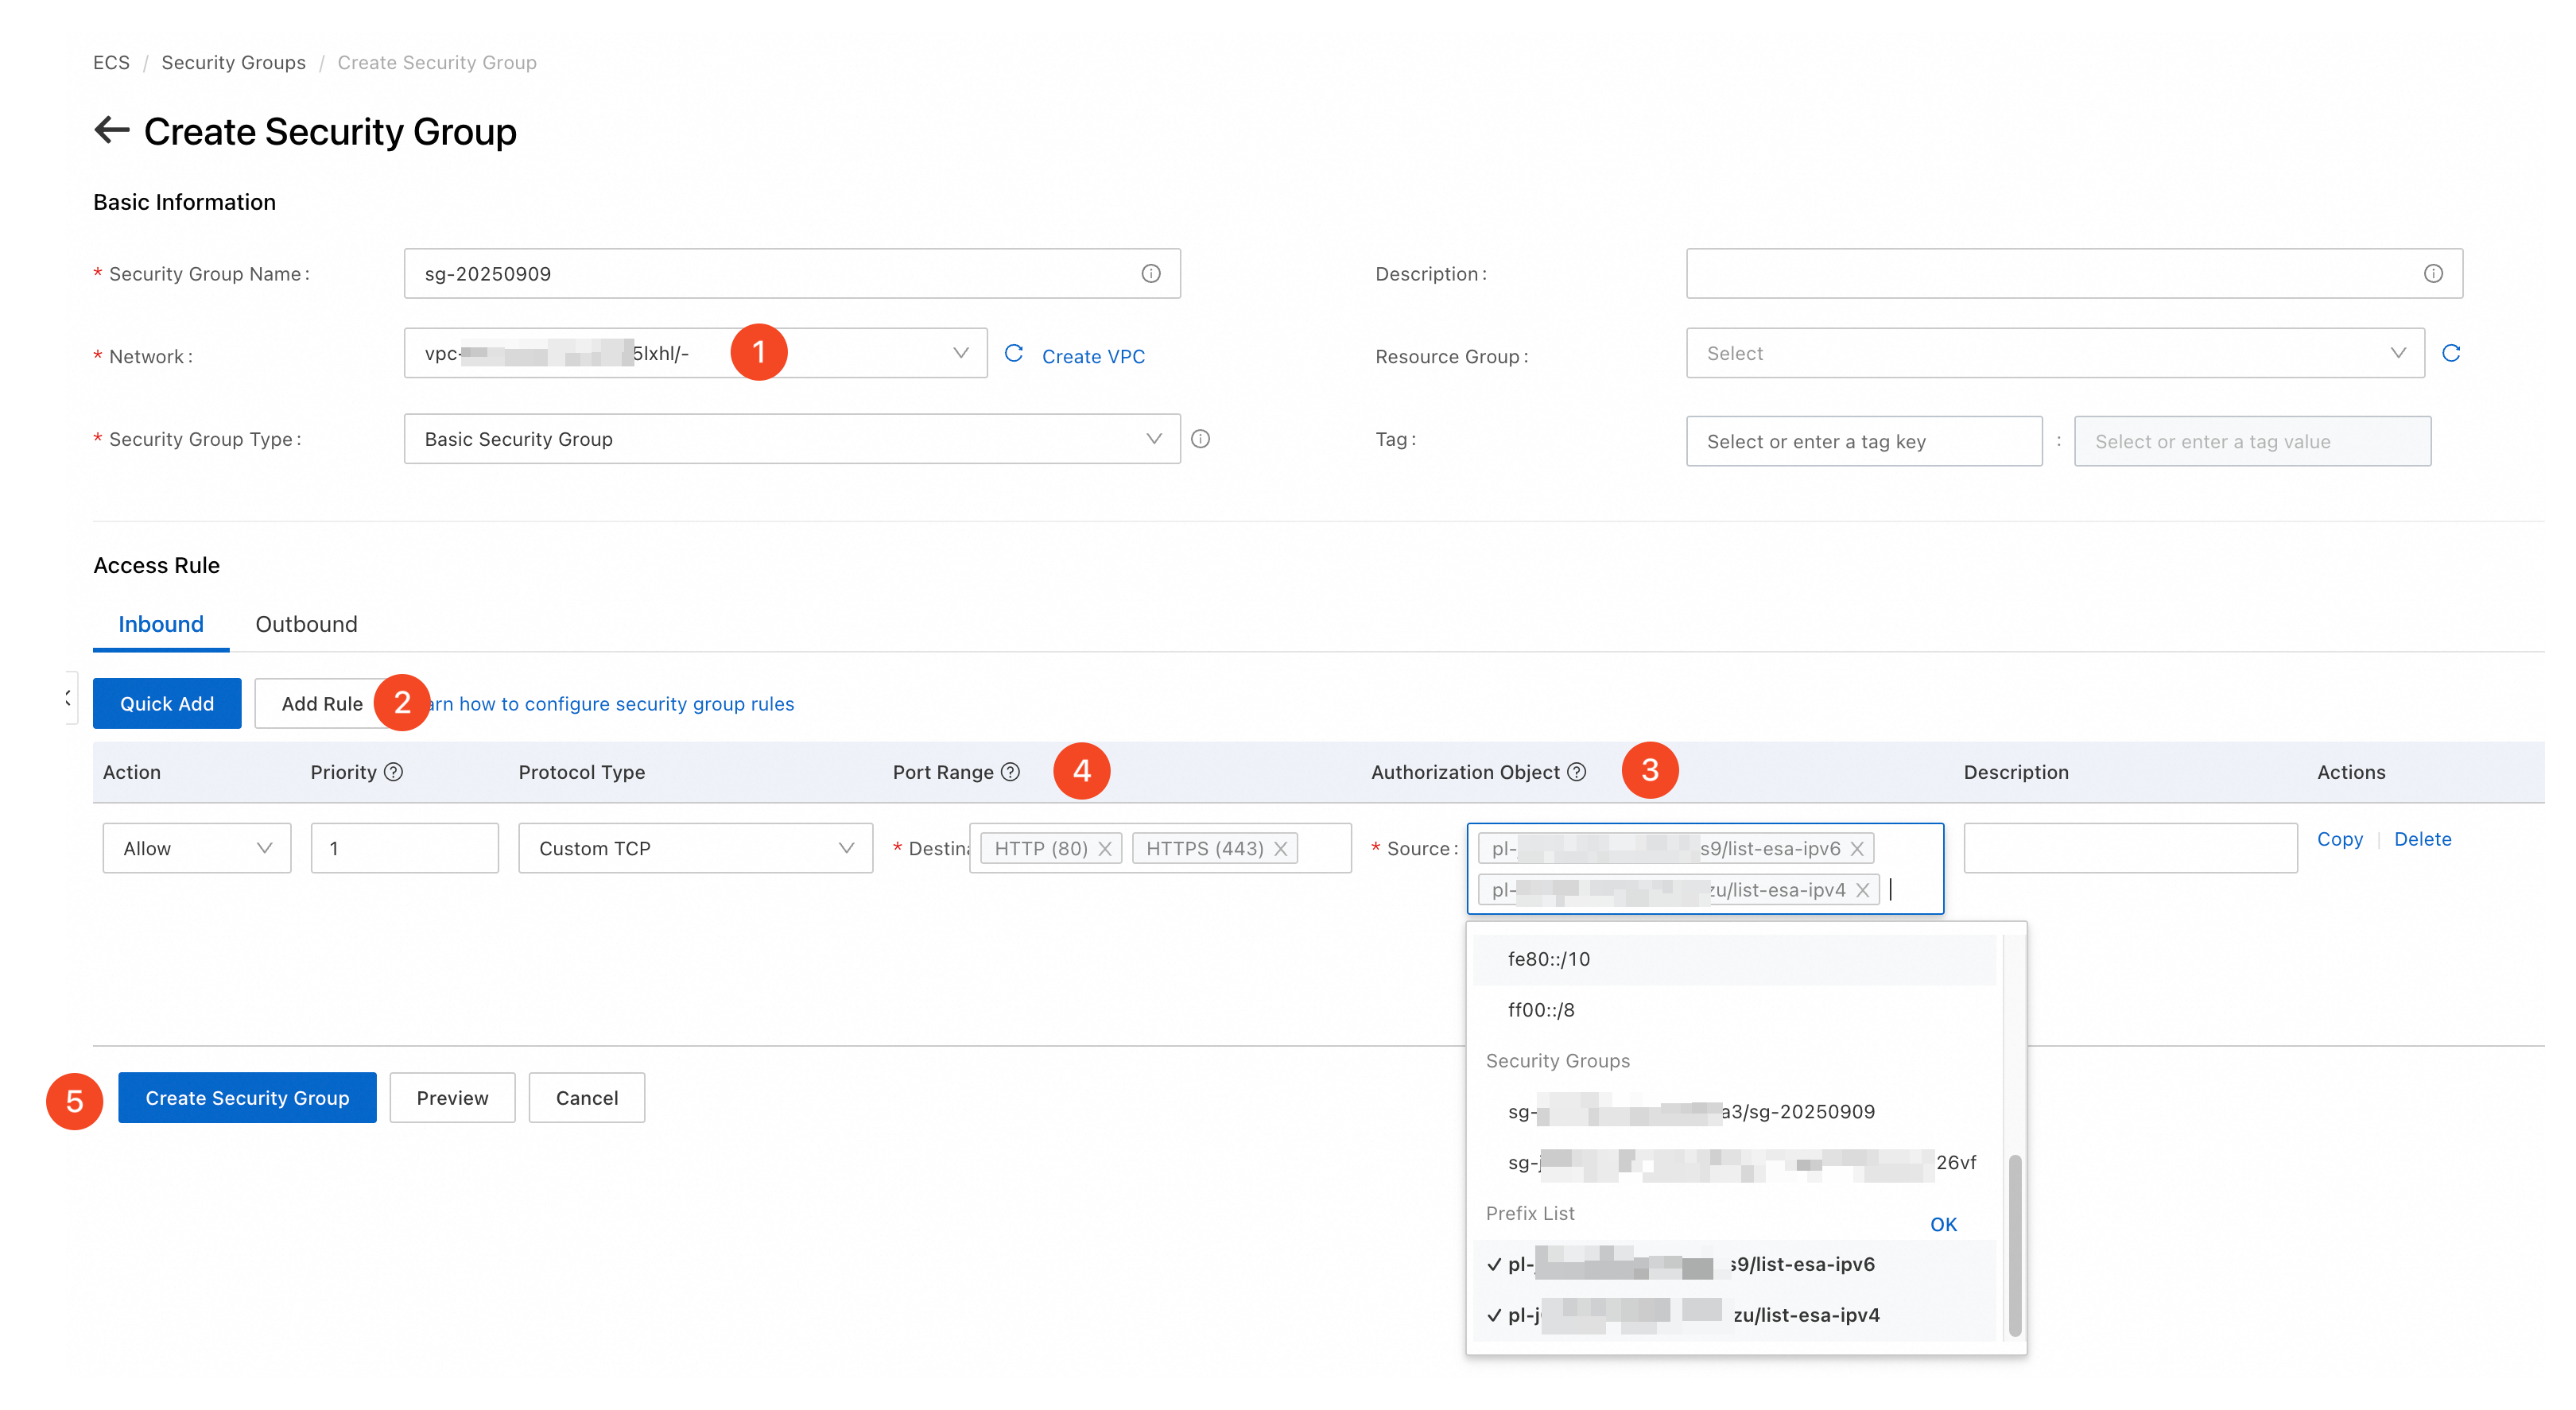
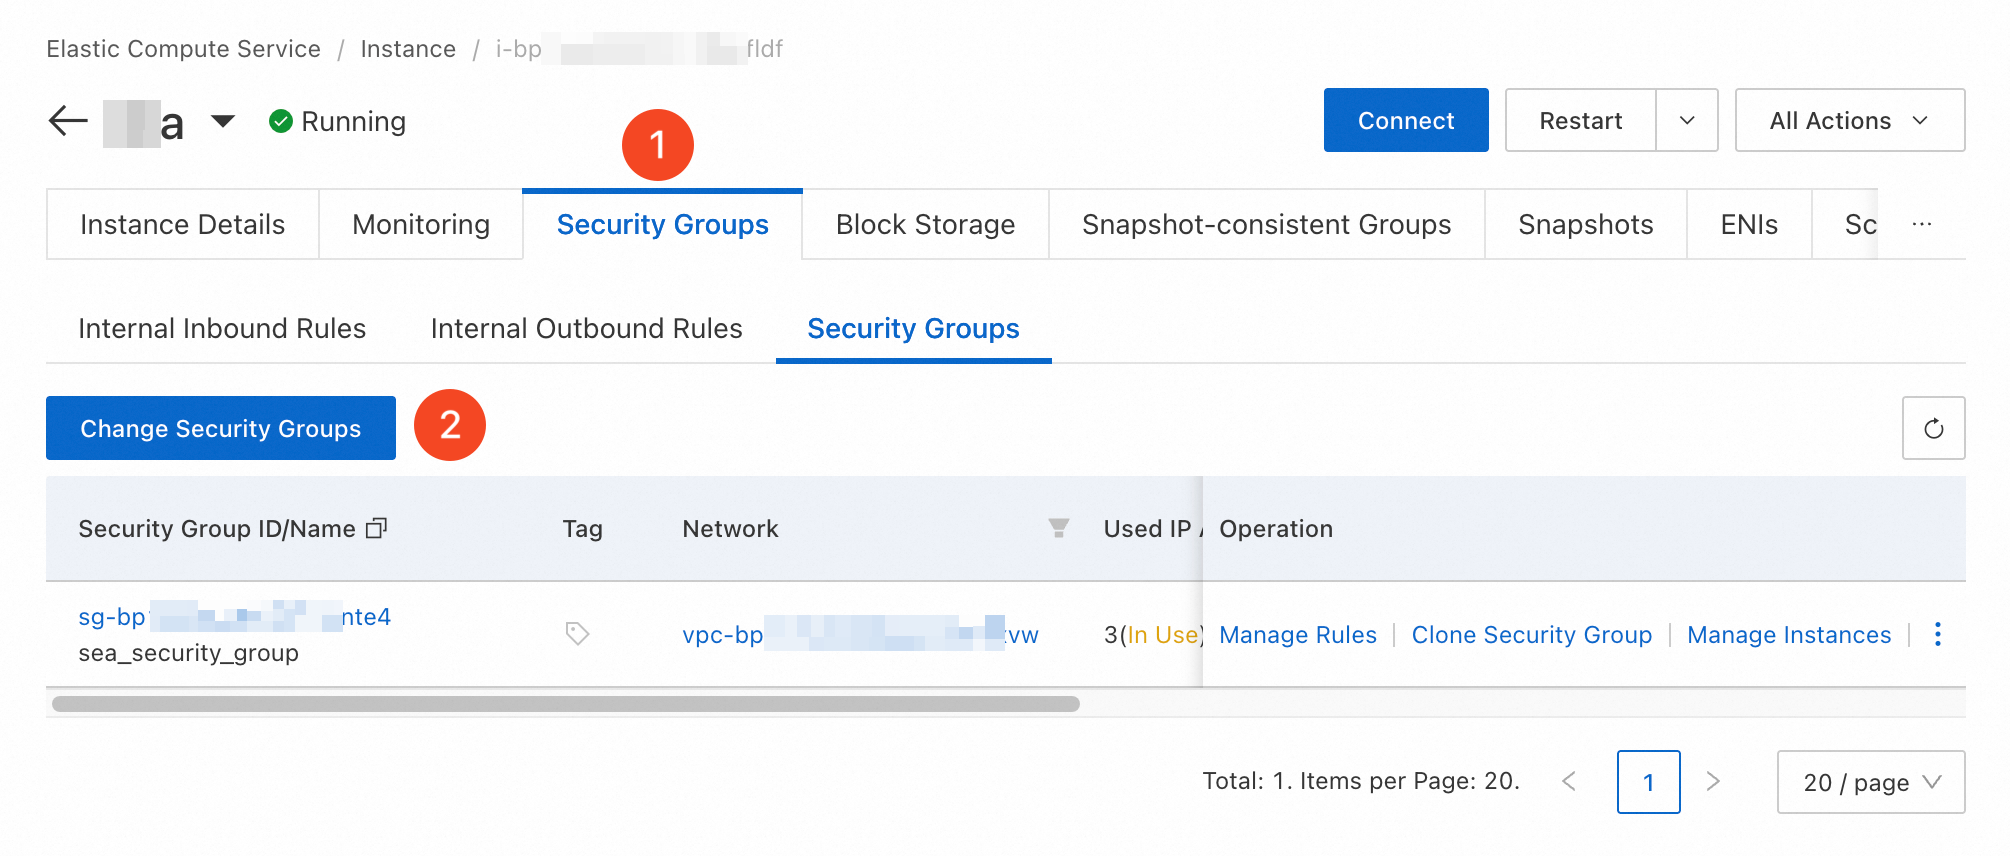
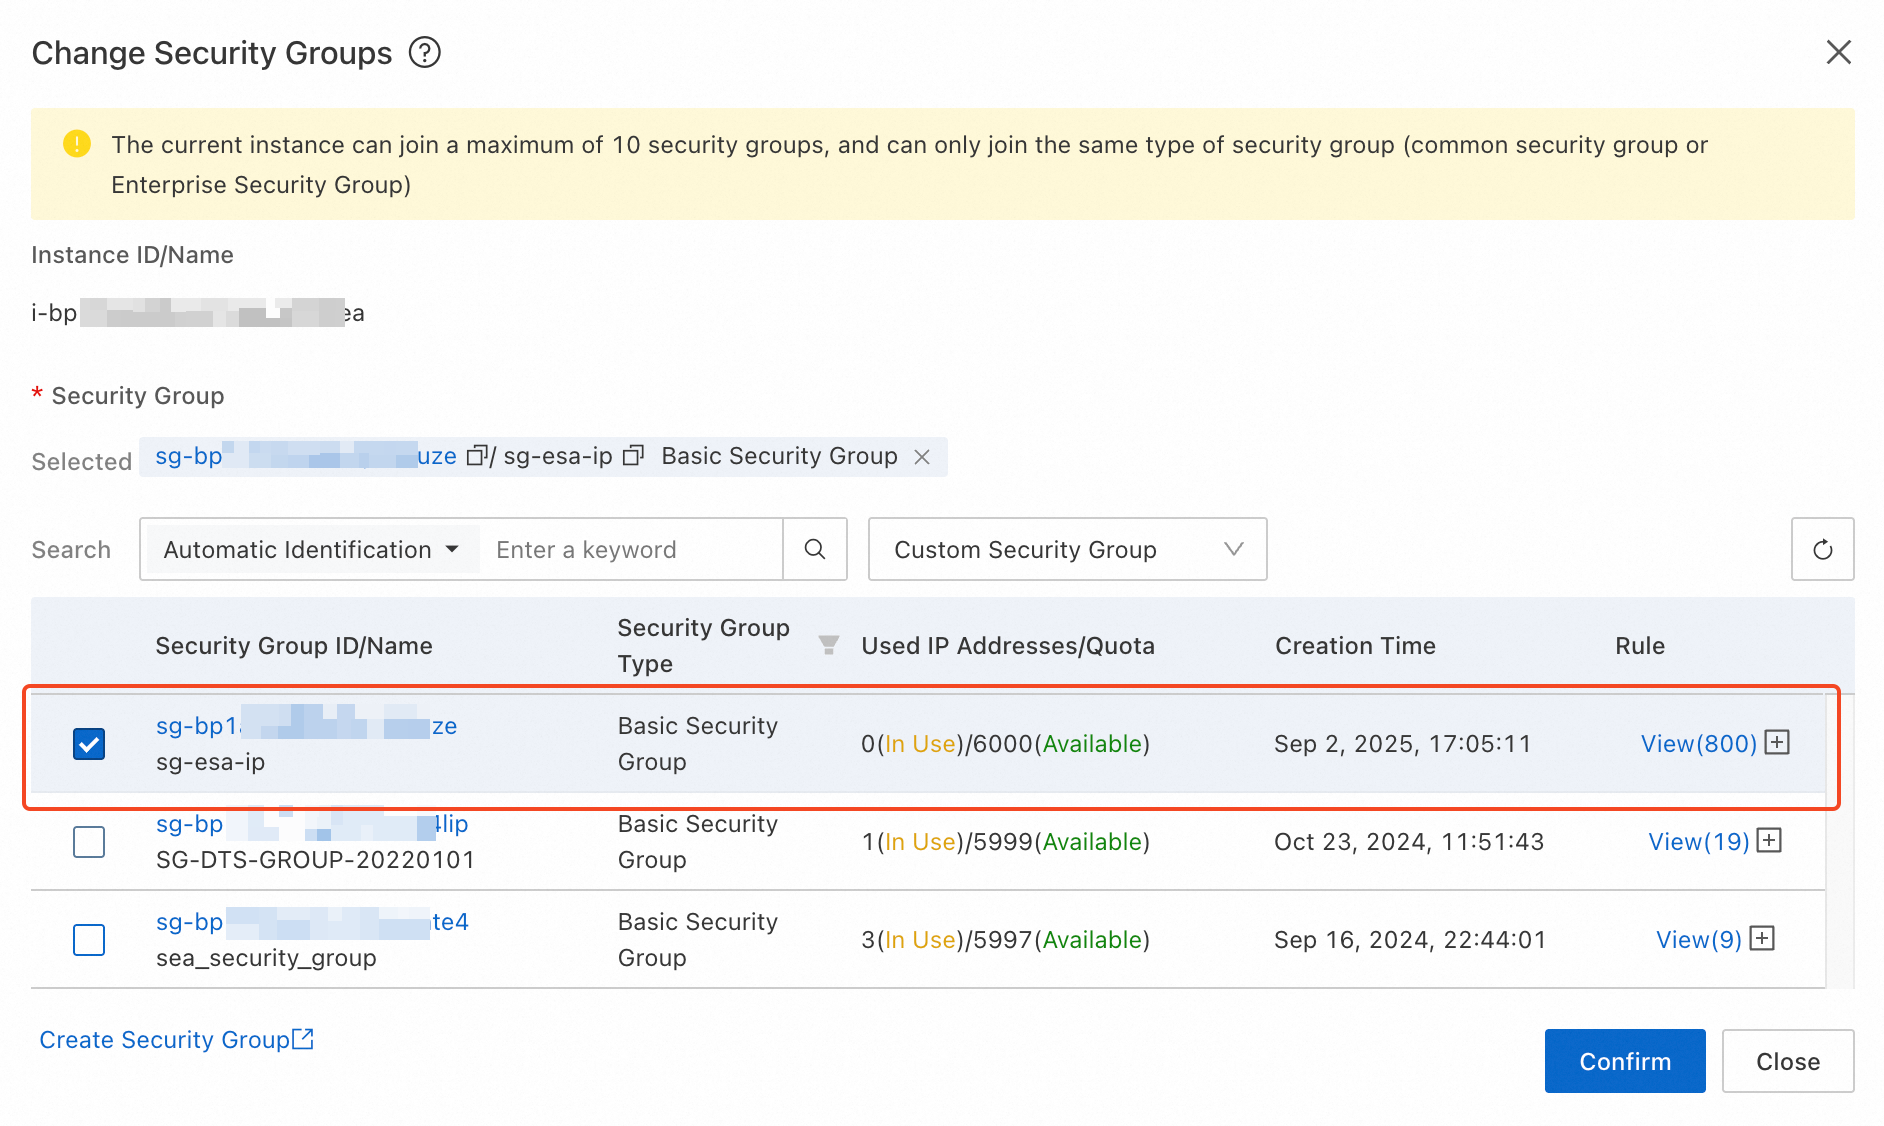
For on-premise or non-Alibaba Cloud origins, apply the whitelist directly on the host.
iptables:
# Allow ESA POPs (example - use your actual list)
iptables -A INPUT -p tcp -s 47.245.0.0/16 --dport 443 -j ACCEPT
iptables -A INPUT -p tcp -s 8.209.0.0/16 --dport 443 -j ACCEPT
# Add all other CIDR blocks...

# Drop everything else
iptables -A INPUT -p tcp --dport 443 -j DROP
firewalld:
firewall-cmd --permanent --new-ipset=esa-pops --type=hash:net
firewall-cmd --permanent --ipset=esa-pops --add-entry=47.245.0.0/16
firewall-cmd --permanent --ipset=esa-pops --add-entry=8.209.0.0/16
# Add all entries...

firewall-cmd --permanent --add-rich-rule='rule source ipset=esa-pops port=443 protocol=tcp accept'
firewall-cmd --permanent --add-rich-rule='rule port=443 protocol=tcp drop'
firewall-cmd --reloadImportant: Test firewall rules in a staging environment before applying them to production. A misconfigured DROP rule can take your origin offline.
When ESA POP addresses change, ESA notifies you by internal message or email. You must update your origin firewall or security group so ESA can keep reaching your origin.
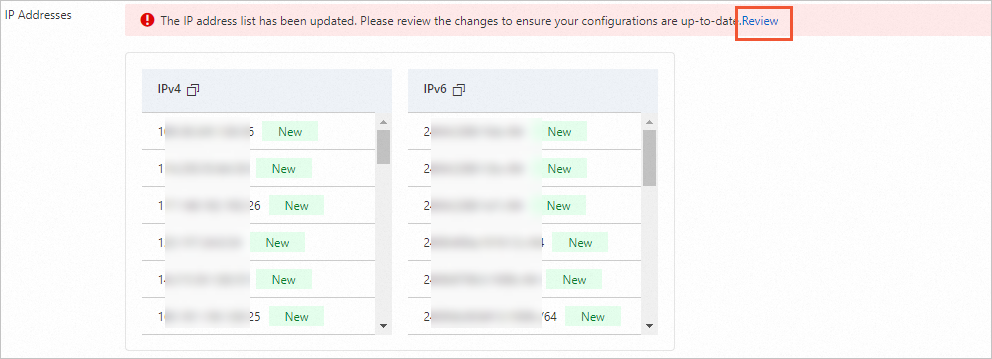
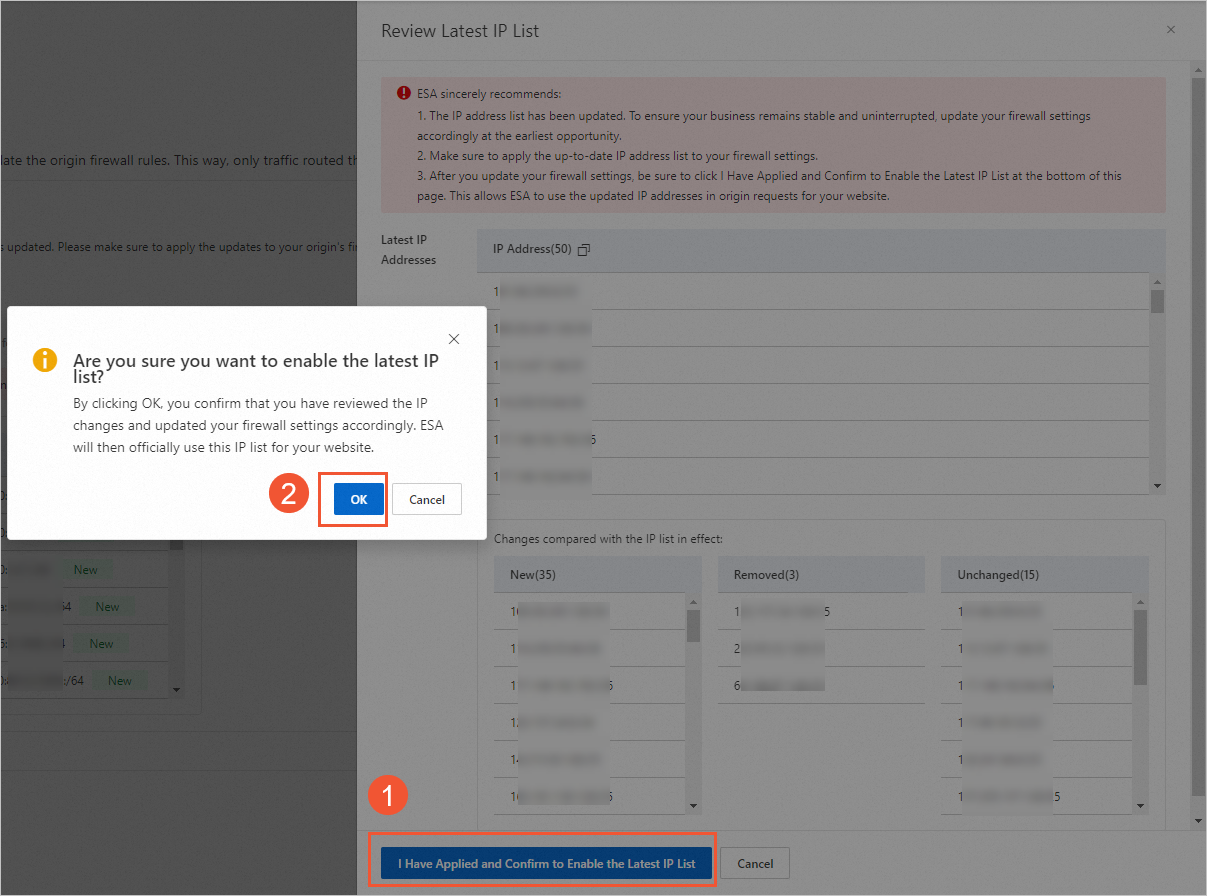
Note: The new list takes effect only after you confirm it. Until then, ESA keeps using the previously confirmed list. Confirm Cloud Firewall's auto-apply is on if you want this handled without manual steps.
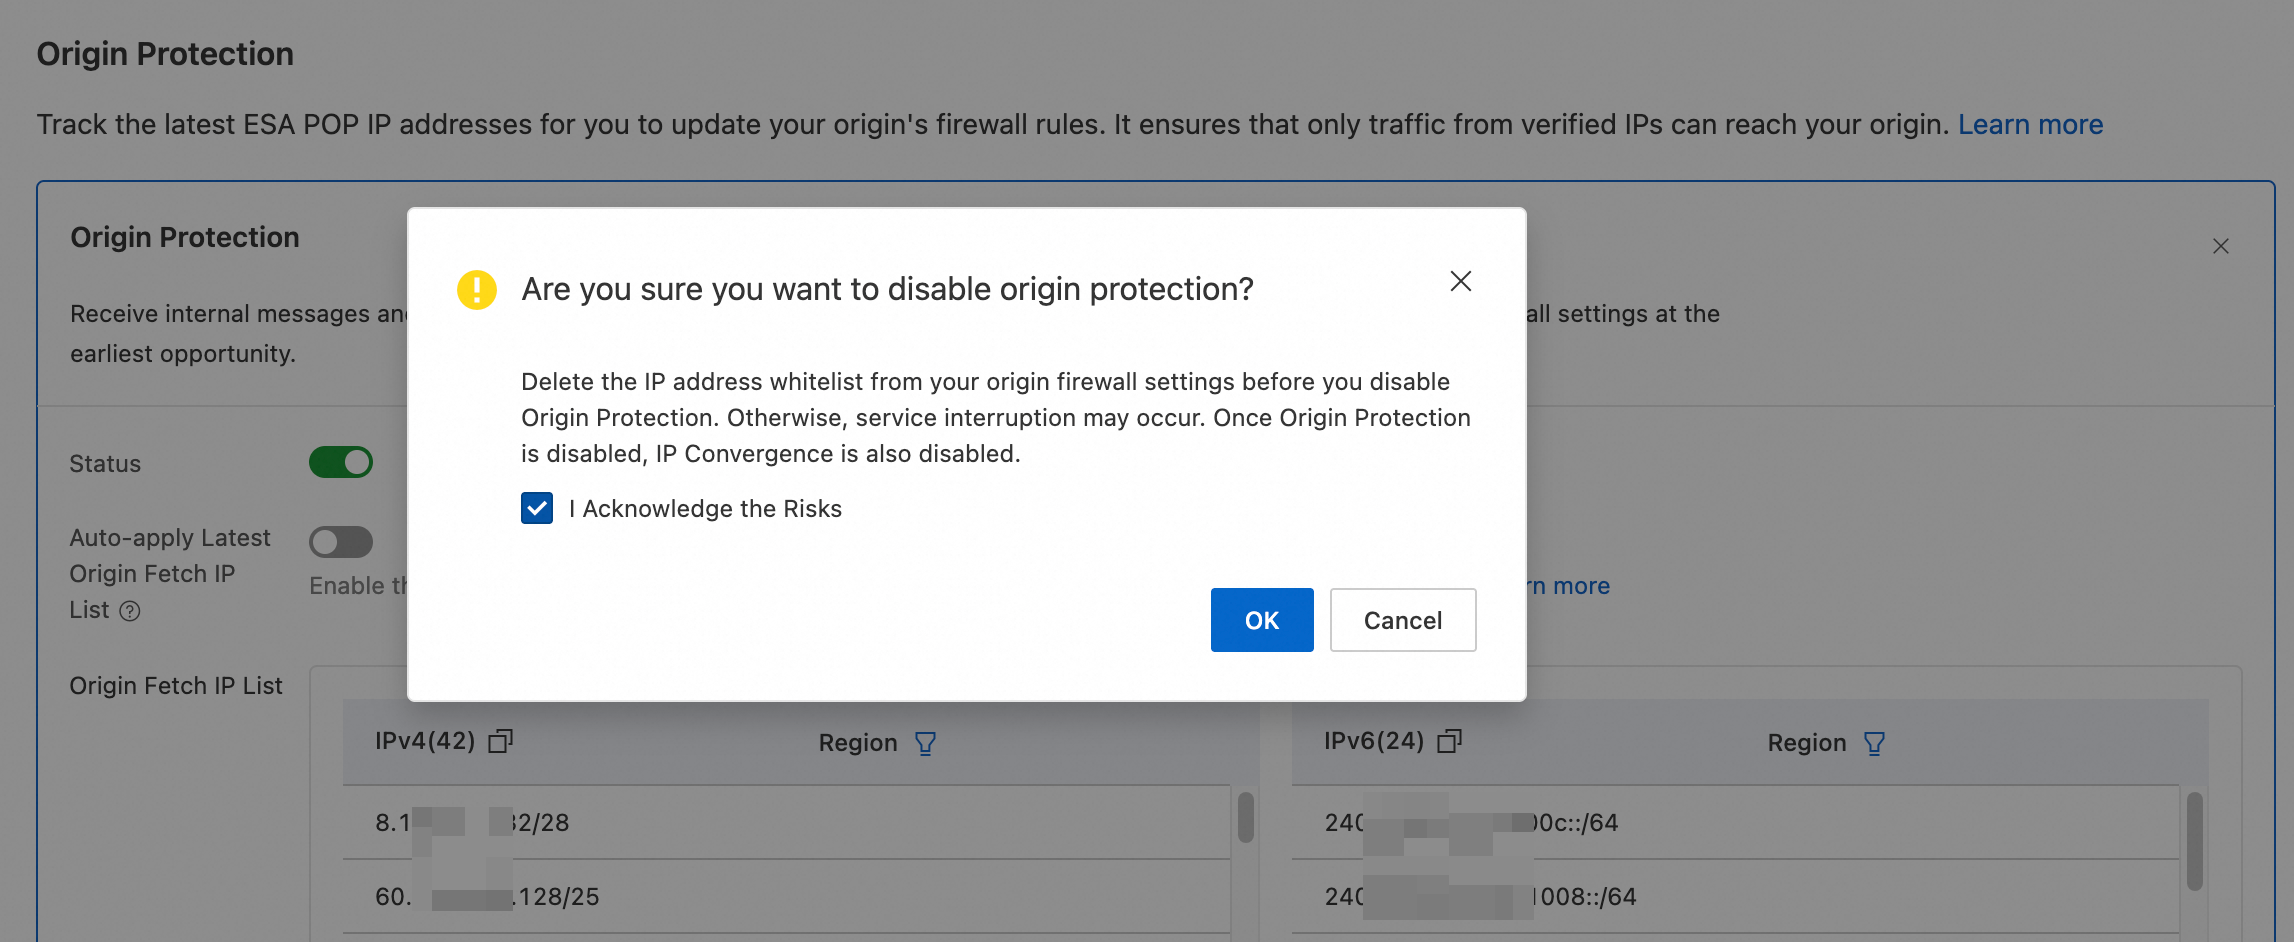
To prevent service interruptions, first remove the IP allowlist from your origin firewall, then disable Origin Protection - not the other way around.
The IP list from Origin Protection consists of converged node IPs, but fetch() calls from ESA Functions and Pages actually use pre-convergence node IPs. If a site called by fetch() does not have Origin Protection enabled, the real origin-pull IP of that fetch() is not in the converged list.
Heads-up: If your Functions call a site that also sits behind ESA, enable Origin Protection on that target site. If it is not on ESA, add the Functions egress IP ranges to the origin allowlist.
If Origin Protection returns more IP ranges than your origin can configure, ask your sales representative to enable back-to-origin convergence (Enterprise plan only). This further reduces the number of back-to-origin ranges.
Note: Fewer ranges means fewer back-to-origin POPs, which can reduce access quality. Enable this feature with caution.
If you move traffic off ESA - for example, by pointing DNS directly to your origin - update or remove the allowlist before disabling ESA. If the entry layer still only accepts ESA POPs but ESA no longer proxies traffic, legitimate requests get dropped.
A regional bank uses ESA to protect its online banking platform. Its PCI DSS framework requires that all inbound traffic to cardholder data environments be logged and filtered. Before Origin Protection, auditors flagged a gap: the origin remained accessible from untrusted networks. By whitelisting only ESA POPs at the load balancer, the bank demonstrated that 100% of inbound traffic was pre-filtered by ESA's security stack, and the audit finding closed immediately.
A mobile gaming company runs its servers behind ESA and is a frequent DDoS target. During one attack, the attackers found the origin IP through a forgotten staging subdomain and sent a 50Gbps flood directly to the game server, bypassing ESA entirely. After implementing Origin Protection, a repeat attack hit the whitelist and was dropped instantly - the servers never saw it. ESA stops attacks at the edge; the whitelist catches anything aimed at the door.
A B2B SaaS platform serves hundreds of customers from shared origin infrastructure, using ESA's WAF to enforce tenant-specific policies via the Host header. If an attacker finds the origin IP, they can craft the right header and reach any tenant directly. Origin Protection forces all traffic through ESA's policy engine, so tenant isolation cannot be circumvented at the origin.
| Plan | Origin Protection |
|---|---|
| Entrance (USD 0/month) | Not supported |
| Pro (USD 15/month) | Supported |
| Premium (USD 249/month) | Supported |
| Enterprise (custom) | Supported |
The Entrance plan does not include this feature, since POP IP whitelisting requires the multi-tier cache architecture that Pro and above provide.
With Origin Protection configured, your origin is only accessible through ESA.
But what if your users are in mainland China and your origin is in the US or Europe? You then face a compliance puzzle (data residency) and a performance puzzle (cross-border latency). Cross-border acceleration solves both, and it is the topic of the next article in this series.
Resources:
ESA Unlocked: Tiered Cache - Break Through the Cache Hit Ratio Ceiling

8 posts | 1 followers
FollowBryan, Zhang - October 5, 2026
ESA Big Fan - June 5, 2026
Bryan, Zhang - August 31, 2026
Bryan, Zhang - June 23, 2026
Kidd Ip - September 15, 2025
Bryan, Zhang - October 7, 2026
8 posts | 1 followers
Follow Edge Security Acceleration (Original DCDN)
Edge Security Acceleration (ESA) provides capabilities for edge acceleration, edge security, and edge computing. ESA adopts an easy-to-use interactive design and accelerates and protects websites, applications, and APIs to improve the performance and experience of access to web applications.
Learn More Edge Node Service
An all-in-one service that provides elastic, stable, and widely distributed computing, network, and storage resources to help you deploy businesses on the edge nodes of Internet Service Providers (ISPs).
Learn More Secure Access Service Edge
An office security management platform that integrates zero trust network access, office data protection, and terminal management.
Learn More Link IoT Edge
 allows for the management of millions of edge nodes by extending the capabilities of the cloud, thus providing users with services at the nearest location.
Learn MoreMore Posts by Bryan, Zhang

